A direct exe link where a store listing should be
You search for a program, a game mod or a cracked tool. Instead of an app store or the developer's own site, you land on a page with one button that downloads the file directly. That single-button page is how an exe download scam starts. No store review stands between the page and your machine, and nothing confirms the file came from the developer and not from whoever built the page.
Minecraft mods and cracked game clients are two searches that lead here. Both already teach users to expect a direct download outside any official store, so a page offering a popular mod or a paid game's cracked version doesn't look out of place, even when it was built only to deliver a dropper.
What we found in 8 sites we analysed
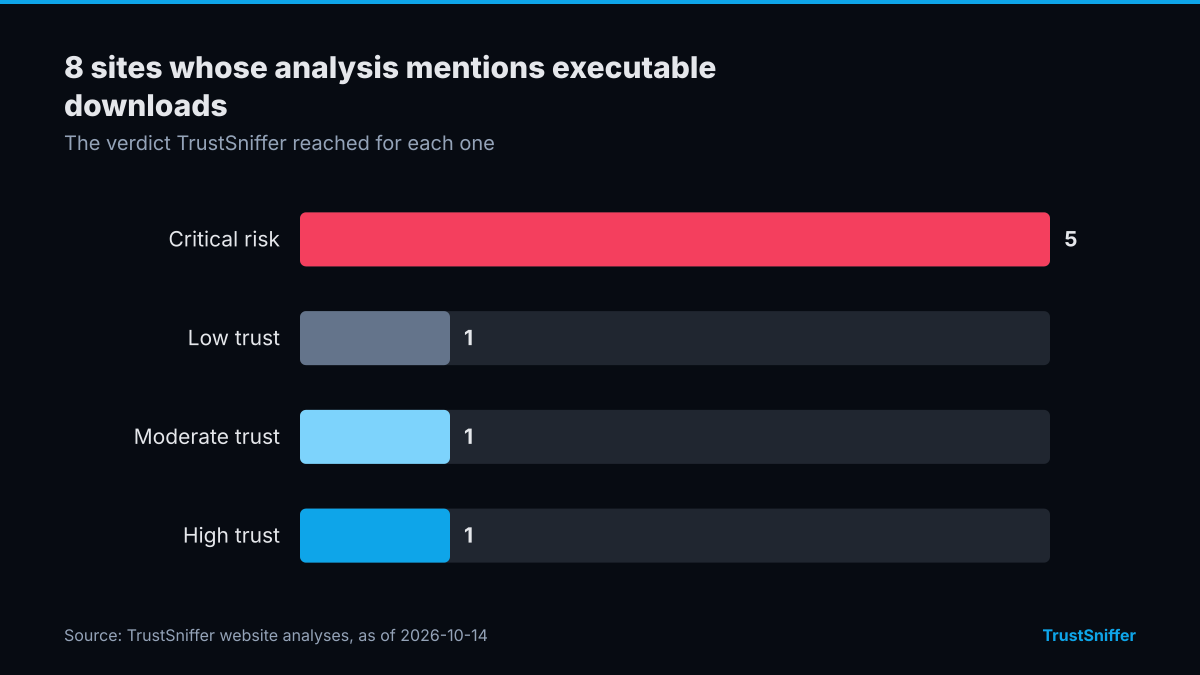
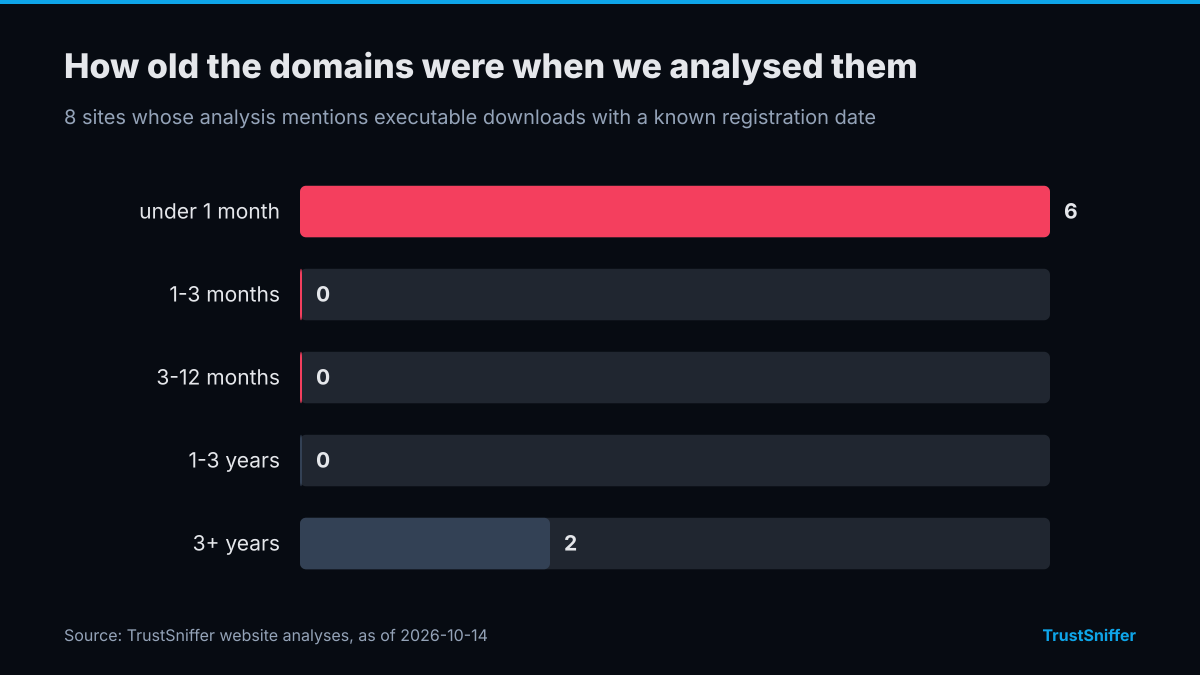
TrustSniffer has analysed 8 sites whose analysis mentions executable downloads. 6 of them (75%) were rated critical risk or low trust (5 critical risk, 1 low trust), and the other 2 scored higher. 6 of the 8 with a known registration date (75%) had a domain under a year old when we analysed it, and the median age was under a month.
4 of them resolved to Cloudflare, Inc. networks, the most common provider in the set. 6 of 8 (75%) were already flagged by at least one VirusTotal engine when we checked.
Some of the sites we analysed, each linked to its full report:
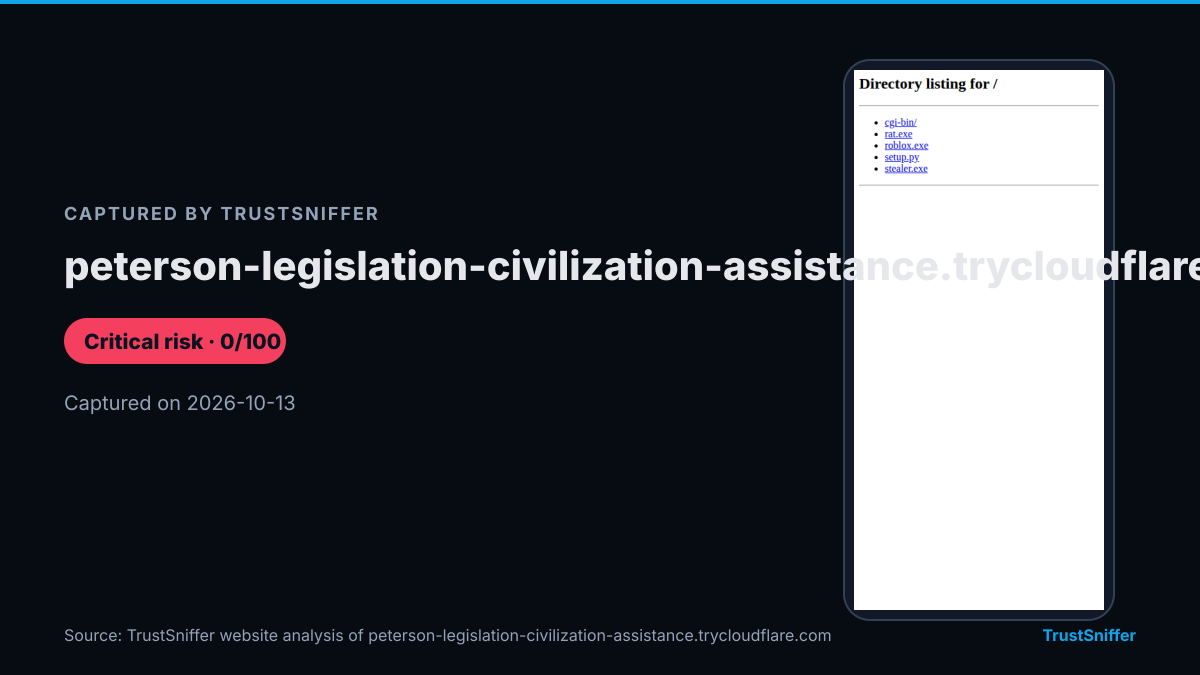
- peterson-legislation-civilization-assistance.trycloudflare.com: rated critical risk (0/100), domain under a month old when analysed.
Why the archive needs a password you type in yourself
The file rarely arrives as a bare .exe. It is more often inside a zip or rar archive that needs a password, and the password sits in plain text on the same download page. The password stops the automated scanners along the way (the ones a browser, mail service or file host runs) from opening the archive and reading what is inside. Your own antivirus only gets to see the file after you type the password and extract it, so every earlier check has already been skipped.
What runs next is a dropper: a small program that does little on its own except connect over the network, download a second file and run it. The .exe you launched is only the first stage. The same structure turns up in .jar files and in Android APKs installed outside an app store (sideloading), because both skip the review a store or package manager would apply.
Why the hosting behind it disappears within days
A dropper's first stage needs little infrastructure, only a page that stays live long enough to be shared and clicked. Free static hosting lets anyone publish a working download page in minutes, with no review of what gets uploaded. Cloudflare Pages and GitHub Pages work this way, and so do Firebase Hosting and free website builders. The file itself can sit in object storage behind a plain link, apart from the page that points to it; Amazon S3, Azure Blob Storage and Cloudflare R2 all allow this. Plenty of honest sites use these services. Scammers pick them because the free tiers are quick to set up and don't check uploads. When one copy is taken down or blacklisted, a near-identical page can go up on another free host the same day, which is why a blacklist built from yesterday's reports keeps missing today's domain. The download links in this set also sit on cheap, disposable extensions like these:
- .top, .icu and .cyou domains
- .sbs, .rest and .space domains
- .shop, .click and .link domains
Who ends up on the download page
Most people who land here want something an app store won't give them for free: a cracked paid game, a mod for a game like Minecraft, or a tool packaged as a .jar they expect to run outside any package manager. Android users sideloading an APK belong to the same group, since sideloading exists to skip the official store's review. Each of these four habits is ordinary. A scam page exploits the fact that none of them comes with a built-in check. For figures beyond a single page, our Risk Index shows current risk levels across what we have analysed.
Four checks before you run the file
The checks below apply to any direct download page, starting with the fastest.
If any check comes back unclear, don't run the file. Get the program from its official page or an app store instead, where the review step you were trying to skip has already happened.
- Compare the domain with the program's real home. If it doesn't match, if it is a generic subdomain of a free host, or if it is a short domain with no visible link to that program, the page is not the vendor's own, however polished it looks.
- Check whether the archive needs a password copied from the page. Legitimate installers don't come in an archive you have to open with a password from the download page; a page that works this way is hiding the file from scanners.
- Before opening the file, check it with a multi-engine file-scanning service. You can upload the file itself, or paste its hash (a short fingerprint of the file that your operating system can compute). The service shows how many antivirus engines flag it. Look at that count: a brand-new dropper is often missed by many engines, so one clean result proves little.
- Paste the domain into the website checker. It gives the site a trust band, from critical risk to high trust. A critical-risk or low-trust band means close the page. If the band is moderate, or you can't tell what it means for this download, don't run the file.
For the wider data on this pattern, our direct executable download analysis looks at 19 sites and their scores. The script that does the fetching is explained in script droppers, and the phone version of the same delivery in Android APK sideloading.


