The send-more-to-get-more promise
You saw a post, a hijacked livestream overlay or a direct message with a known exchange's logo or a public figure's name on it. It said that whatever you send to a listed address comes back larger. Paying before any reward arrives, when the only guarantee of a return is a stranger's promise, is what a crypto giveaway scam looks like in practice.
What we found in 13 sites we analysed
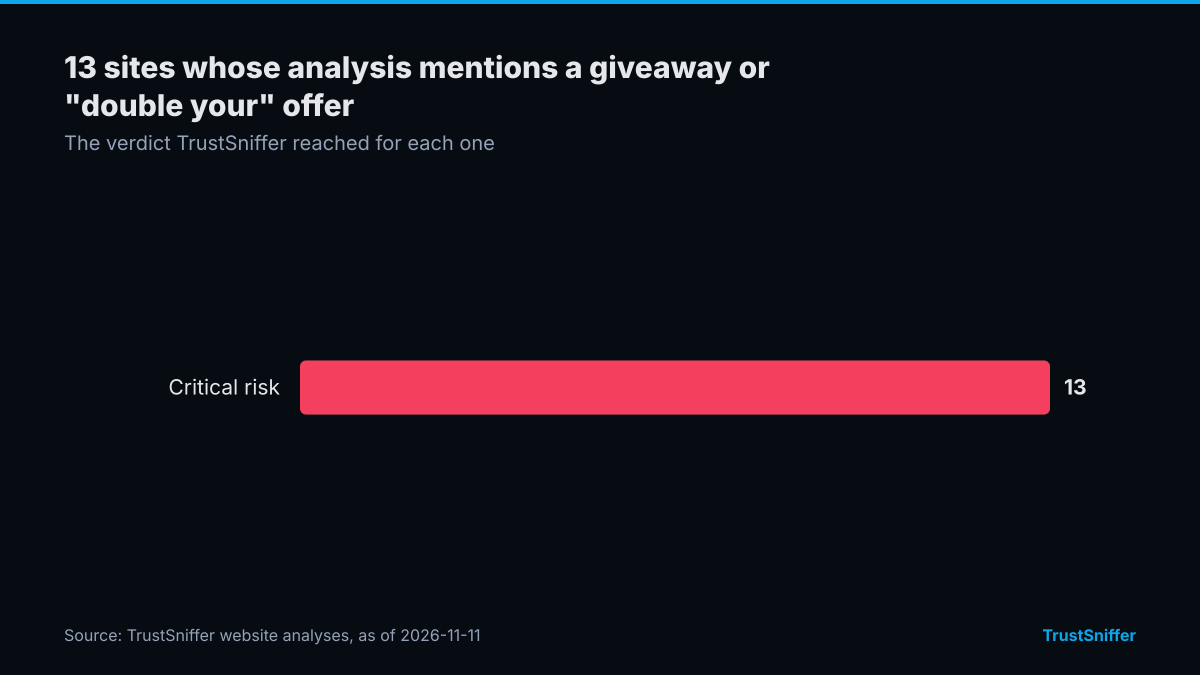
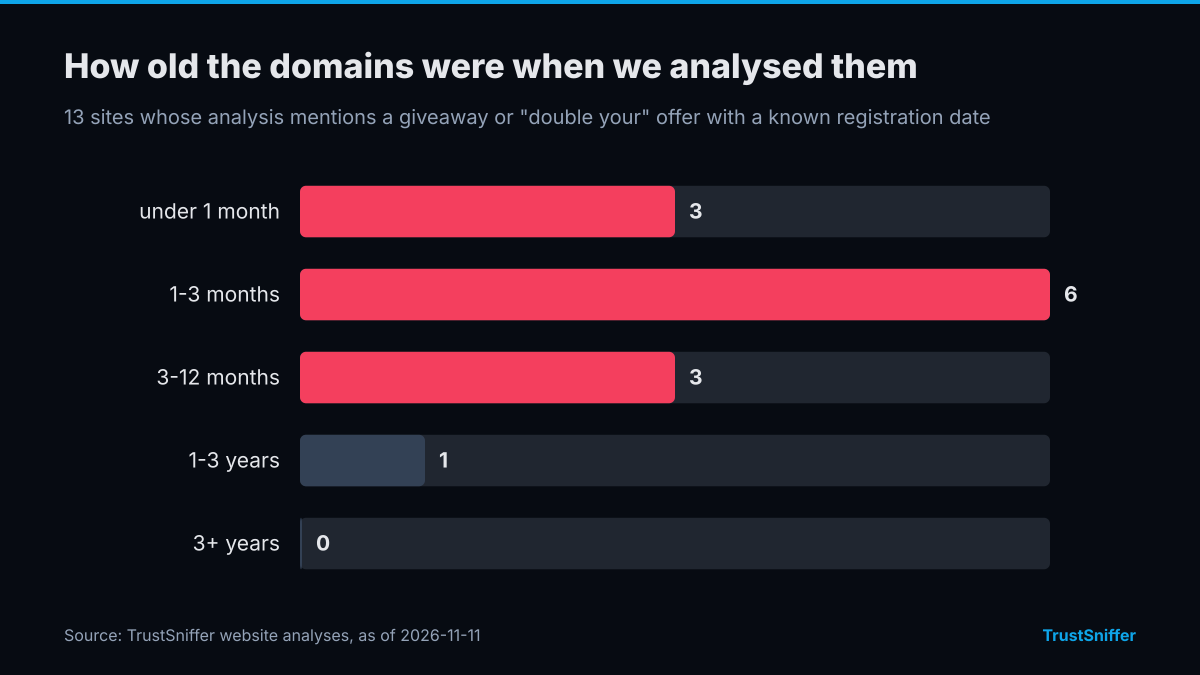
TrustSniffer has analysed 13 sites whose analysis mentions a giveaway or "double your" offer. 13 of them (100%) were rated critical risk or low trust: 13 critical risk. 12 of the 13 with a known registration date (92%) had a domain under a year old when we analysed it, and the median age was 2 months.
The networks they most often resolved to were Cloudflare, Inc. (8). 12 of 13 (92%) were already flagged by at least one VirusTotal engine when we checked.
Some of the sites we analysed, each linked to its full report:
- token-giveaway-live.netlify.app: rated critical risk (0/100), domain under a month old when analysed.
- 4burn-giveaway.netlify.app: rated critical risk (0/100), domain 8 months old when analysed.
- meme-giveaway.fun: rated critical risk (0/100), domain 2 months old when analysed.
- giveaway-piggycoincom.pages.dev: rated critical risk (0/100), domain 1.8 years old when analysed.
Why a transfer to that address doesn't come back
A wallet address has no function that sends money back automatically or multiplies a deposit. Tokens such as USDT are recorded by a small program on the blockchain called a token contract. On Ethereum (under its ERC-20 standard) and on TRON (under the matching TRC-20 standard), that contract keeps one balance per address, and a transfer adds to the recipient's existing balance. Nothing in that step triggers a return payment or a reward.
Funds leave an address only when someone approves the transfer with that address's private key, the secret code that works like the wallet's password. In a giveaway scam, the operator who set up the address and the post holds that key. The exchange, celebrity or project whose name and photo appear in the offer does not have it and has no say over what moves.
A borrowed logo and an address with no history
Made-up example: a giveaway post uses a real exchange's logo, prints a wallet address underneath and promises that anything sent there comes back multiplied. The address has no connection to the exchange. It was created for that post alone. The giveaway ends when the operator stops answering messages, and the sender is left with a transfer that has already settled and cannot be reversed.
Confused with a real token airdrop
A genuine token airdrop sends tokens to addresses that already qualify, based on past activity or a snapshot the project took in advance. The recipient sends nothing first. A giveaway scam reverses that order and asks for a deposit before any reward appears, whatever platform the message showed up on and whatever name is attached to it. Payment before reward is the detail to check, however official the page looks.
Checking the address before you send anything
Three checks take a few minutes and need nothing but the address in the post.
- Confirm the token contract. Genuine USDT runs from one contract per network: TR7NHqjeKQxGTCi8q8ZY4pL8otSzgjLj6t on TRON and 0xdAC17F958D2ee523a2206206994597C13D831ec7 on Ethereum. A token calling itself USDT from any other contract is not Tether's USDT, whatever the giveaway page calls it.
- Look up the address on the matching explorer. Tronscan shows the sender, recipient, token contract, amount and time for a TRON address or transaction hash; Etherscan shows the same fields on Ethereum.
- If the address is on Ethereum or TRON, run it through TrustSniffer's wallet checker. It returns a risk assessment for that address. A high-risk result means do not send; a low-risk result still does not make it safe to pay first, because a genuine giveaway does not ask for payment. If the offer is hosted on a website, check the domain with the website checker. It produces a report on the site, which you can use to decide whether to trust the page making the offer.
If the contract doesn't match, or the explorer shows an address that only collects deposits and has no record of paying anything back to senders, don't send anything. Once a transfer settles, nothing in the token mechanics described above returns it. If the result is unclear (a brand-new address with no history, for instance), don't send a test amount to find out. A real giveaway does not require a payment to deliver a prize.
Can you get crypto back from a giveaway scam?
Usually not from the sender's side. The transfer settled the moment it confirmed, and only the holder of the receiving address's key can move the funds. What you can do is report the address to the exchange or platform where the post appeared and keep the transaction hash. Be ready for a second approach: people who offer to recover giveaway losses for an upfront fee are running the crypto recovery scam.
Giveaway posts and fake airdrop pages borrow the same trust in a familiar name. A page that asks you to connect and sign instead of sending a deposit is the wallet drainer version of the same trick.


