Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
aave-fi.info shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 16 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 24 reports; shared hosting inflates reports | Clear |
| Domain age | 3 months oldMost scam domains are under a year old | Risk |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | CLOUDFLARENETServer in US | Noted |
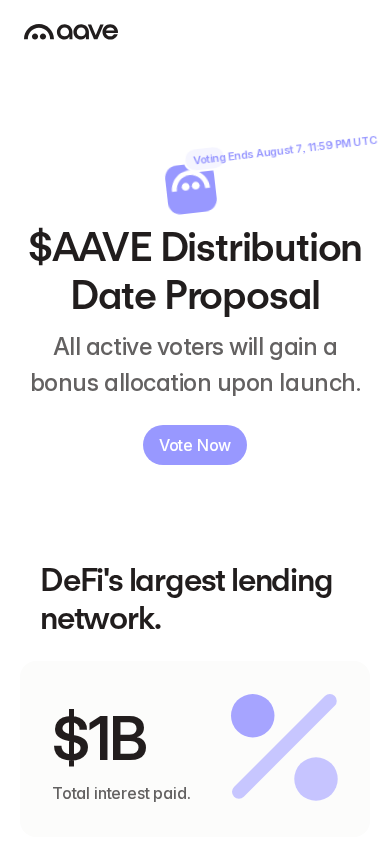
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Aave-fi.info is a newly registered .info website whose name pairs a recognisable decentralized-finance lending brand term with a "fi" suffix, which positions it as a crypto-finance or DeFi-themed service. The analysis could not extract any readable product, pricing or company content from it. What was observed is a front end that rebuilt itself heavily once interaction began and made many background calls to third-party services, which is typical of a wallet-oriented web application. Its apparent purpose is therefore a DeFi-style interface that invites visitors to interact with digital assets.
Scam/Impersonation Risk
Hard contradictory signals are present. Several major security vendors independently classify the domain as malicious, and a further group rates it suspicious, which amounts to a confirmed blacklist listing. The reputation detections are decisive, and no other signal offsets them. The domain name borrows the vocabulary of an established DeFi lending brand and was registered only very recently. That combination fits the usual pattern of lookalike domains set up to harvest wallet access or funds, although the evidence does not by itself establish which brand, if any, is being copied. In the behavioural sandbox, no wallet-drainer routine, clipboard hijack, hidden form or externally posting password form was detected. The page nonetheless changed its structure extensively after interaction and exchanged a large volume of background traffic with external services, so live content can differ substantially from what a first load shows. Taken together, the site should be treated as a high-risk destination for any wallet connection, login or financial action. The posture is cautionary, not a finding that a particular operator has committed fraud. Evidence:
- Homepage reputation checks: 16 security engines flag the domain as malicious and 2 as suspicious, including several tier-one vendors, and an external kill-switch condition is active.
- Domain provenance: registered 2026-08-07, about 80 days (~0.22 years) old, so the site has no established track record.
- Homepage behaviour: 49 external background requests and 6 external POSTs, all to recognised destinations, and 5,593 page-structure changes after interaction.
- DeFi directory check: the domain does not appear among recognised DeFi protocols, so no TVL or protocol listing supports a claim to represent an established protocol.
Regulatory Verification Notes
The analysis found no regulator registration, licence or authorised-entity listing for the site, and no third-party broker record matched it. Its legal and identity disclosures are unclear. Registrant details are incomplete, which amounts to ownership opacity, and it cannot be tied to a real-world company or individual. This is a verification gap in its own right. The serious concerns arise from the reputation findings above. The domain is registered through NICENIC International Group Co., Limited. Its transport encryption is a standard domain-validated certificate, which proves only that the connection is encrypted and says nothing about who operates the site. Evidence:
- Registration record: registrar NICENIC International Group Co., Limited, created 2026-08-07, expiring 2027-08-07, with owner details incomplete.
- Transport security: TLS certificate issued by WE1 (DV), valid to 2027-01-03.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Broker reputation dataset: no match, so there is no third-party regulatory or reputational record for this domain.
What to Verify Next
Any connection to the real Aave protocol should be established only through its official channels, reached independently of this domain, for example via a bookmarked address or the project's verified social and documentation accounts. If the site claims a company name, licence or audit, each claim should be checked directly against the relevant registry or the auditor's own publication. Any link or message that led to this domain should be traced back to its sender and treated as unsolicited until that sender is authenticated. A wallet that has already interacted with the site should be reviewed for token approvals, and any unrecognised approvals revoked. Evidence:
- Domain name: the lending-brand term plus "fi" suffix on a .info domain should be compared against the official protocol's published address.
- Homepage: the site's behaviour includes heavy post-interaction page changes, so any displayed claims cannot be treated as stable.
- Registration record: the domain is only months old, which leaves no operating history to rely on.
Summary Verdict
The overall posture is high-risk and clearly cautionary. Third-party threat intelligence is decisive, and the site's newness and unverified identity give no basis to discount it. Legitimacy cannot be inferred, and the site is unsuitable for any sensitive or financial interaction.
Infrastructure Integrity
The site is fronted by Cloudflare's CDN and WAF. All four observed addresses are Cloudflare edge servers, so the origin host cannot be seen and independent verification of the real hosting is not possible. The domain's bot-protection layer is also Cloudflare. A valid certificate from a known issuer and a normal edge network confirm only that the site is competently delivered, and they do not offset the reputation findings. The 24 abuse reports on one of its edge addresses are attributed to the shared provider address, not to this domain, and are discounted. The same edge address also serves unrelated customers.
Closing Assessment
The site should be treated as read-only at most. Wallets should not be connected, credentials should not be entered, and no funds, approvals or signatures should be given on this domain. Anyone who has already done so should move assets to a fresh wallet and revoke existing approvals.
Written analysis generated 2026-10-27 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, hosting and network, behaviour in a sandbox.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page replaced a large part of its own content after loading.Behaviour in a sandbox
rule:BEHAV_DOM_CHANGE_HIGH - The page rewrote itself after it was interacted with, so what a visitor first sees is not what they end up on.Behaviour in a sandbox
rule:BEHAV_DOM_DIFF_AFTER_INTERACTION - The structure of the page changed sharply while it was loading.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE
Signals weighed against the site
- AbuseIPDB: 24 reports on hosting IP 2a06:98c1:3120::b (Cloudflare, Inc., Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of aave-fi.info.
- The request stayed on aave-fi.info. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-08-07. Noted
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2a06:98c1:3120::b |
| Name servers | ashley.ns.cloudflare.com, tanner.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-03 |
| Domain age | 0.22 years (continuous registration) |
| Domain expiry | 2027-08-07 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 16 flagged | AbuseIPDB: 0% confidence, 24 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about aave-fi.info at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.