Verdict
Several risk patterns were present. Do not send money or personal details until you have verified this business another way.
ai-gradient.network is low-trust and potentially risky.
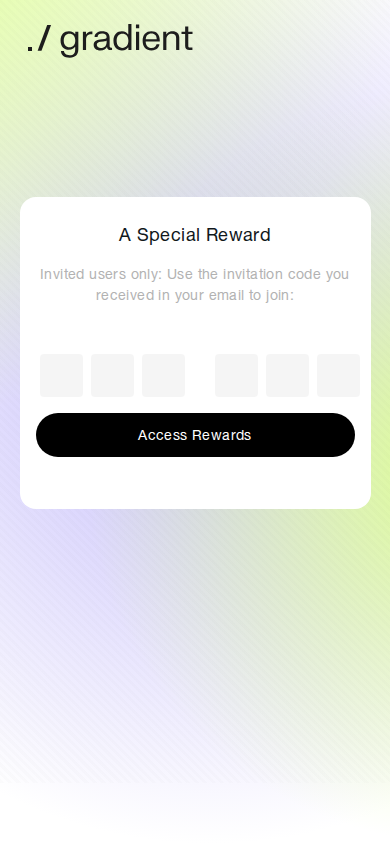
| What this site appears to be | A minimal page titled 'Gradient Dashboard' offers 'A Special Reward' to invited users only, asking them to enter an invitation code received by email to join and access rewards. No service description, legal entity, contact details, or monetization terms are visible, so the page is classified as a login-only page with no context. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 29 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20262 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YR2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Ai-gradient.network is a single-page website titled "Gradient Dashboard" that offers "A Special Reward" to invited users only. It asks a visitor to enter an invitation code received by email and then press "Access Rewards". The page gives no description of a product or service, no operator, and no pricing. Its apparent purpose is an invite-gated rewards or sign-up funnel whose business model cannot be determined from the visible content.
Scam/Impersonation Risk
This site shows confirmed contradictory signals, and its risk posture is elevated. It appears on external blacklists. More than one independent reputation source flags it as malicious, and a tier-one security vendor is among those flagging it. This is a confirmed blacklisting, not a speculative concern. No brand impersonation and no conflicting legal identities were observed, so the risk comes from the reputation record and the nature of the page. The homepage is an invitation-code gate with no accompanying context. Invite-only "special reward" mechanics are a common pattern in reward-claim and onboarding lures. They create a sense of exclusivity while a visitor is steered into an account or deposit flow that cannot be inspected beforehand. The automated business-model assessment also flagged a deposit-before-service pattern, although the captured text itself describes no deposit. The site is also very new, and its page content is thin. During behavioural testing, nearly all page activity consisted of requests to third-party endpoints, mostly outside any recognised allow-list. The page also carries one analytics tracker, one ad-network tracker and one tracking pixel, which is out of proportion for a 130-character page. No cloaking, hidden forms, wallet-drainer behaviour or clipboard manipulation was detected. The posture rests on the reputation record and the opacity of the offer, not on observed malicious page behaviour. Evidence:
- The homepage contains only the title "Gradient Dashboard", the text "A Special Reward", an instruction to use the emailed invitation code, and an "Access Rewards" action, with no service, owner or terms described.
- Domain registered 2026-09-19 (~31 days old), through NICENIC INTERNATIONAL GROUP CO., LIMITED.
- The web archive holds 2 snapshots, spanning 2026-09-19 to 2026-09-20 (1 year tracked), so there is no meaningful operating history.
- Behavioural testing across 3 runs recorded 7 external requests, 6 of them to non-allow-listed destinations, and no password or external-form submissions.
Regulatory Verification Notes
The homepage is the only page captured. It has no legal or identity pages, no named operating entity, no registered address, no licence or registration number and no contact channel. The site claims no licence or regulatory status, and none could be corroborated independently. Operator identity is therefore unverified, and ownership and governance are opaque. Because the site invites participation in a reward programme, which could involve financial or personal-data exchange, the absence of any accountable party is a material gap. It adds to the reputational concerns above but is not by itself evidence of fraud. No third-party broker or regulator listing was matched for this domain. Evidence:
- The homepage shows no company name, jurisdiction, licence number, privacy policy or terms of service.
- Served from AS214036 (Ultahost, Inc.), with a server located in South Africa.
- TLS certificate issued by YR2 (DV, domain validation only), valid to 2026-12-18. This confirms domain control, not organisational identity.
What to Verify Next
Any contact with this site should begin by establishing independently whether the invitation actually exists. A recipient should check the original email's sender and headers and confirm with the claimed sender through a separately sourced, offline channel. The recipient should not rely on any link or reply address in the message. The operating entity behind the "Gradient" name should be identified through an independent source, and any claimed authorisation should be checked against the relevant public registry. Official support channels should be confirmed from an independent source, not from the site. A security team should also check whether the invitation code arrived unsolicited, since an unsolicited code is more consistent with a lure. Evidence:
- The homepage describes no reward mechanics, issuer or eligibility rules that could be cross-checked.
- The invitation-code gate is the only entry point, and no other pages were captured.
- Blacklist status should be re-checked in a later review, since the domain is only a few weeks old and its record is still forming.
Summary Verdict
The overall posture is high risk and clearly cautionary. External reputation sources have confirmed adverse detections, the operator is unidentified, and the offer is opaque. These signals converge and cannot be offset by the technically valid certificate or by the stable page behaviour recorded in testing. Legitimacy is not supported by the available evidence.
Infrastructure Integrity
The domain resolves to a single address at a commodity hosting provider, Ultahost, with no CDN or WAF in front of it. The origin server is therefore directly exposed, and no protective layer mitigates the reputational findings. The hosting is a generic data-centre environment with no abuse reports against the address. That is neutral and does not offset the external detections.
Closing Assessment
Treat the site as untrusted. At most, limited read-only observation from an isolated environment is appropriate. Do not enter the invitation code, any credentials or any personal data, and make no payments or deposits. Any related email should be treated as potentially hostile and reported to the organisation's security team.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, page content, history in the web archive.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of ai-gradient.network.
- The request stayed on ai-gradient.network. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by ultahost.com, across 4 name servers. Noted
- The registration is paid up to 2027-09-19. Noted
- The earliest public archive of this site is from 2026-09-19. Clear
- It is hosted on ULTAHOST-AS, from a server in ZA. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | ULTAHOST-AS - Ultahost, Inc., US |
| Country | ZA |
| Server IP | 192.142.53.246 |
| Name servers | ns1.ultahost.com, ns2.ultahost.com, ns3.ultahost.com, ns4.ultahost.com |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR2 |
| SSL expiry | 2026-12-18 |
| Domain age | 0.08 years (continuous registration) |
| Domain expiry | 2027-09-19 |
| Archive first seen | 2026-09-19 |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 2 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about ai-gradient.network at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.