Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
allbridge-bridge.vercel.app shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 103 reports; shared hosting inflates reports | Clear |
| Domain age | 26 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20261 snapshot | Clear |
| Certificate | Encrypted connectionIssued by WR1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
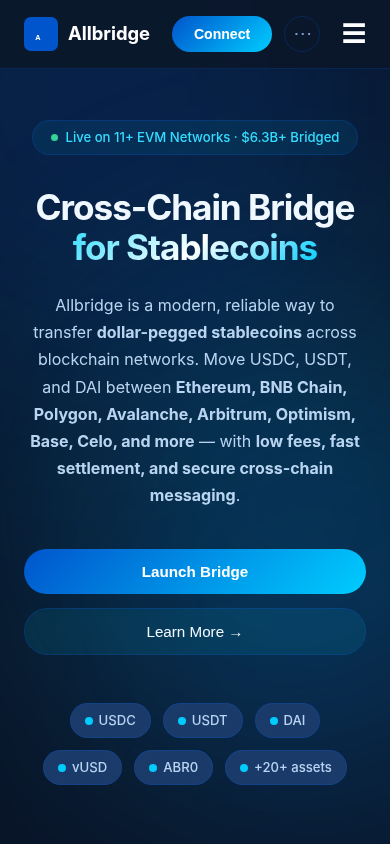
This website presents itself as "Allbridge Bridge", a cross-chain stablecoin bridge for EVM networks. It is a single-page interface that invites visitors to move tokens between blockchains, and it is served from a free subdomain on a shared application-hosting platform rather than from a dedicated brand domain. Its apparent purpose is a token-transfer service that would require visitors to interact with crypto wallets and approve on-chain transactions.
Scam/Impersonation Risk
Hard contradictory signals are present. Several independent threat-intelligence sources currently list this site as malicious or suspicious, and the combined result amounts to a confirmed blacklist condition. The hostname fuses a well-known bridge protocol's name with the generic word "bridge" on a platform subdomain that anyone can create at no cost. That is a classic brand-lookalike pattern, and nothing observed ties the site to the genuine protocol's operators. The homepage describes a bridge for moving stablecoins between EVM networks. Services of this kind routinely ask visitors to sign token approvals and transfers, so a lookalike front-end would be positioned to redirect funds. Abuse reports exist against the shared edge address the site resolves to. Those reports are attributed to the hosting platform's shared infrastructure and are discounted, so they are not counted against the site itself. Browser-behaviour testing was comparatively benign. The page made no external requests, showed no wallet-drainer, clipboard-hijack or hidden-form behaviour, and did not cloak its content. Clean behaviour in a short sandbox session does not offset the external threat listings, and a wallet-interaction flow could behave differently once a real wallet is attached. Evidence:
- Homepage: the title and content present a cross-chain stablecoin bridge for EVM networks under the Allbridge name, hosted on a platform-issued subdomain.
- Domain provenance: the hostname was first observed about 26 days ago, with a single web-archive snapshot from 2026 (1 year tracked), so there is no history of legitimate operation.
- Reputation: two security engines rate the site malicious and one suspicious, against 57 harmless verdicts and 32 with no verdict. Abuse reports on the shared edge IP (103) are attributed to shared infrastructure.
- Behaviour: three of three sandbox runs completed with no external requests, no wallet-provider activity and no DOM manipulation after interaction.
Regulatory Verification Notes
The site presents no verifiable operator identity, legal entity, licence or registration. This is a disclosure gap on the page and is not, by itself, evidence of wrongdoing. Its weight here comes from sitting alongside the threat listings. Identity could not be independently connected to the real protocol, so no claim of affiliation with it can be accepted. No third-party broker or regulatory record was matched. The site is also not recognised in any DeFi protocol directory, which fits a lookalike deployment better than an established protocol front-end. Evidence:
- Homepage: the page offers no named company, jurisdiction, licence or registration number.
- Technical: the site is served from AS16509 (AMAZON-02, Amazon.com, Inc., US).
- Transport security: the TLS certificate is issued by WR1 at domain-validation (DV) level and is valid to 2026-11-27, about 36 days remaining. It confirms only control of the hostname, not the operator's identity.
- Directory check: no DeFi protocol directory listing and no TVL record exist for this hostname.
What to Verify Next
Any prospective interaction should begin by establishing whether the genuine protocol operates this front-end. That means obtaining the official address from the protocol's documentation or verified social channels, not from links, search ads or messages that led here, and comparing it with this hostname. Official support channels should be confirmed independently, and the protocol's published security notices should be checked for warnings about lookalike front-ends. If any token approvals have already been granted to contracts linked to this site, they should be reviewed and revoked with a reputable approval-management tool. Evidence:
- Homepage: the hostname differs from any dedicated brand domain, which is the first thing to compare with the official address.
- Reputation: current malicious and suspicious detections mean the page should be treated as unsafe for transactions until cleared.
- Provenance: the very recent first sighting of the hostname gives no prior record to rely on.
Summary Verdict
The available evidence supports a clearly cautionary, high-risk posture. Active threat-intelligence listings, a brand-lookalike hostname and an absence of any verifiable operator or history outweigh the clean technical hygiene and benign sandbox behaviour. Identity is unverified, and the site cannot be treated as an authentic service.
Infrastructure Integrity
The site resolves entirely to edge addresses of a protective CDN/WAF layer on Amazon-operated hosting in the United States, and the origin server is not observable. This layer is a mitigating factor only. It shows the site is hosted on a mainstream platform, but it does nothing to establish who operates the site or whether it is legitimate. Edge-only visibility also means page content can be swapped quickly without any change to the visible infrastructure.
Closing Assessment
Do not connect a wallet, sign messages, approve token spending, or enter credentials or funds on this site. Passive viewing is the only reasonably safe use. Anyone needing a bridge should use only an address obtained independently from the genuine protocol's official channels.
Written analysis generated 2026-10-22 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by external reputation, hosting and network, history in the web archive, behaviour in a sandbox, registration and ownership.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
04 Behaviour in a sandbox
- A large share of what the page loaded came from other domains.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_MODERATE
05 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Signals weighed against the site
- AbuseIPDB: 103 reports on hosting IP 216.198.79.195 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of allbridge-bridge.vercel.app.
- The request stayed on allbridge-bridge.vercel.app. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-09-25. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 216.198.79.195 |
| Name servers | Not available |
| CDN / edge network | Detected |
| Resolved IP addresses | 6 |
| Edge IP addresses | 6 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| Domain age | 0.07 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2026-09-25 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 2 flagged | AbuseIPDB: 0% confidence, 103 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about allbridge-bridge.vercel.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.