Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
app-routerprotocol.pages.dev shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 1.5 years oldRegistered history | Clear |
| Web archive | Archived since 20253 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
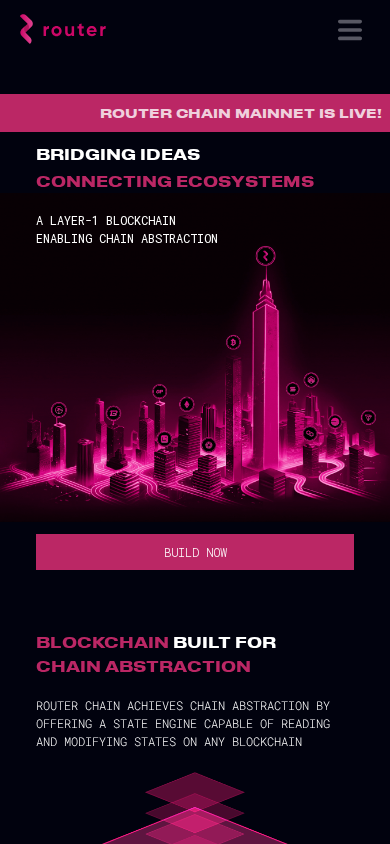
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: 1 to 3 years (registration continuity).
- Public web-archive history exists since 2025.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
This website is a single-page crypto front end on a free shared-hosting subdomain. Its page title presents it as "Router Protocol", offering cross-chain swaps and chain abstraction. A visitor sees a decentralized-finance style interface, and the apparent purpose is to get users to interact with a cross-chain token swap and bridging service.
Scam/Impersonation Risk
This is the dominant concern. Several independent threat-intelligence sources currently flag the site as malicious or suspicious, and a confirmed blacklist-level detection is present. Those detections outweigh every other signal and are decisive for the verdict. The site's name embeds a recognisable crypto-protocol brand on a free, shared subdomain, not on a dedicated domain. That is a pattern commonly used for brand-lookalike and wallet-interaction lures. The evidence does not confirm which brand, if any, is being imitated, and no conflicting legal identities were observed. The brand-lookalike naming is therefore a risk-amplifying context, not a proven impersonation. A cross-chain swap interface asks visitors to connect wallets and approve transactions, so a malicious front end of this kind can lead to loss of funds. No wallet-drainer, clipboard-hijack, or cloaking behaviour was observed in the automated browsing sessions. That result does not offset the external detections, because malicious logic can be deployed or swapped in later. Evidence:
- Homepage: the title presents a protocol brand with cross-chain swap and chain-abstraction messaging, hosted on a shared free-hosting subdomain.
- Multiple independent threat-intelligence sources report the site as malicious or suspicious, and a blacklist-level detection is active.
- Domain registered about 1.5 years ago (first observed April 2025), with only 3 archive snapshots across 2025–2026 (2 years tracked), which gives no established history.
- Behavioural sessions (3 of 3 successful) showed no wallet-drainer, clipboard-write, hidden-form, or cloaking activity, and one external POST request was observed.
Regulatory Verification Notes
The available evidence does not connect the site to any verified operator, company, or registered financial entity, and it identifies no governing party. The site's identity could not be independently confirmed, so any on-site brand claim carries no weight as proof. No third-party broker or regulatory-registry record matched the site. Licensing status is therefore unconfirmed, and nothing supports treating the service as a regulated product. The site is not recognised in public DeFi protocol directories, so there is no independent record of the liquidity or protocol activity that "cross-chain swap" messaging implies. These are verification gaps. The external detections are what make the risk elevated. Evidence:
- Identity assessment: the site is not independently linked to any real-world brand or person.
- No broker or regulatory-registry match was found for the site.
- Hosted on AS13335 (Cloudflare, Inc., US); TLS certificate issued by WE1 (DV, domain-validated only), valid to 2026-12-29.
- No DeFi directory listing or reported TVL was found for this deployment.
What to Verify Next
Before any interaction, the official website of the genuine protocol should be reached through an independently sourced route, such as its verified social channels or a trusted aggregator. Its canonical address should be compared character by character with this one. Any claim of affiliation made by this site should be checked against the protocol's own announcements. Wallets should not be connected, and no signing or token-approval prompt should be accepted from this site. Any wallet that has already interacted with it should have its token approvals reviewed and revoked. Official support and contact channels should be confirmed through the protocol's verified documentation, not through links on this site. Evidence:
- Homepage: the brand-style title sits on a shared subdomain, so the address needs comparison with the genuine protocol's canonical domain.
- The site's domain history is short, with only 3 archive snapshots, so there is no long track record to rely on.
- Active external detections mean prior wallet interactions with the site warrant review.
Summary Verdict
The site is assessed as a high-risk, critical-trust property. Active external malicious-site detections drive that assessment, and the site's brand-style presentation on a disposable subdomain, short history, and unverified operator reinforce it. Apparent technical hygiene such as a valid certificate and stable page behaviour does not mitigate it. The site is unsuitable for login, credential entry, wallet connection, or any financial interaction.
Infrastructure Integrity
The site is served entirely through Cloudflare's CDN and WAF. All observed addresses are edge servers, and the origin host cannot be seen, which prevents independent verification of where the content actually runs. A valid certificate and mainstream edge hosting are only mitigating factors, because these services are freely available to any deployer, including malicious ones. They cannot offset the reputation risk. Edge-only visibility also means page content can be swapped quickly without any visible change in hosting.
Closing Assessment
The site should be treated as unsafe for anything beyond passive, read-only viewing, and ideally avoided. No credentials should be entered, no wallet connected, and no funds committed. Any legitimate need to use the named protocol should be met through its officially published channels.
Written analysis generated 2026-10-29 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by governance, external reputation, registration and ownership.
01 Governance
- A threat feed lists this domain as malicious, and that caps the score whatever the other checks found.Governance
rule:GOV_CRITICAL_BLACKLIST
02 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
03 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of app-routerprotocol.pages.dev.
- The request stayed on app-routerprotocol.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2025-04-17. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2c47 |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-29 |
| Domain age | 1.53 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2025-04-17 |
| Archive snapshots | 3 |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about app-routerprotocol.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.