Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
apps-wallet--connect.web.app shows high-risk / scam indicators.
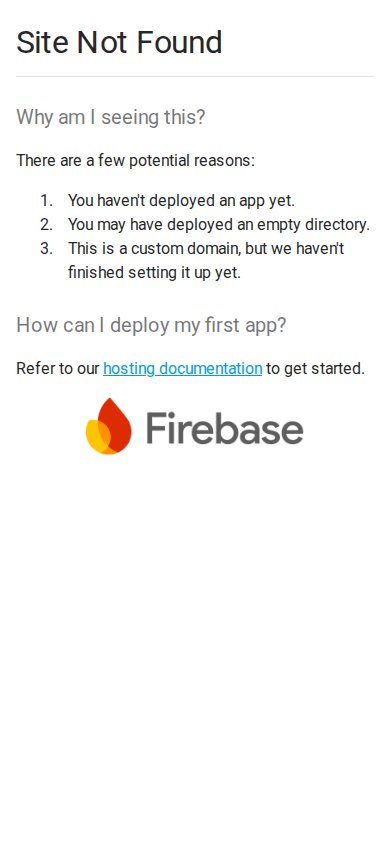
| What this site appears to be | Hosting provider default placeholder reporting that no application is deployed at this domain. The page contains no service description, forms, links, or scripts. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 4% confidenceAbuseIPDB, 4 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Fortinet flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
The website at this address is a hosting-provider "Site Not Found" placeholder served on a free subdomain of a developer hosting platform. It tells the visitor that no application has been deployed, that an empty directory may have been published, or that a custom domain has not finished setting up. It shows no products, pricing, forms, links, branding or business description, so it has no visible business model. Its hostname, however, pairs the words "apps", "wallet" and "connect".
Scam/Impersonation Risk
Confirmed contradictions are present. A threat-intelligence feed currently lists this site as the actor in a phishing operation, which is the decisive factor in this assessment. The site is also blacklisted by several independent reputation sources, with multiple security engines flagging it as malicious. The placeholder page's blank content therefore does not indicate a benign or abandoned site. A placeholder is also a common state for a phishing page that has been taken down or is being staged. The hostname's wallet-connection wording matches the naming pattern of crypto-wallet lures, which try to get visitors to connect wallets or enter recovery phrases. No brand impersonation has been confirmed, and no conflicting legal identities exist because no identity is presented at all. The homepage also behaved differently from what its static content suggests. The sandbox saw a very large number of external requests, repeated outbound posts and heavy page-structure changes after interaction. The requested page and the final destination did not match, and the server returned a not-found status. All observed external traffic went to recognised destinations, so it is not independently malicious. It is still an unexplained mismatch for a page with no scripts or links. A small number of abuse reports exists for a shared content-delivery address used by the hosting platform. These apply to the shared provider infrastructure rather than to this site specifically, and they are not counted as site-specific evidence.
- Threat-intelligence listing, last seen in mid-October 2026, classes the site as an active phishing actor. This is the controlling signal.
- Four security engines flagged the domain as malicious, and none of its 58 harmless verdicts offsets this.
- Homepage sandbox: 257 external XHR requests, 28 external POSTs and 2,204 DOM mutations on a page with 311 characters of text, alongside a final-destination mismatch and a 404 status.
- Four abuse reports attach to the shared provider address, not to this site specifically.
Regulatory Verification Notes
The site publishes no legal, terms, privacy, about or contact pages, so no operator, company name, jurisdiction, licence or registration number can be assessed. The real-world operator is unverified, and ownership is opaque. This reflects the absence of any disclosure on the site, and it adds to the concern because an active phishing listing already exists. Without a regulated status, a verified operator or any third-party reputation record, nothing offsets the active threat listing. No broker-reputation record matches this domain, so there is no external regulatory signal in either direction. The transport encryption is valid but only domain-validated, so it confirms an encrypted connection and says nothing about who operates the site.
- Homepage contains only generic placeholder text and no company name, licence statement or registration number.
- No legal or policy pages are reachable from the homepage, which has no links at all.
- Served from AS54113 (Fastly, US).
- TLS certificate issued by WR4 (DV), valid to 2026-12-22.
What to Verify Next
Do not interact with the site while the threat listing is active. If a link to this address arrived by message, social post, advertisement or email, treat that source as suspect and confirm independently whether it is genuine. Any wallet or application service the sender claims to represent should be reached only through an official address obtained from a trusted offline or previously known route, not by following the link. Anyone who has already connected a wallet, signed a request or entered credentials here should revoke wallet permissions with a trusted tool, move assets if needed, and change reused passwords. The domain should be reported to the hosting platform and to browser and security reporting channels. Official support channels should be confirmed only through independent routes.
- The homepage offers no forms, links or contact route, so nothing on the site can be used to confirm legitimacy.
- The phishing listing was still current at the time of analysis.
- The hosting platform's own placeholder text confirms that no application is deployed at this address.
Summary Verdict
The site carries an elevated risk posture. An active phishing listing and independent malicious detections converge on an unverified, anonymous operator, and the benign-looking placeholder does not mitigate them. It should be treated as a hostile or compromised-in-purpose destination, not as a dormant page.
Infrastructure Integrity
The site is served through well-known content-delivery infrastructure from Fastly, and Cloudflare edge addresses also appear among the resolved IPs. Every observed address is a shared edge node, and no origin server was observable. This is a standard setup for free-hosted subdomains and says nothing about the operator's honesty. The infrastructure mitigates exposure only in the narrow sense that it is a mainstream, well-maintained platform. It cannot offset the active threat listing, because shared edge hosting is equally available to legitimate and malicious publishers.
Closing Assessment
The site is suitable at most for passive viewing from an isolated environment. Wallet connections, transaction signing, recovery-phrase entry, logins, credential submissions and payments should all be avoided. Any exposure that has already occurred should be handled as a potential compromise.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by governance, external reputation, behaviour in a sandbox, page content.
01 Governance
- A threat-intelligence feed currently lists a file on this site as malicious, and that caps the score while the listing is live.Governance
rule:gov_active_threat_listing
02 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
03 Behaviour in a sandbox
- The structure of the page changed sharply while it was loading.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY - The page sent data to other domains many times while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_POSTS_HEAVY
04 Page content
- The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META
Signals weighed against the site
- AbuseIPDB: 4 reports on hosting IP 2620:0:890::100 (Google LLC, Content Delivery Network), 4% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of apps-wallet--connect.web.app.
- The request stayed on apps-wallet--connect.web.app. It was not redirected to another domain. Clear
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | Not available |
| Country | Not available |
| Server IP | 2620:0:890::100 |
| Name servers | Not available |
| CDN / edge network | Lookup incomplete |
| SSL issuer | WR4 |
| SSL expiry | 2026-12-22 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not available |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 4% confidence, 4 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about apps-wallet--connect.web.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.