Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
aurora-cooked.netlify.app shows high-risk / scam indicators.
| What this site appears to be | Community-hosted landing page for the Aurora Cooked Client (Minecraft Java edition) offering a direct .jar download (aurora.cooked.jar, ~5.46 MiB). The page includes feature blurbs (PvP, exploration), a compatibility warning advising users to only run trusted JARs and to back up worlds, and an explicit disclaimer that it is unofficial and not affiliated with Mojang or Donut SMP. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 3 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 2 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
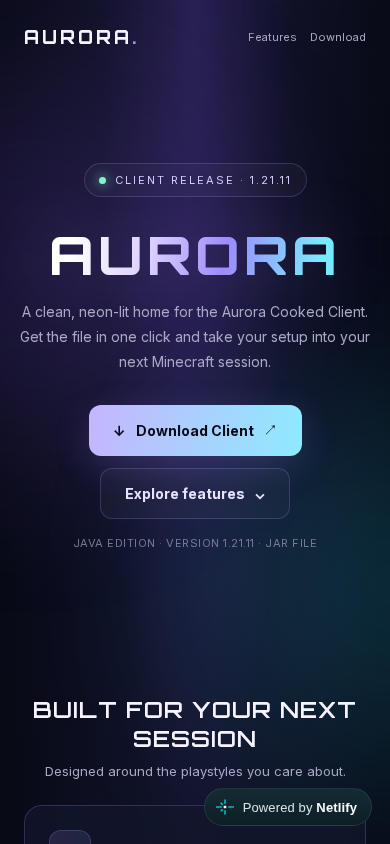
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This is a single-page, community-run landing site hosted on a free subdomain of a general-purpose web hosting platform. It promotes the "Aurora Cooked Client", a Minecraft Java Edition 1.21.11 modification, and offers a one-click direct download of an executable archive named aurora.cooked.jar (about 5.46 MiB). The page uses neon-styled feature blurbs for PvP, exploration and a "Donut SMP Ready" theme. It describes itself as an unofficial community page and states it has no affiliation with Mojang or Donut SMP. No monetisation model is presented. Its apparent purpose is distributing a modified game client file.
Scam/Impersonation Risk
Confirmed contradictory signals are present, and they dominate the assessment. A threat-intelligence listing currently identifies this site itself as distributing malware. It was last observed very recently, and it is decisive. Several independent security engines also flag the domain as malicious or suspicious, including a top-tier security vendor, which together amount to a confirmed blacklist position. The concern is the downloadable file, not the page's visible design. The site's sole call to action is an executable Java archive of unverifiable content. The page admits it "does not verify its contents or guarantee compatibility" and tells users to "only run JAR files you trust", which shifts all risk to the downloader. No brand impersonation, phishing form or conflicting legal identity was observed. The page carries no login, payment or wallet-connect surface, and its sandboxed behaviour showed no external data exfiltration. These benign behaviours do not offset the malware-distribution listing, because the threat sits in the payload that a visitor would run locally. A Minecraft client mod is also a common lure for credential and session-token stealers aimed at game accounts. Evidence:
- Homepage: a single prominent "Download .JAR" control serves aurora.cooked.jar (about 5.46 MiB) directly, with no checksum, source repository or publisher attribution.
- Homepage: the page states it "does not verify its contents" and that users should "only run JAR files you trust".
- Threat listing: the site is currently listed as an active actor for malware distribution, last seen 2026-10-13.
- Reputation checks: 3 engines flag the domain as malicious and 1 as suspicious, including one top-tier vendor.
Regulatory Verification Notes
The site is not a regulated financial or commercial service, and no licence is claimed, so licensing is not the relevant test. The relevant gap is accountability. The page names no developer, maintainer, organisation, support route or terms of use. The operator is unidentified and independent identity verification was not achieved. The only affiliation statement is a trademark disclaimer for Mojang and Donut SMP, which is not a source of provenance. The absence of an accountable publisher compounds the malware listing, because there is no named party to hold responsible for the file. No third-party broker or regulator record matches this site. Evidence:
- Homepage: no named developer, company, contact channel or legal pages; the only attribution is "Unofficial community download page".
- Hosting: served from AS16509 (AMAZON-02, Amazon.com, Inc., US).
- Transport encryption: TLS certificate issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 (OV) to the hosting platform's organisation (Netlify, Inc), valid to 2027-03-19. This identifies the platform, not the site's publisher.
- Page metadata: no meta description, canonical tag or structured data is published.
What to Verify Next
Verification should focus on whether any trustworthy version of this software exists, not on rehabilitating this download. A prospective user should look for a named author and a public source repository through an independent route, such as a well-known modding community or the game server's own staff. Any published checksum or code signature should be matched before the file is trusted. If the file has already been downloaded, it should not be run. It should be scanned in an isolated environment, and the user's game and linked account credentials should be rotated if it was executed. The site's operator should be asked, through an independent channel, to confirm the official support and contact routes. Evidence:
- Homepage: no checksum, release notes or source link accompanies the download.
- Homepage: the compatibility notice itself recommends backing up worlds, which acknowledges possible damage from running the file.
- Threat listing: the malware flag is current, so any copy of aurora.cooked.jar obtained from this site is suspect.
Summary Verdict
The site presents a clearly high-risk posture. Active malware-distribution reporting and corroborating multi-engine detections outweigh its plain presentation and its clean sandbox behaviour. The operator's real-world identity is unverified, so no claim of legitimacy can be supported. This is a decisive, evidence-based cautionary classification, not a precautionary one.
Infrastructure Integrity
The site is served from Amazon-operated infrastructure behind a content-delivery layer, and the visible edge addresses sit on Cloudflare's network. The true origin server was not observable. This is a mitigating factor only and does not offset the reputation findings. Two abuse reports exist against an address belonging to a shared Amazon content-delivery range. They apply to shared provider infrastructure, not to this site, and were discounted accordingly. The malware listing and the multi-engine detections are not attributable to that shared-infrastructure noise.
Closing Assessment
The site should not be used for downloads, and aurora.cooked.jar should not be opened or executed. No credentials, game-account details or payment information should be associated with anything obtained from it. Read-only viewing of the page carries little direct risk, but nothing should be installed from it until the listing is cleared and a named publisher with verifiable source material emerges.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by governance, external reputation, page content.
01 Governance
- What the site offers, as described on its own pages, limits how high the score can go until more of it can be verified.Governance
rule:gov_business_model_cap - A threat-intelligence feed currently lists a file on this site as malicious, and that caps the score while the listing is live.Governance
rule:gov_active_threat_listing
02 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
03 Page content
- The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
Signals weighed against the site
- AbuseIPDB: 2 reports on hosting IP 2a05:d014:58f:6200::259 (Amazon Data Services Ireland Ltd, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of aurora-cooked.netlify.app.
- The request stayed on aurora-cooked.netlify.app. It was not redirected to another domain. Clear
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | Not available |
| Country | Not available |
| Server IP | 2a05:d014:58f:6200::259 |
| Name servers | Not available |
| CDN / edge network | Lookup incomplete |
| SSL issuer | DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
| SSL expiry | 2027-03-19 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not available |
| Reputation | VirusTotal: 3 flagged | AbuseIPDB: 0% confidence, 2 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about aurora-cooked.netlify.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.