Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
axiomdesktop.com shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 2 months oldMost scam domains are under a year old | Risk |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
| Hosted by | CLOUDFLARENETServer in US | Noted |
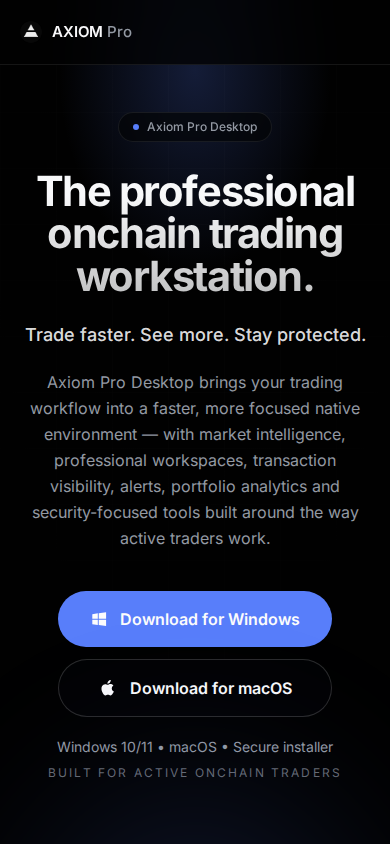
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
AXIOM Pro Desktop is a website presenting itself as a "professional onchain trading workstation", a desktop-style trading product aimed at cryptocurrency and decentralized-finance users. The visitor sees a single-page product presentation whose apparent purpose is to promote and distribute trading software or terminal access. The site is very newly established and operates in a sector where fraudulent and malicious clones are common.
Scam/Impersonation Risk
This assessment is cautionary and security-forward. Contradictory signals are present. Several independent security engines currently flag the domain as malicious or suspicious, including two tier-one vendors, and the site appears on external blacklists. In the behavioral sandbox, the page also triggered malware-execution behavior, so the flagging is corroborated by observed runtime conduct rather than resting on reputation alone. The page also rewrote its own structure on a very large scale after interaction, with thousands of DOM mutations. This is consistent with content being injected or swapped dynamically, which is a common pattern in payload-delivery and wallet-targeting pages. The site is also a newly registered domain marketing trading software, a lure category often used to push malicious installers to crypto users. No conflicting legal identities were observed. No impersonation of a named brand was confirmed, and the supplied evidence does not show whether the product name borrows a legitimate brand. The risk therefore rests on threat detections and runtime behavior, not on identity conflict. Direct interaction, including downloads, installers, wallet connections, and credential or payment entry, should be treated as unsafe. Evidence:
- Homepage: Multiple security engines rate the domain malicious or suspicious. Two tier-one vendors are among them, and the domain is externally blacklisted.
- Homepage sandbox runs: Malware-execution behavior was observed across all three runs. Interaction triggered 4,728 DOM mutations.
- Domain provenance: Registered 2026-09-03 (~0.14 years old, about 52 days).
Regulatory Verification Notes
No licensing, registration, or regulated-entity status could be established for the operator. The page's disclosure state is unclear, and page-level content analysis was incomplete, so the absence of a license should not be read as a confirmed omission by the site. Operator ownership and governance are opaque: registration details are hidden or incomplete, and nothing independently connects the site to a named company or individual. This is ownership opacity, not an identity contradiction. A product that handles trading activity and potentially user funds would ordinarily be expected to identify its operating entity and applicable regulatory standing. Third-party broker-reputation datasets returned no match, which is neutral and neither supports nor undermines the site. Domain registration through a Hong Kong-based registrar and a standard domain-validated TLS certificate are routine facts that confer no legitimacy. Evidence:
- Domain registration: Registrar NICENIC INTERNATIONAL GROUP CO., LIMITED; created 2026-09-03, expires 2027-09-03.
- Transport encryption: TLS certificate issued by YE1 (DV, domain validation only), valid to 2026-12-11 (46 days remaining at analysis).
- Hosting: Served from AS13335 (Cloudflare, Inc., US).
What to Verify Next
Any contact with the site should be preceded by independent checks. First, confirm through official channels, not links on the site, whether a legitimate product named AXIOM exists and which domain its vendor actually uses. Second, check whether the claimed operator appears in a financial or business registry in a relevant jurisdiction. Third, confirm official support and contact channels offline or through an independent route. Fourth, if software was already downloaded or run from this site, treat the device as potentially compromised: scan it, review wallet approvals and revoke unnecessary ones, and rotate any credentials that were exposed. Evidence:
- Homepage: Product positioning as a trading workstation implies software distribution, so any executable obtained from the site is a priority for scanning.
- Domain provenance: The domain is under two months old, so no established track record exists to rely on.
Summary Verdict
The evidence converges on a high-risk, critically low trust posture. Confirmed external threat detections, a blacklist presence, and malware-execution behavior in sandbox testing outweigh the few neutral technical hygiene factors, such as a valid certificate and a stable page response. Real-world operator identity remains unverified, and legitimacy cannot be inferred.
Infrastructure Integrity
The site is fronted by Cloudflare's CDN and WAF, and every observed address is an edge node of that network, so the origin server could not be seen. This protective layer is a minor mitigating factor only. It also prevents independent hosting verification and can mask rapid content swaps, which is relevant given the dynamic page rewriting observed. It does not offset the threat detections.
Closing Assessment
The site should not be used for downloads, wallet connections, logins, credentials, or any financial interaction. If it must be examined, this should be done only from an isolated environment, with no software downloaded or executed from it.
Written analysis generated 2026-10-25 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, hosting and network.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Behaviour in a sandbox
- The page attempted to run or deliver malicious code during the sandboxed visit.Behaviour in a sandbox
rule:BEHAV_MALWARE_EXECUTION - Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page replaced a large part of its own content after loading.Behaviour in a sandbox
rule:BEHAV_DOM_CHANGE_HIGH - Many of the responses the page received looked generated rather than served normally.Behaviour in a sandbox
rule:BEHAV_SYNTHETIC_RESPONSES_HIGH
03 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of axiomdesktop.com.
- The request stayed on axiomdesktop.com. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-03. Noted
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3036::6815:3b9 |
| Name servers | EVA.NS.CLOUDFLARE.COM, KURT.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-11 |
| Domain age | 0.14 years (continuous registration) |
| Domain expiry | 2027-09-03 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about axiomdesktop.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.