Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
baeapes.live shows high-risk / scam indicators.
| What this site appears to be | An NFT mint and token-claim page for the BaeBieZ collection on ApeChain that asks visitors to connect a wallet and sign transactions to claim $BAEZ. It promises monthly ApeCoin royalties and passive income for holders and stakers, but gives no verifiable legal entity, audit, team identity, or contact or physical address to support those claims. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 8 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 22 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20263 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
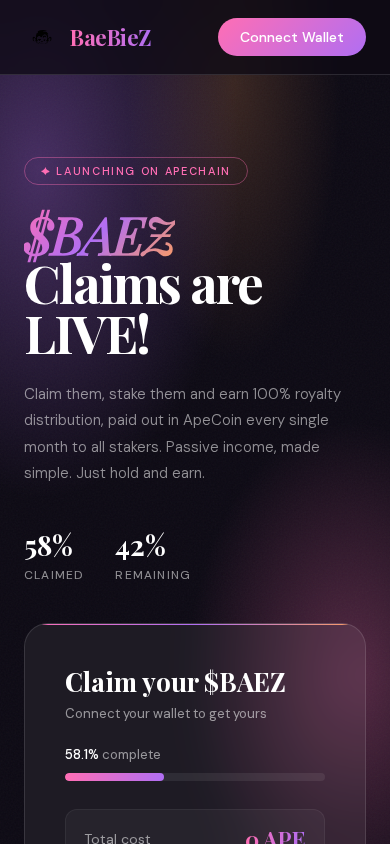
This website is a single-page NFT mint and token-claim portal for a collection called BaeBieZ, presented "by Bae Apes" and deployed on ApeChain. It invites visitors to connect a crypto wallet and sign transactions to claim a token called $BAEZ, and it promotes a 4,444-piece generative collection. The apparent business model is primary NFT sales plus a token claim, with staking and a built-in marketplace that keep holders engaged.
Scam/Impersonation Risk
Confirmed contradictions are present. The domain has been flagged as malicious by several independent threat sources, including multiple tier-one security vendors, and this amounts to a confirmed blacklist hit. No conflicting legal identities and no brand impersonation were detected, and the page shows no credential-harvesting form. The risk therefore comes from the reputation findings combined with the content of the offer itself. The homepage says "Claims are LIVE!" and tells visitors to "claim them, stake them and earn 100% royalty distribution, paid out in ApeCoin every single month to all stakers," adding "Passive income, made simple. Just hold and earn." A guaranteed full royalty pass-through with no named revenue source, audit, or contract verification is an aggressive yield promise that the site does not back up. The page shows a progress counter reading 58% claimed and a "0 APE" total cost. Both are unverifiable on-page urgency and scarcity cues that push visitors toward connecting a wallet. The wallet selector offers EVM, Solana, TRON and XRP networks, a long list of wallet brands, and a "Manual Claim" route "for other networks and wallets." Collecting signatures across that many ecosystems is unusual for a collection that says it lives on one chain. Behaviour testing also saw a large share of requests, including many POST submissions, going to non-allowlisted third-party destinations. The "by Bae Apes" attribution and the outbound link to a separate Bae Apes domain are the site's own claims, and nothing independently ties this domain to that brand. Evidence:
- Homepage: monthly ApeCoin "100% royalty" payouts and "passive income" are promised for holders and stakers, with no audit, team identity, or contract verification shown.
- Homepage: a 58% claimed counter and a "0 APE" cost label sit beside repeated connect-wallet prompts and a transaction-signing flow.
- Domain provenance: registered September 2026 (~0.06 years, about three weeks old), with only 3 archive snapshots spanning 2026-09-28 to 2026-10-09 (1 year tracked). This is a very young domain with no earlier history.
- Behavioural testing: 15 external XHR calls and 12 external POST submissions, 9 of each to non-allowlisted destinations, plus 9 console errors across 3 runs.
Regulatory Verification Notes
The site names no legal entity, operating company, registered address, licence, or responsible team. It publishes no contact channel beyond social links to X and Discord. The homepage describes a monthly income stream tied to token holding and staking but cites no regulatory status or investor disclosures. Staking depends on an external site that is outside the evidence reviewed here. This leaves ownership and governance opaque, and the registration details are incomplete. The identity of the real-world operator is not independently verified. The site presents itself as a Web3 project with passive-income mechanics, which is a category that regulators in many jurisdictions treat as investment-like. Because the site claims no licence, this is a disclosure gap in the context of high-stakes financial activity. It is not a scam finding on its own. No regulated-broker match exists, and no third-party reputational record was found for the project. Evidence:
- Homepage: no company name, jurisdiction, team, or physical address appears, and the page links out to only one separate external domain.
- Homepage: staking, a marketplace and a "metaverse avatars and wearables" utility are described without terms, risk disclosure, or contract references.
- Transport security: the site uses a domain-validated TLS certificate issued by YE2, valid to 2026-12-27. This confirms only encrypted transport, not operator identity.
- Registration: domain registered through NICENIC INTERNATIONAL GROUP CO., LIMITED, with registration expiring 2027-09-28.
- DeFi directory check: no recognition of the project as a listed DeFi protocol.
What to Verify Next
Any claim of affiliation with the Bae Apes brand should be confirmed only through that brand's own officially known channels, reached independently rather than through links on this page. The token contract address for $BAEZ and the staking contract should be checked on a public ApeChain block explorer for verified source code, holder concentration, and admin or mint privileges before any signature is considered. The source of the promised ApeCoin royalties should be traced to a documented revenue stream. A named, accountable team and a contact route reachable outside the website should also be confirmed. Evidence:
- Homepage: ApeChain (Chain ID 33139) is the stated network, so contract details can be checked on-chain without touching the site.
- Homepage: the collection is stated as 4,444 NFTs with over 260 hand-drawn traits, and these figures can be compared against official collection pages.
- Homepage: the staking function is hosted off-site, so its operator needs separate verification.
Summary Verdict
The domain sits in the lowest trust tier and carries an elevated, clearly cautionary risk assessment. Confirmed external threat detections, a newly created domain with no operating history, and an unsubstantiated passive-income offer converge on one conclusion: the site is a high-stakes crypto transaction flow with no accountable counterparty. The reputation findings are decisive and cannot be offset by the site's polished interface, its valid encryption, or its mainstream hosting. Apparent legitimacy cannot be inferred from any of these.
Infrastructure Integrity
The site is served through Cloudflare (AS13335, US), and all four observed addresses are edge nodes of that network, so the origin server is not visible. This protective layer is a mitigating factor only. It improves availability and filters some attacks, but it neither validates the operator nor addresses the reputation findings. It also limits independent hosting verification and can mask rapid content changes on a site this young.
Closing Assessment
At most, the site may be viewed read-only. Wallets should not be connected, no transactions or messages should be signed, and no funds, tokens, or NFTs should be committed. Interaction should wait until an independent party has verified the operator and the associated contracts and the site's reputation status has cleared.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, page content, history in the web archive.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 55/100 |
| Identity verification confidence | 60% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of baeapes.live.
- The request stayed on baeapes.live. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-28. Noted
- The earliest public archive of this site is from 2026-09-28. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3037::6815:239c |
| Name servers | bonnie.ns.cloudflare.com, michael.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2026-12-27 |
| Domain age | 0.06 years (continuous registration) |
| Domain expiry | 2027-09-28 |
| Archive first seen | 2026-09-28 |
| Archive snapshots | 3 |
| Reputation | VirusTotal: 8 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about baeapes.live at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.