Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
beam-sol.com shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: An ownership check raised a concern: the registration record did not name the registrant. On its own this does not say who runs the site or that anything is wrong with it.
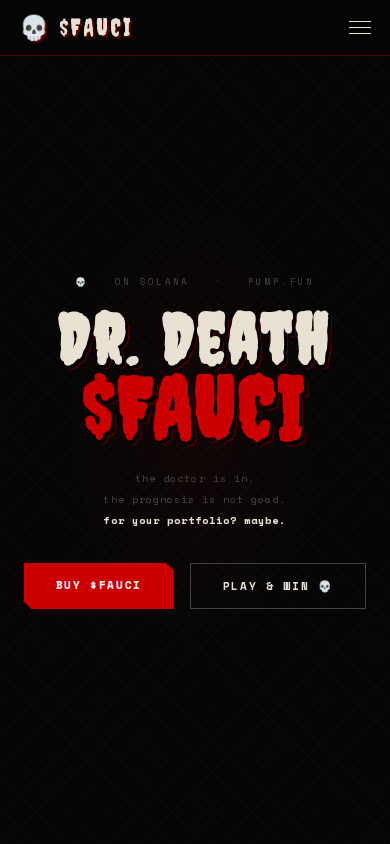
| How the site describes itself | A Solana memecoin landing page for $FAUCI (pump.fun), with a Buy CTA, live market stats, a holders-only browser game, and a contract address. It disclaims financial advice and any expected return, and it lists no team, legal entity, or roadmap. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 9 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 9 months oldRegistered 2026-02-05 | Watch |
| Web archive | Archived since 20266 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-02-05).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Overview
This website is a single-page promotional landing site for "$FAUCI" ("Dr. Death"), a Solana memecoin launched on pump.fun. It presents a skull-themed brand, a prominent "Buy $FAUCI" button, a live market-statistics panel, a copyable token contract address, and a browser mini-game called "Hospital Run". Its apparent business model is to drive visitors to purchase a speculative token. A holders-only game reward adds a further incentive to buy.
Scam/Impersonation Risk
This is an elevated-risk site, and the contradictions are confirmed rather than inferred. Multiple major security vendors currently flag the domain as malicious, and an external reputation source also lists it as blacklisted. The blacklisting is the decisive negative signal. The page-level analysis found no brand impersonation, no login or credential forms, no hidden forms, no wallet-drainer or clipboard-hijack behaviour, and no cloaking. The risk therefore comes from the confirmed external listings and the nature of the offer, not from a detected phishing kit. No conflicting legal identities appear, because the site names no legal entity at all. The domain name suggests a different project from the "$FAUCI" brand shown on the page, which adds to the difficulty of tying the site to any accountable party. The offer is also commercially thin. The page itself shows a market capitalisation of only a few thousand dollars, about nine purchases and fourteen transactions in 24 hours, and trading volume under one thousand dollars. Liquidity this shallow is easily manipulated, and a buyer could struggle to exit a position. The copy says "No presale. No roadmap" and "The prognosis: nobody knows. The treatment: buy." These lines are openly irreverent, and they confirm there is no team, product, or plan. The holders-only game promises "SCORE 1000+ POINTS TO WIN $FAUCI". The leaderboard shows only truncated wallet addresses with scores and cannot be independently confirmed. The token-gated reward adds conversion pressure to buy before playing. The site does include "not financial advice" language and states the token has no intrinsic value or expected return. A disclaimer does not offset an active blacklisting, and the page's candour about speculation does not make the listing benign.
- Homepage: the market panel shows a market capitalisation of about $7.1K, 24-hour volume of $912.32, 9 buys and 14 transactions, which indicates a very thin and easily manipulated market.
- Homepage: the "Hospital Run" game states "SCORE 1000+ POINTS TO WIN $FAUCI · HOLDERS ONLY", and its leaderboard lists only truncated wallet addresses with point totals.
- Homepage: the copy reads "No presale. No roadmap" and names no team, company, or contact beyond social and trading-platform links.
- Domain provenance: registered on 2026-02-05 (about 0.75 years old), with only 6 archive snapshots, all in 2026, covering about 1 year tracked.
Regulatory Verification Notes
The site discloses no company name, jurisdiction, licence, registration number, or physical address. It has no terms, privacy, or about pages, and its only outbound links go to social and trading-data platforms. Ownership is not verifiably connected to any real-world person or entity, and the operator's identity remains unverified. For a token marketed to retail buyers, this gap matters more because the site provides no accountable party to hold responsible. The missing disclosures are verification gaps in their own right. They are not proof of fraud, but they sit alongside the confirmed external listings. The site makes no claim of regulation, and no third-party broker or regulator record is associated with it. The only disclaimer is the on-page "not financial advice" statement, which is not a regulatory disclosure. The transport-layer and hosting facts below confirm that the site is technically operational. They say nothing about who runs it or whether it is lawful.
- Homepage: no legal entity, licence, registration number, team, or postal address is stated anywhere on the page.
- Homepage: the footer links lead only to pump.fun, X (Twitter), DexScreener and Birdeye, with no internal legal pages.
- Domain registration through Global Domain Group LLC, created 2026-02-05 and expiring 2027-02-05.
- Served from AS13335 (Cloudflare, Inc., US); TLS certificate issued by WE1 (DV, domain validation only), valid to 2026-12-22.
What to Verify Next
Before any financial interaction, an independent assessor should check the token's on-chain record. That includes holder concentration, the deployer wallet's history, liquidity depth, and whether the leaderboard wallets correspond to genuine holders. The listed security vendors can be asked to explain their detections. Any claim of a team or project identity should be confirmed through channels independent of this domain. The official token address should be cross-checked on pump.fun rather than copied from this page, since the page's copy-to-clipboard contract field is the point where a visitor commits funds. It would also help to confirm the official support and contact channels. The game's prize mechanics should be treated as unproven until a payout to a genuine third-party wallet is independently observed.
- Homepage: the contract address is displayed with a "click to copy" control, so it should be compared against the pump.fun listing itself.
- Homepage: the game and leaderboard make unverified reward claims that a prospective buyer could test only by spending funds.
- External reputation: the domain currently carries multiple malicious and suspicious detections from security vendors, and any purchase decision should wait for these to be re-checked and cleared.
Summary Verdict
This is a high-risk site carrying a confirmed adverse reputation. Its clean technical presentation, with a valid certificate and no detected malicious page behaviour, does not change that outcome. It is a new, anonymous, speculative token promotion with no verifiable operator and no accountable disclosures. The overall posture is clearly cautionary.
Infrastructure Integrity
The domain resolves entirely to Cloudflare's content-delivery and web-application-firewall edge network. Four edge addresses were observed, and no origin server could be identified. This is a mitigating factor only. It shows professional hosting and reduces direct exposure of the origin. It also means the underlying host cannot be independently identified, and content could be changed quickly behind the edge. The protection does not offset the confirmed external detections.
Closing Assessment
Read-only viewing is the only appropriate use. Wallet connections, purchases, and any financial interaction should be avoided, and no files should be downloaded from the site. Anyone still interested in the token should research it through independent on-chain sources rather than through this domain.
Written analysis generated 2026-11-06 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content, and registration and ownership.
01 External reputation
- A confirmed external listing marks this domain as malicious: at least five security engines including a leading vendor, ten engines, or Google Safe Browsing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Registration and ownership
- The registration record did not name the registrant.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of beam-sol.com.
- The request stayed on beam-sol.com. It was not redirected to another domain. Clear
- Registered through Global Domain Group LLC. Noted
- DNS for this domain is served by ns.cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-02-05. Noted
- The earliest public archive of this site is from 2026-02-05. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Global Domain Group LLC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3035::ac43:dc93 (a CDN edge address; the server behind it was not observed) |
| Name servers | eva.ns.cloudflare.com, rohin.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-22 |
| Domain age | 274 days (registered 2026-02-05) |
| Domain expiry | 2027-02-05 |
| Archive first seen | 2026-02-05 (274 days before capture) |
| Archive snapshots | 6 |
| Reputation | VirusTotal: 9 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about beam-sol.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.