Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
beradrome.pro shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: An ownership check raised a concern: the registration record did not name the registrant. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | Beradrome is a DeFi dApp on Berachain offering token swaps, BERO restaking into hiBERO, LP farming, ve(3,3) gauge voting with bribes, BGT delegation to its validator, and a Tour de Berance NFT collection. The page claims audits, non-custodial custody, open-source code and a bug bounty, but names no auditor and links no reports or repositories in the captured text. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-10-29 and re-scored on 2026-11-04. The certificate, the registration age and the page content describe the site as it was on 2026-10-29.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 5 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 10% confidenceAbuseIPDB, 5 reports; shared hosting inflates reports | Clear |
| Domain age | 3 months oldRegistered 2026-07-24 | Risk |
| Web archive | Archived since 20262 snapshots; the archive has almost no record of this site, which counted against it | Watch |
| Certificate | Encrypted connectionIssued by YR2 | Noted |
The page as captured
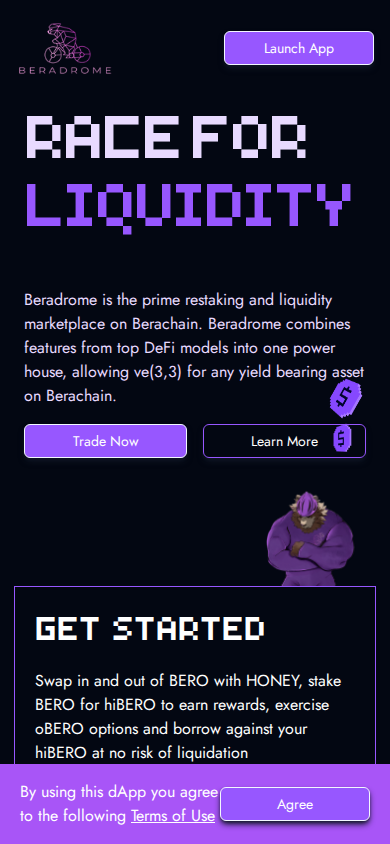
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-07-24).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
Fortinet, Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Overview
Beradrome is a decentralised-finance application landing page for a liquidity and restaking marketplace on the Berachain network. It presents a swap interface, restaking of its BERO token into a staked form called hiBERO, liquidity-pool farms, gauge voting in which projects pay "bribes" to attract emissions, a boost mechanism that delegates BGT to its own validator, and a Tour de Berance NFT collection. The apparent business model is to earn trading fees and route protocol token emissions, while users deposit or lock tokens in return for yield.
Scam/Impersonation Risk
The assessment is clearly cautionary. Several independent security engines flag the domain as malicious or suspicious, including two top-tier vendors. This amounts to a confirmed blacklisting, and it is the decisive finding. Abuse reports also exist against the hosting address. They attach to a shared provider range rather than to this site specifically, so they are corroborating context, not an independent accusation. Nothing observed amounts to impersonation of a known brand or to conflicting legal identities. The homepage also cites two different "official" domains, one on a ".pro" and one on a ".com" suffix. A visitor cannot tell which is authentic, and that is a real exposure for a service that asks users to connect wallets and lock assets. The product design adds structural risk. Users deposit LP tokens and lock BERO before any return is realised. The page promises "higher yields" and "passive income". It also advertises borrowing against hiBERO "at no risk of liquidation", an absolute claim given without any mechanism or supporting evidence. The page names no auditor, yet it asserts audits, open-source code and a bug bounty. The domain is also very new. Taken together, these points read as a fresh deployment whose safety claims cannot be tested from the site itself. On the positive side, behavioural testing found no hidden forms, no cross-site credential capture, no clipboard manipulation and no wallet-drainer behaviour. That does not offset the external threat listing.
- Homepage and domain: registered 2026-07-24 (~0.26 years old) through Atak Domain Bilgi Teknolojileri A.Ş., with expiry on 2027-07-24.
- Web archive: only 2 snapshots, both in 2026 (first 2026-07-28, last 2026-10-11; 1 year tracked), so no established history exists.
- Reputation checks: 5 engines rated the domain malicious and 3 suspicious. Five abuse reports were filed against the hosting IP, with the most recent about a week before analysis.
- Behavioural sandbox: three runs returned stable HTTP 200 responses, with zero external POSTs, zero non-whitelisted XHR calls and zero wallet-drainer or clipboard-hijack events.An XHR request is a request the page sends in the background while it is open, to load or send data without reloading.
Regulatory Verification Notes
The site does not claim any financial licence, registration or regulator oversight. Its non-custodial positioning is therefore the only legal-style assurance it offers. The audit, open-source and bug-bounty claims are the main disclosure gap. The captured page links no audit reports, no code repositories and no bounty programme, so the statements cannot be checked. The page does carry a risk-disclosure section and documentation links, which shows some effort toward transparency. No operating company or accountable individual is connected to the site, so the operator's real-world identity remains unverified. No third-party broker or regulatory database lists the site. Its supporting technical credentials are basic: a standard domain-validated certificate and ordinary hosting.
- Terms and legal content: the captured homepage content shows no licence, authority or registration number, and none is claimed.
- Homepage FAQ: it covers wallets, tokenomics and governance risk, but it does not point to any named audit firm.
- Hosting: served from AS59692 (IQWeb FZ-LLC, AE), registered under RIPE NCC.
- Transport encryption: the TLS certificate is issued by YR2 at domain-validation (DV) level and is valid to 2027-01-13.
What to Verify Next
Before any engagement, an independent route should settle which of the two cited domains the project officially uses. Suitable routes are the network's own ecosystem listings, an established block explorer, or the project's long-standing community channels. Any audit named by the project should be checked on the audit firm's own site, where the report scope, date and contract addresses can be matched. Contract and validator addresses should be compared with the network's public explorer, not with addresses shown on this site. The threat listing should be re-checked later, since vendors sometimes clear listings after remediation. Support and contact channels should be confirmed through an independent route.
- Homepage links: outbound references are limited to documentation, a public block explorer and the network's RPC endpoint, so none of the project's own claims can be checked independently from the site.
- Token set: the six named tokens (BERO, hiBERO, oBERO, veBERO, BGT, HONEY) have no verifiable contract references in the captured text.
- NFT collection: the page says Tour de Berance runs on a different chain (Arbitrum) from the main application, which adds a second set of contracts to confirm.
Summary Verdict
The site presents as a technically functional but unproven DeFi front end, and external threat intelligence outweighs its polished product presentation. Identity is unverified and the domain is very new. Its safety claims cannot be tested, so the posture is firmly high-risk for any sensitive or financial interaction.
Infrastructure Integrity
The site resolves to a single IP at a UAE-based hosting provider (IQWeb FZ-LLC, AS59692). It sits behind no CDN or web-application firewall, so it has no edge-level protection layer. Because the server is directly exposed, infrastructure offers no mitigation against the reputation concerns. The transport certificate is valid, but this is a baseline hygiene measure and does not support legitimacy.
Closing Assessment
Browsing the public pages without interaction is the only appropriate use. Wallet connections, token approvals, deposits, staking, NFT purchases and any credential entry should be avoided until reputable independent sources confirm the project's authentic domain and its security reviews, and the external threat listings are cleared.
Written analysis generated 2026-11-04 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content, history in the web archive, hosting and network, and registration and ownership.
01 External reputation
- A confirmed external listing marks this domain as malicious: at least five security engines including a leading vendor, ten engines, or Google Safe Browsing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME
03 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
04 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, three to six months before capture.Hosting and network
rule:DNS_YOUNG_6M
05 Registration and ownership
- The registration record did not name the registrant.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 5 reports on hosting IP 186.2.175.35 (IQWEB), 10% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of beradrome.pro.
- The request stayed on beradrome.pro. It was not redirected to another domain. Clear
- Registered through Atak Domain Bilgi Teknolojileri A.Ş. Noted
- DNS for this domain is served by trustname.com, across 2 name servers. Noted
- The domain is registered until 2027-07-24. Noted
- The earliest public archive of this site is from 2026-07-28. Watch
- It is hosted on IQWEB, a network registered in AE. Noted
Domain intelligence
| Registrar | Atak Domain Bilgi Teknolojileri A.Ş. |
|---|---|
| Hosting | IQWEB - IQWeb FZ-LLC |
| Network registered in | AE |
| Server IP | 186.2.175.35 |
| Name servers | zeus.trustname.com, ares.trustname.com |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR2 |
| SSL expiry | 2027-01-13 |
| Domain age | 97 days (registered 2026-07-24) |
| Domain expiry | 2027-07-24 |
| Archive first seen | 2026-07-28 (93 days before capture) |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 5 malicious | AbuseIPDB: 10% confidence, 5 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about beradrome.pro at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.