Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
bitweb3git.vercel.app shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 16 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 92 reports; shared hosting inflates reports | Clear |
| Domain age | 3 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20261 snapshot | Clear |
| Certificate | Encrypted connectionIssued by WR1 | Noted |
The page as captured
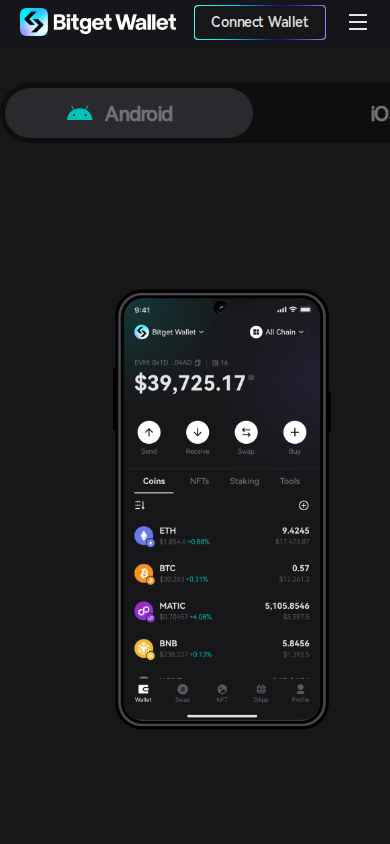
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website is a single-page download portal titled for the Bitget Wallet application. It offers iOS, Android and Google Chrome installs, and it sits on a free, generic subdomain of a developer hosting platform rather than on a branded domain. It presents itself as a distribution point for a self-custody crypto wallet. Nothing on the site establishes who operates it or that it is affiliated with the wallet brand it uses. Its apparent purpose is to steer visitors toward installing wallet software.
Scam/Impersonation Risk
This is a high-risk site, and the convergence of independent signals is what drives that conclusion. The site is blacklisted by external reputation sources, and a large cluster of security engines classify it as malicious, including two tier-one engines. A wallet-download lure on a throwaway subdomain is a well-known pattern for distributing trojanised installers or harvesting seed phrases. The behavioural sandbox also recorded strong cloaking. After simulated interaction, the homepage's rendered content diverged materially from its initial state, with a very large number of DOM mutations and repeated console errors. That behaviour fits a page that presents one face to scanners and another to engaged visitors. The sandbox did not observe wallet-connection prompts, wallet-drainer routines, clipboard manipulation, hidden forms or external password posts. External requests also went only to recognised destinations. These absences do not offset the reputation and cloaking findings. A large volume of abuse reports exists for the hosting address, but it belongs to shared provider infrastructure and carries no confidence against this site specifically, so it is discounted as evidence. No conflicting legal identities were found. The wallet branding on a generic subdomain is a lure risk that is not confirmed as brand impersonation. No suspicious contact address was published on the captured page. Evidence:
- Homepage: the title advertises a Bitget Wallet download for iOS, Android and Chrome, hosted on a free platform subdomain with no brand-owned domain.
- Homepage behaviour: strong post-interaction cloaking, with a semantic content shift of about 15% and 1,423 DOM mutations in a single run. 10 console errors were logged across 3 sandbox runs.
- Reputation: 16 engines flag the site as malicious and 1 as suspicious, including two tier-one engines. This triggered an external-detection override.
- Provenance: domain registered in 2026 (about 86 days old, ~0.24 years). The web archive holds 1 snapshot, captured 2026-08-04, so no established history exists.
Regulatory Verification Notes
The captured homepage discloses no operating company, jurisdiction, licence, registration number, support channel or legal pages. Ownership and governance are opaque, and nothing can be independently tied to a real-world entity. This is a verification gap rather than evidence of wrongdoing on its own. Here, however, it compounds the reputational findings and leaves no accountable party to contact if software obtained from the site causes loss. A search of the third-party broker reputation dataset returned no match. That is neutral context, not a regulatory finding, and the site is not presented as a regulated or licensed service. Evidence:
- Homepage: no operator name, address, licence or registration reference and no terms or privacy pages were identified.
- Hosting: served from AS16509 (AMAZON-02, Amazon.com, Inc., US), with the hosting address attributed by abuse data to Vercel, Inc.
- Transport security: TLS certificate issued by WR1 (domain-validated only), valid to 2026-11-27 with 29 days remaining. This confirms encryption only, not operator identity.
What to Verify Next
Anyone who wants the Bitget Wallet application should obtain it only from the official website, which should be typed manually or reached from the vendor's verified social profiles. Official app-store listings with the publisher's verified name are the other acceptable source. The vendor's official support channel can confirm in writing whether this address is an authorised distribution point. Any file already downloaded from this site should not be installed. If one was installed, it should be scanned, and any wallet that interacted with it should be treated as compromised. Funds and recovery phrases should then be moved to a fresh wallet generated on a clean device. Evidence:
- Homepage: the site presents itself as a source of wallet installers for three platforms, which is the highest-impact delivery vector to validate.
- Reputation: external malicious classifications mean any package from this origin is untrusted until independently cleared.
- Domain history: a registration under three months old with a single archive capture offers no track record to rely on.
Summary Verdict
The authoritative posture is critical-risk and clearly cautionary. Multiple independent external detections and evasive page behaviour outweigh the technically valid but unremarkable security hygiene. The operator's identity is unestablished, and the site is unsuitable for any sensitive interaction.
Infrastructure Integrity
The site resolves to edge addresses on Amazon-hosted network ranges, delivered through a recognised provider's edge network behind a valid certificate, with consistent availability across sandbox runs. The origin server was not observable. These are mitigating hygiene factors only. Protective infrastructure is available to any tenant on the platform, so it cannot offset the external threat detections or the cloaking behaviour.
Closing Assessment
Treat this address as read-only at most. Do not log in, connect a wallet, enter a recovery phrase, make payments or download or run any file from it. Obtain wallet software exclusively through the vendor's officially verified channels, and report the page to the hosting platform and the wallet vendor.
Written analysis generated 2026-10-29 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, behaviour in a sandbox, history in the web archive.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Behaviour in a sandbox
- The structure of the page changed sharply while it was loading.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - A large share of what the page loaded came from other domains.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_MODERATE
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Signals weighed against the site
- AbuseIPDB: 92 reports on hosting IP 64.29.17.195 (Vercel, Inc, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of bitweb3git.vercel.app.
- The request stayed on bitweb3git.vercel.app. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-08-04. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 64.29.17.195 |
| Name servers | Not available |
| CDN / edge network | Detected |
| Resolved IP addresses | 6 |
| Edge IP addresses | 6 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| Domain age | 0.24 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2026-08-04 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 16 flagged | AbuseIPDB: 0% confidence, 92 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about bitweb3git.vercel.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.