Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
bridger.fi shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: The governance checks raised a concern: a threat-intelligence listing limits the score; the registration record did not give the registrant or the registrant's country. The findings below give the detail.
| How the site describes itself | This page is an openly labelled, unaffiliated recreation of the Aave lending interface. It shows simulated earning rates, stablecoin borrow and supply figures, and 'add money' and 'get started' calls to action. It states that Aave Labs does not operate it and that its figures are illustrative, not live. No operator, legal identity, or verifiable service is disclosed, so the money-related promises cannot be verified. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-10-22 and re-scored on 2026-11-04. The certificate, the registration age and the page content describe the site as it was on 2026-10-22.
- The real-world operator identity was not independently verified.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 5/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | Threat-listing ceilingA threat-intelligence feed TrustSniffer monitors listed a file on this site as malicious when the evidence was captured, and that listing caps the score. | Risk |
|---|---|---|
| Malware engines | None flagged itVirusTotal | Clear |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 21 days oldRegistered 2026-10-01 | Risk |
| Web archive | Archived since 20263 snapshots; the archive has almost no record of this site, which counted against it | Watch |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-10-01).
- Public web-archive history exists since 2026.
- No flags from the reputation services TrustSniffer consulted when the evidence was captured.
Full analysis
Overview
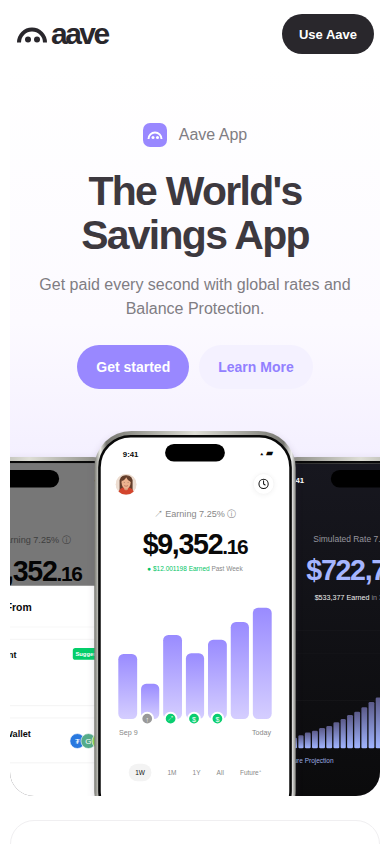
A single-page marketing site presenting itself as an "Interface Recreation" of the Aave decentralised lending app. It shows mock-ups of a savings screen and a professional borrowing dashboard, with "Get started" and "Add Money From Bank Account" calls to action. The page says it is independent of Aave Labs and that its figures are simulated. Its apparent purpose is to promote a stablecoin savings and borrowing experience while naming no operator that would stand behind any funds.
Scam/Impersonation Risk
A threat-intelligence feed currently lists this site as distributing phishing, with the most recent sighting only days before this assessment. This is the decisive finding. It is consistent with the site acting as a source of the activity rather than a compromised victim, although the feed's attribution is a third-party assertion that we have not independently confirmed. It also caps the overall assessment at its lowest tier. The listing is a blacklist-type hit from a single feed. Separately, no conflicting legal entities and no explicit brand-impersonation flag were observed, because the page declares its unaffiliated status. That disclaimer is a genuine transparency point, but it is the page's own statement and does not neutralise the risk. The page reproduces a recognisable lending interface and pairs it with money-movement prompts. It advertises a 7.25% "Earning" rate and the promise to "get paid every second". It also shows a projected $533,377 gain over 30 years and a bank-funded deposit option of up to £15,000. The page also displays a truncated wallet address and market tables for USDT, USDC, GHO and Wrapped BTC. Together with the token references to AAVE, USDe and sUSDe, these give visitors the familiar look of a trusted protocol. Visitors could therefore be led to believe a real deposit channel exists. The page names no custodian, no counterparty and no revenue source, so nothing explains where deposited money would go. Interactive testing showed no wallet-connection attempts, hidden forms or cloaking. This is a favourable observation, but it is discounted because it covers only on-page behaviour at the time of testing and does not address the listing or the lure. The concern is the lure and the unexplained money flow, not observed on-page malware behaviour.
- The homepage presents simulated earning, projection and borrowing tables beside "Add Money" and "Get started" prompts, with no operator named.
- The domain was registered on 2026-10-01 (~0.06 years old, about three weeks) and is registered through Immaterialism Ltd.
- The web archive holds only 3 snapshots, spanning 2026-10-01 to 2026-10-11 (1 year tracked), so there is no meaningful prior history.
- A threat-intelligence feed lists the site as a phishing actor, last seen 2026-10-18.
Regulatory Verification Notes
The site has no legal, terms, about or licensing disclosure that links it to a regulated entity. It names no company, jurisdiction, licence, custody arrangement or complaints route. Yet it invites bank-funded deposits and advertises yield. For a site that solicits money, these omissions are significant verification gaps. No third-party broker or regulatory match was found, so no external reputation signal offers any offsetting assurance. The only identity-related statement is the page's own claim of independence from Aave Labs. That claim is not independent confirmation of who runs the site, and the operator's real-world identity remains unverified. A valid transport-encryption certificate is present, but it is a basic domain-validated one. It indicates only that the connection is encrypted and does not speak to the operator's legitimacy.
- The homepage lists no operator, licence number, registered address or custody model.
- The homepage's wording on figures being "illustrative, not live" conflicts with its live-style deposit and "get paid every second" prompts.
- The site is served from AS13335 (CLOUDFLARENET, Cloudflare, Inc., US).
- The TLS certificate is DV-level, issued by YE1 and valid to 2027-01-13.
What to Verify Next
Any interest in this service should begin with independent confirmation of whether the operator exists, rather than with the site's own statements. First, check the official Aave channels directly, reached by typing the address or using a bookmark saved earlier, for any mention of this domain. If none exists, treat the site as having no demonstrated connection to the protocol it imitates. Second, ask the site's operator for a registered legal entity, jurisdiction and financial-services authorisation, and check these against the relevant public registry. Third, confirm through an independent route who holds deposited funds and under what terms. Finally, find and use the official support and contact channels for the platform actually intended, not those on this domain.
- The homepage's "Add Money From Bank Account" option gives no recipient, institution or payment terms to check.
- The "Stay Updated" and "Notify Me" prompts are the only contact route on the page, and they identify no responsible party.
- A phishing listing from a threat-intelligence feed should be re-checked by the reader against current public reputation sources.
Summary Verdict
The overall posture is elevated risk. A current threat-intelligence phishing listing outweighs everything else. The site is very new, has no traceable operator, and presents financial promises that cannot be tested. The visible disclaimers and the cleanly behaving page are discounted because they are the site's own statements or limited observations, and they do not change the conclusion. Trust is not supported at any level that would justify sensitive interaction.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and WAF, and every observed address is an edge address, so the origin server was not observable. This protection is a mitigating factor only. It improves availability and transport quality, but it cannot offset the reputational evidence. The edge-only view also prevents independent verification of the hosting, so the underlying content could change without notice.
Closing Assessment
Limit any interaction to read-only viewing. Do not log in, connect a wallet, supply credentials or payment details, or move funds through this site, and do not act on its yield or projection figures.
Written analysis generated 2026-11-04 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by governance, hosting and network, page content and history in the web archive.
01 Governance
- A threat-intelligence feed TrustSniffer monitors listed a file on this site as malicious when the evidence was captured, and that listing caps the score.Governance
rule:gov_active_threat_listing
02 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, less than three months before capture.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of bridger.fi.
- The request stayed on bridger.fi. It was not redirected to another domain. Clear
- Registered through Immaterialism Ltd. Noted
- The domain is registered until 2027-10-01. Noted
- The earliest public archive of this site is from 2026-10-01. Watch
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Immaterialism Ltd |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3030::6815:4434 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2027-01-13 |
| Domain age | 21 days (registered 2026-10-01) |
| Domain expiry | 2027-10-01 |
| Archive first seen | 2026-10-01 (21 days before capture) |
| Archive snapshots | 3 |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about bridger.fi at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.