Verdict
The site blocked our scan, so nothing was confirmed either way. Treat it as unknown and verify who runs it another way.
catapult-nft.web.app blocked our automated scan and could not be verified.
- Needs Review: The site blocked or cut short the capture, so no verdict was reached.
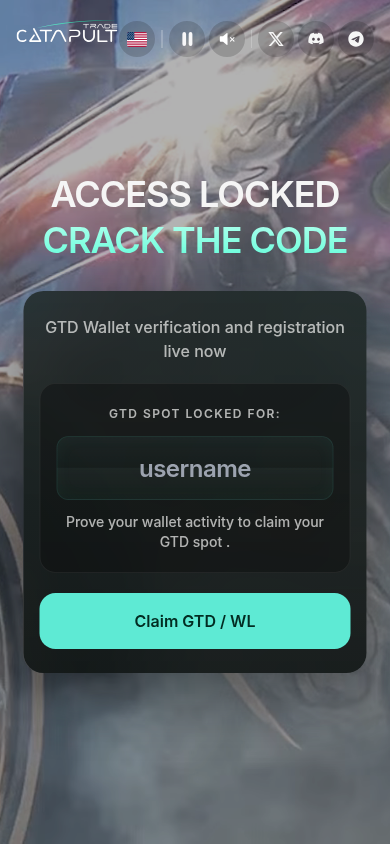
| How the site describes itself | A English-language page branded 'Catapult TRADE' locks a 'GTD' whitelist spot behind proving wallet activity and offers a 'Claim GTD / WL' button. It gives no legal entity, team, contact details, token or product explanation, or description of what the wallet verification does, so the sensitive wallet step is unsupported by evidence. |
|---|
Evidence status and limitations
Evidence completeness: IncompleteThis says whether every check on the site was recorded as finished. The site blocked or cut short our capture, so the result needs review.
- Capture was incomplete or blocked; this result requires review.
- The real-world operator identity was not independently verified.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 4% confidenceAbuseIPDB, 4 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | Not availableNo registration record was returned | Noted |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by WR4 | Noted |
The page as captured
Key findings
- The site blocked automated access, so TrustSniffer could not collect enough evidence to assign a score.
Full analysis
Overview
This is a single-page crypto landing site branded "Catapult TRADE". It opens on an "Access Locked" screen under a "Crack the Code" headline and announces that wallet verification and registration for a guaranteed ("GTD") whitelist spot are live. Its apparent purpose is an airdrop or token-sale style promotion. A visitor is asked to prove on-chain wallet activity to claim a place on an allocation list. The page does not say what token, product or revenue model stands behind the offer.
Scam/Impersonation Risk
No contradictions were observed. There is no phishing indicator, no brand impersonation, no conflicting legal identities and no confirmed threat-list listing. The risk is a lack of substance, not a proven deception. The homepage promises a guaranteed allocation but names no token, project, team or sale terms. It also never explains what the "Claim GTD / WL" wallet step does. Gating a claim behind wallet activity is a common pre-sale mechanic and is also a pattern used to steer users toward signing requests. Because nothing on the page supports the claim, the intent of that step cannot be judged from the page. In the observed browsing runs, the mitigating behaviours were that no wallet-connection prompt, wallet-draining routine, clipboard manipulation, hidden form or password form appeared. Against that, the page generated a large volume of outbound network activity for such a small amount of content. That included POST requests to destinations outside the recognised set, and the behaviour analysis classed the network pattern as suspicious. The reputation signals are soft and not site-specific. One scanning engine returned a single unconfirmed "suspicious" flag. A handful of abuse reports attach to a shared edge address of the hosting provider, which serves many unrelated sites. The "nft" wording in the domain name does not match the "TRADE" branding on the page, which fits an unfinished or hastily assembled promotion.
- Homepage text is only about 189 characters, with no token, team, roadmap or terms of the allocation.
- Behavioural runs (3 of 3 completed) recorded 43 external XHR requests and 32 external POSTs, 2 of the POSTs to non-recognised destinations, plus 67 console errors. No wallet-connect, drainer, clipboard-hijack or hidden-form behaviour was detected.An XHR request is a request the page sends in the background while it is open, to load or send data without reloading. "External" means it went to a different website than the one you opened. A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Reputation checks: 1 suspicious flag and 0 malicious flags from the scanning engines, and 4 abuse reports against the shared provider address, an attribution that applies to shared infrastructure.
Regulatory Verification Notes
The homepage names no legal entity, operator, jurisdiction, licence, registration number, physical address or contact channel. It carries no links to terms, privacy or about pages, and it has no page title or meta description. This is a content gap on the site itself. It is not evidence of wrongdoing on its own, but it leaves the operator unidentified. The domain is also a subdomain on a shared application-hosting suffix, so the parent domain's registration does not point to the operator. Independent confirmation of the operator is therefore not available from this evidence. No third-party broker or regulatory profile matched this site. That absence is neutral and is neither an endorsement nor a warning. The valid transport encryption shows only that the connection is encrypted. It does not show who runs the site.
- TLS certificate issued by WR4 (domain-validated, DV), valid to 2026-12-22, which confirms encryption only and not operator identity.
- Served from AS54113 (FASTLY - Fastly, Inc., US).
- Homepage has no internal links, no external links and no social-media presence.
- No licence, regulator or registration claim is made anywhere on the page.
What to Verify Next
The first step is to confirm independently that a "Catapult" project and its whitelist exist. This should be done through channels discovered outside this page, such as established project announcements or a team's long-standing official accounts. A link taken from the page itself should not be relied on. Next, the specific actions the wallet step requires should be established before any wallet is connected. A read-only connection differs from a transaction or permission signature, and the page does not say which one is requested. If any financial product or token sale is later offered, the operator's authorisation status should be checked once with the relevant registry of the jurisdiction concerned. Any wallet used for testing should be a separate, low-balance wallet.
- The page describes the wallet check only as "proving wallet activity", without specifying the on-chain actions involved.
- The headline promise of a guaranteed spot cannot be matched to any sale terms or published token details.
- The site's own pages offer no official support or community contact that could serve as a starting point for confirmation.
Summary Verdict
The site reads as a new, thinly documented crypto promotion whose legitimacy cannot be established from available evidence. No confirmed fraud indicators were found, but the combination of an unsupported allocation claim, an unidentified operator and unexplained network behaviour supports a measured, cautionary posture. The assessment is unresolved. It is neither an endorsement nor a finding of malice.
Infrastructure Integrity
The site is delivered through Fastly's content-delivery and edge network, and all observed addresses are edge nodes of that provider. A bot-protection challenge was also observed during testing. This is a reputable, established infrastructure provider, and its presence mitigates exposure of the underlying server. However, protective infrastructure does not indicate legitimacy, and the origin server was not observable behind the edge. The encrypted connection and edge delivery are therefore treated as neutral-to-mildly positive hygiene and not as evidence about the operator.
Closing Assessment
Wallet connections, signatures, payments and the sharing of personal information should wait until the project and its allocation terms have been confirmed through independent, established channels. Until then, viewing the page is a reasonable extent of interaction.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by page content and several checks together.
01 Page content
- The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED - The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN
02 Several checks together
- No external threat source confirms a listing for this site, but its own page content reads as risky.Several checks together
rule:HYB_POSITIVE_EXTERNAL_NEGATIVE_PAGE
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 4 reports on hosting IP 2620:0:890::100 (FASTLY), 4% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of catapult-nft.web.app.
- The request stayed on catapult-nft.web.app. It was not redirected to another domain. Clear
- It is hosted on FASTLY, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | FASTLY - Fastly, Inc. |
| Network registered in | US |
| Server IP | 2620:0:890::100 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (fastly) |
| Resolved IP addresses | 2 |
| Edge IP addresses | 2 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR4 |
| SSL expiry | 2026-12-22 |
| First seen (web archive) | Not available (the web archive has no record of this address; a site on web.app has no registration of its own) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 4% confidence, 4 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about catapult-nft.web.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.