Verdict
The site blocked our scan, so nothing was confirmed either way. Treat it as unknown and verify who runs it another way.
cdn-nodes.vercel.app blocked our automated scan and could not be verified.
- Needs Review: The site blocked or cut short the capture, so no verdict was reached.
| How the site describes itself | Developer-style wrapper page for a Collab.Land connect flow. It explains how to load a signed same-origin iframe path that forwards to a server-side PHP connect backend, using a JWT token and user/server query parameters. No sensitive form, financial action or brand-impersonation signal is visible in the supplied text. |
|---|
Evidence status and limitations
Evidence completeness: IncompleteThis says whether every check on the site was recorded as finished. The site blocked or cut short our capture, so the result needs review.
- Capture was incomplete or blocked; this result requires review.
- The real-world operator identity was not independently verified.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 87 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 12 days before captureWeb archive; a site on vercel.app has no registration of its own | Risk |
| Web archive | Archived since 20261 snapshot; the archive has almost no record of this site, which counted against it | Watch |
| Certificate | Encrypted connectionIssued by WR1 | Noted |
The page as captured
Key findings
- The site blocked automated access, so TrustSniffer could not collect enough evidence to assign a score.
Full analysis
Overview
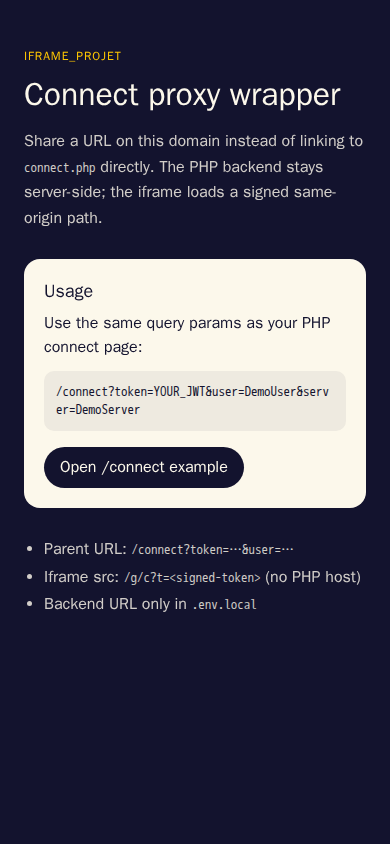
This website is a minimal developer utility page titled "Collab.Land Connect Proxy," hosted as a subdomain on the Vercel application platform. It documents how to share a URL on its own domain instead of linking directly to a PHP connect backend. It shows a signed same-origin iframe path, a connect route that takes a JWT token plus user and server query parameters, and a note that the backend address lives only in a local environment file. Its apparent purpose is to serve as a non-commercial integration wrapper for a Collab.Land community-connect flow. It describes no monetization, products or financial offering.
Scam/Impersonation Risk
No contradictions were observed. No phishing, confirmed threat-feed listing, conflicting legal identities or brand impersonation was found. The homepage contains no login form, no payment or sensitive data entry, and no promises of returns. A brand-similarity flag points at the hosting platform's own domain, which the site is a subdomain of, so it reflects the hosting arrangement rather than a lookalike attack. The generic, infrastructure-sounding subdomain name and the use of a third-party community brand without any visible operator attribution are fair reasons for caution, but they are not evidence of deception. A large number of abuse reports sit against one of the shared platform edge addresses. They are attributed to the provider's multi-tenant infrastructure and discounted accordingly, and they say nothing specific about this site. Only one security engine returned a suspicious result, and it was unconfirmed. Browser-behavior testing recorded a moderate share of outbound requests to destinations outside the common allowlist. These included several outbound POST and XHR calls and a number of console errors, and they warrant the verification steps below. Taken together they count as a soft reputational signal, not a finding of malicious intent.An XHR request is a request the page sends in the background while it is open, to load or send data without reloading. A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Homepage: a 462-character documentation-style page with no forms, no hidden forms and no password fields. It shows only a usage example with a token placeholder and a signed-token iframe path.
- Hosting-layer reputation: 87 abuse reports are recorded against the shared platform edge address 216.198.79.131, but with a zero confidence score, a CDN usage classification and an allowlisted status, so they are discounted as shared-infrastructure noise.
- Browser sandbox, 3 of 3 runs completed: 18 external requests, 12 of them to non-allowlisted hosts, including 6 non-allowlisted POSTs, plus 9 console errors. No cloaking, clipboard manipulation, wallet-drainer behavior or fingerprinting was detected.
- Provenance: a single archive snapshot dated 2026-10-09, with the domain roughly 11 days old (2026), indicating a very recently created deployment.
Regulatory Verification Notes
The page makes no licensing claim and presents no financial service, so there is no regulated-activity claim to test. Nothing on it connects it to a named legal entity or individual. It publishes no operator name, contact channel, terms or privacy page, and no company registration or affiliation statement. No official tie to the Collab.Land brand is stated. This is a disclosure gap in the page content. It is expected for a short-lived developer scaffold but leaves real-world operator identity independently unverified. No third-party broker or regulatory-database record matches this site, so there is no external reputational signal to weigh in either direction.
- Homepage and visible site content: no legal entity, license number, registration, terms or privacy pages, and no named maintainer.
- Transport layer: a valid TLS certificate issued by WR1 (DV, domain validation only), valid to 2026-11-27 (about 37 days remaining), which confirms encryption but not operator identity.
- Hosting: served from AS16509 (AMAZON-02 - Amazon.com, Inc., US), with edge addresses in the US.
- Content categorization: classified as a developer tool / utility page with a low page-level risk band and no red flags.
What to Verify Next
Before using the connect flow, confirm through Collab.Land's own official documentation or support channels that this proxy is an endorsed integration, and identify who deploys and administers this instance. Because the flow passes a JWT in the URL, the intended token scope and lifetime should be confirmed with the party that issues it. The outbound destinations contacted during page load should also be reviewed against the integration's documented dependencies, and any official support or contact channel should be confirmed by an independent route. Until then, an authentic issuance of tokens or any credential is unconfirmed.
- Homepage usage example: the connect route accepts a token plus user and server parameters, so link sharing could expose a live token if misused.
- Browser sandbox: several non-allowlisted outbound POST and XHR destinations that the integration's documentation should account for.
- Homepage: no stated operator or official-integration attribution to cross-check against the vendor's own listings.
Summary Verdict
The site reads as a genuine but unverified, newly created developer utility rather than a fraud vehicle, with no contradictory or deceptive signals. Its trust position is held back by the brevity of its history, the absence of any attributable operator, and unexplained outbound network activity, which together place it in a needs-review posture rather than an established one.
Infrastructure Integrity
The site is served through the Vercel edge network on Amazon cloud infrastructure in the United States, behind a valid TLS certificate from a recognized issuer. All six observed addresses are CDN edge nodes, and the origin server is not observable, so the underlying host cannot be independently confirmed. Edge-only visibility can also mask rapid content changes on a freshly created deployment. The protective, widely used platform is a mitigating factor only and does not establish the legitimacy of the operator.
Closing Assessment
Reading the documentation page is reasonable. Before supplying a token, credentials or any sensitive data to the connect flow, a user should first confirm with the relevant Collab.Land community administrator that this instance is the one they intend to use.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by hosting and network, history in the web archive, page content and behaviour in a sandbox.
01 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, less than three months before capture.Hosting and network
rule:DNS_NEW_DOMAIN_90D
02 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
03 Page content
- The page runs on a free vercel.app address instead of a domain of its own, a setup common to short-lived phishing and claim pages.Page content
rule:PAGE_BRAND_SUSPECTED - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
04 Behaviour in a sandbox
- The page exchanged network traffic with destinations TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_TRAFFIC - The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 87 reports on hosting IP 216.198.79.131 (AMAZON-02), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of cdn-nodes.vercel.app.
- The request stayed on cdn-nodes.vercel.app. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-10-09. Watch
- It is hosted on AMAZON-02, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc. |
| Network registered in | US |
| Server IP | 216.198.79.131 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected |
| Resolved IP addresses | 6 |
| Edge IP addresses | 6 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| First seen (web archive) | 12 days before capture; a site on vercel.app has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2026-10-09 (12 days before capture) |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 87 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about cdn-nodes.vercel.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.