Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
changebit.org shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: The governance checks raised a concern: the kind of site it appears to be limits how high the score can go, because its operator could not be verified; a threat-intelligence listing limits the score; the registration record did not name the registrant. The findings below give the detail.
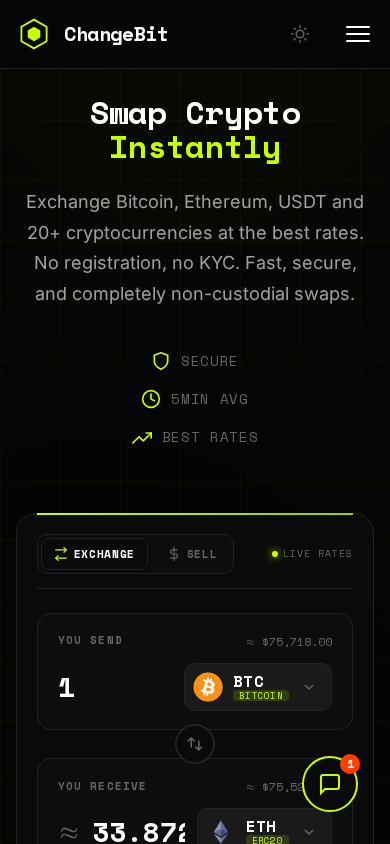
| How the site describes itself | ChangeBit presents itself as a non-custodial cryptocurrency swap service offering no-KYC exchanges across 20+ to 50+ tokens and 15+ networks. Users send crypto to a unique deposit address generated per order, and the platform then forwards the swapped funds. The page makes strong security, audit, and non-custody claims, but it provides no verifiable company identity, licensing, audit reports, or physical address, and its fee disclosures are inconsistent. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The real-world operator identity was not independently verified.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 5/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | Business-model ceiling; Threat-listing ceilingTrustSniffer limits the score of a site whose operator it could not verify, according to the kind of site it appears to be; here that limit is what sets the score. A threat-intelligence feed TrustSniffer monitors listed a file on this site as malicious when the evidence was captured, and that listing caps the score. | Risk |
|---|---|---|
| Malware engines | None flagged itVirusTotal | Clear |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 9 months oldRegistered 2026-02-10 | Watch |
| Web archive | Archived since 202411 snapshots; the history predates the current registration (2026-02-10); an earlier owner may have held the name | Noted |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-02-10).
- Public web-archive history exists since 2024.
- No flags from the reputation services TrustSniffer consulted when the evidence was captured.
Full analysis
Overview
ChangeBit is a cryptocurrency swap website that presents itself as a "non-custodial" instant exchange. Visitors pick a pair from about two dozen major tokens, including Bitcoin, Ethereum, USDT, Solana, XRP and Monero. The site promises no registration, no identity checks and settlement in roughly five minutes. The business model is a per-swap service fee. It depends on visitors sending funds to a deposit address the platform generates for each order.
Scam/Impersonation Risk
A threat-intelligence feed currently carries a malware listing for this domain, and this is the decisive factor in the assessment. The listing attributes the activity to the site itself rather than to a third party. It is a hard contradiction, so the domain is blacklisted on this source, and that overrides every positive technical signal. No phishing, brand-impersonation, identity-inconsistency or registration-based contradiction was confirmed, and no conflicting legal entities appear. The domain name is, however, a close lookalike of a well-known petition platform. That resemblance is an unconfirmed soft signal. It is consistent with the pattern of names chosen to borrow familiarity, but it is not proof of impersonation. The homepage describes a "completely non-custodial" service, yet its own three-step flow tells users to send funds to a platform-generated deposit address, after which the operator forwards the swapped asset. Control of the funds therefore appears to sit with the operator in transit, which is inconsistent with the non-custody claim. The security and audit assertions come with no linked audit report, and the stated fee is inconsistent: the FAQ and terms say 0.15%, while the live swap widget shows 0.25%. The social-proof figures also conflict, with "12,000+" completed exchanges in one place and "285K+" swaps in another. These inconsistencies suggest testimonials and counters that cannot be verified. Irreversible crypto transfers to an operator whose identity is unverified, with no-KYC onboarding and an active malware listing, are a high-loss scenario.
- The threat-intelligence listing is a malware listing against the domain, attributed to the site itself. It is a blacklist-level hard contradiction, and the feed's last sighting is dated late October 2026. The feed does not confirm phishing.
- Domain registered 2026-02-10 (~0.73 years, about nine months old) through Global Domain Group LLC, so the site is young for a service claiming to handle large volumes.
- Homepage swap widget: fee shown as 0.25%, against 0.15% in the FAQ and terms; completed-exchange counters of 12,000+ and 285K+ appear on the same site.
- Homepage "How It Works" section: step three instructs users to send funds to a deposit address, which is inconsistent with the "non-custodial" headline.
Regulatory Verification Notes
The site publishes privacy, terms and anti-money-laundering pages, which indicates policy text exists. None of it ties the service to a named company, a registration number, a licensing authority or a physical address. A swap service holding customer funds in transit is normally expected to disclose these. The omission is a disclosure gap rather than proof of wrongdoing, but here it sits alongside an active malware listing and so adds to the risk instead of being a stand-alone gap. No third-party broker or regulator database matched the site, and no license is claimed. Real-world operator identity remains unverified (identity score 30, confidence 0.5), and ownership details are not apparent from the site's own pages. The 11 archive captures from 2024 to 2026 show continuity of content, but they establish only that the site has existed, not who runs it.
- Terms, privacy and AML pages: present, but they name no legal entity, license or registered office.
- Homepage and contact route: no verifiable physical address or accountable company identity.
- 11 archive snapshots spanning 2024–2026 (3 years tracked), with no signs of repurposing.
- Served from AS13335 (Cloudflare); TLS certificate issued by WE1 (domain-validated only), valid to 2027-01-02.
What to Verify Next
No sensitive action should be taken until the malware listing is cleared. If a prospective user still wishes to assess the service, the starting point is to ask the operator for its legal entity name, registration and licensing details. Each of these should be checked independently with the relevant registry, rather than relying on statements the site makes about itself. Audit claims should be tested by asking for the auditor's name and confirming the report directly with that auditor. Official support channels should be established through an independent, offline route rather than links on the site. Any exchange test should use a trivially small amount, and only after the fee and rate discrepancy has been explained in writing.
- Homepage security and audit claims name no auditor and link no report.
- Fee conflict between the swap widget and the FAQ and terms needs a written explanation from the operator.
- The only transactional surfaces are the order form and a support-ticket form, both of which collect user-supplied details.
- The domain-validated certificate confirms only control of the domain, not the operator's identity.
Summary Verdict
The overall posture is high risk. An active malware listing, a business model that appears to conflict with its own marketing, and the absence of any verified accountable identity all point the same way. Technical hygiene does not offset these findings. The available evidence does not support treating the site as legitimate, and the operator's identity remains unconfirmed.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and web application firewall, and all observed addresses are CDN edge servers, so the origin host is not visible. This is a mitigating factor only. It is consistent with ordinary professional hosting and a valid certificate, but it says nothing about the operator's honesty. Edge-only visibility also makes independent hosting verification harder and can mask rapid content swaps. It does not offset the reputation risk.
Closing Assessment
Do not log in, submit credentials, or send any funds or tokens to deposit addresses generated by this site. Any use should be limited to passive reading until the malware listing is removed and the operator's identity has been independently confirmed. Anyone who has already sent funds or entered details should contact their exchange or wallet provider and secure their accounts immediately.
Written analysis generated 2026-11-06 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by governance and page content.
01 Governance
- TrustSniffer limits the score of a site whose operator it could not verify, according to the kind of site it appears to be; here that limit is what sets the score.Governance
rule:gov_business_model_cap - A threat-intelligence feed TrustSniffer monitors listed a file on this site as malicious when the evidence was captured, and that listing caps the score.Governance
rule:gov_active_threat_listing
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY - The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of changebit.org.
- The request stayed on changebit.org. It was not redirected to another domain. Clear
- Registered through Global Domain Group LLC. Noted
- DNS for this domain is served by ns.cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-02-10. Noted
- The earliest public archive of this name is from 2024-03-01, before the current registration on 2026-02-10; an earlier owner may have held it. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Global Domain Group LLC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3033::6815:2aac (a CDN edge address; the server behind it was not observed) |
| Name servers | piper.ns.cloudflare.com, rene.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-02 |
| Domain age | 269 days (registered 2026-02-10) |
| Domain expiry | 2027-02-10 |
| Archive first seen | 2024-03-01 (2.7 years before capture) |
| Archive snapshots | 11 |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
The web archive has records of this name from 2024-03-01, before the current registration on 2026-02-10. That archive history predates the current registration, and an earlier owner may have held the name.
Server behind Cloudflare
The site is served through Cloudflare, which hides the address of the server behind it. TrustSniffer could not confirm the current server. Public DNS history records where the domain pointed earlier.
| Earlier address (DNS history) | 91.210.166.248 (ROUTE 95 LLC, AS59729, BG), seen 2024-03-01 to 2024-03-04 |
|---|---|
| Earlier address (DNS history) | 176.123.0.245 (AlexHost - ALEXHOST S.R.L., AS200019, MD), seen 2024-02-14 to 2024-02-14 |
Found only from free public records (certificate logs, mail and SPF records, Mnemonic passive DNS, addresses written in the page) and one ordinary request to the address. An earlier address is a record of the past, not proof of where the site runs today.
About this assessment
A trust score summarises the evidence TrustSniffer could collect about changebit.org at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.