Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
cloubflare.net shows high-risk / scam indicators.
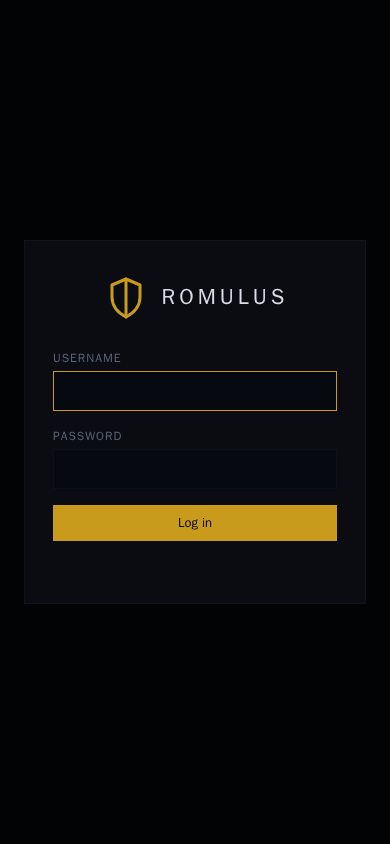
| What this site appears to be | A minimal login page labeled 'Romulus' requesting username and password with no surrounding information about the service or organization. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 9 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 74% confidenceAbuseIPDB, 51 reports; shared hosting inflates reports | Risk |
| Domain age | 1.8 years oldRegistered history | Clear |
| Web archive | Archived since 20241 snapshot | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: 1 to 3 years (registration continuity).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
The website is a minimal authentication portal titled “Romulus,” presenting only username and password fields and a login control; its underlying service, operator, products, and intended business purpose are not identified to visitors.
Scam/Impersonation Risk
The site presents a critical sensitive-interaction risk. The login page requests credentials without explaining the service, organization, account purpose, or contact route, creating a substantial evidence gap for a high-impact interaction. External threat intelligence records the domain as blacklisted, with malicious detections from multiple sources; this is decisive in combination with the credential-only presentation. The hosting-IP abuse reports are attributed to shared provider infrastructure rather than specifically to the site, but they remain an adverse environmental signal. No separate legal-entity identity contradiction was observed.
- The homepage/login page is titled “Romulus” and contains only “Username,” “Password,” and “Log in,” with no service or organization context.
- The login page contains one sensitive credential form and no internal or external explanatory links.
- External reputation checks recorded 9 malicious and 1 suspicious detection, with Fortinet and Sophos among the flagged vendors; the domain was also recorded by an external blacklist.
- The hosting IP, 167.148.201.191, has 51 abuse reports with a confidence score of 74; the attribution is to shared infrastructure operated by MillenialHost Limited.
Regulatory Verification Notes
The available page does not identify a legal entity, licensing authority, registration number, or regulated service, and no terms, privacy, about, or contact disclosures were supplied for review. This is a material transparency deficiency for a site requesting credentials, although the absence of a license claim alone is not proof of fraud. Independent identity verification remains unsuccessful, and the available broker-reputation dataset contains no matching record. The transport certificate is valid but uses domain validation only, which authenticates control of the domain rather than the real-world operator.
- The supplied page content contains no company name, license disclosure, registration number, product description, or contact information.
- The domain-registration record lists NICENIC INTERNATIONAL GROUP CO., LIMITED and a creation date of 2026-10-14, with a WHOIS age value of 0.01 years; the reconciled domain-age record is 1.8288843258042438 years.
- Historical coverage contains 1 archive snapshot spanning 1 year, first seen on 2024-12-17 and last seen on 2024-12-17.
- The site’s TLS certificate is issued by YE1, uses DV validation, and is valid through 2027-01-12T18:36:46+00:00.
What to Verify Next
No credential, payment, or other sensitive interaction should proceed through this portal unless the exact domain and service relationship are independently confirmed through an established, offline or previously trusted channel. Any claimed operator should be matched against the relevant corporate and regulatory registers, and the legitimate service’s official support channel should be accessed from a known-good source rather than from this page. If credentials have already been entered, they should be changed through the confirmed official service and reviewed for related account activity.
- The page’s stated purpose cannot be established beyond credential collection because it provides no product, company, or contact context.
- The available identity status is unverified, with no independent identity signals supplied.
- The page is categorized as “Login-only / Unknown” and carries the documented red flags of no-context login, claim-evidence dissonance, and a high-stakes evidence gap.
Summary Verdict
The website has a critical-risk posture and should not be treated as a trustworthy authentication service. The combination of credential collection without context, confirmed external threat detections, blacklisting, and unresolved operator identity makes the site unsuitable for sensitive interaction.
Infrastructure Integrity
The site is protected by Cloudflare CDN/WAF, and the observed edge infrastructure resolves through AS135392, MILLENIALHOSTLIMITED-AS-GB - MillenialHost Limited, HK; the observed edge address is 167.148.201.191 and no origin candidate was visible. Cloudflare protection and edge-only visibility provide a limited defensive benefit, but they do not establish operator legitimacy or offset the adverse site and reputation signals.
Closing Assessment
Treat the portal as unsuitable for credential or financial use, preserve any relevant evidence of interaction, and rely only on a separately confirmed official service channel for account access or remediation.
Written analysis generated 2026-10-17 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, several checks together.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL - The server address behind this site has a strong record of abuse reports.External reputation
rule:EXT_ABUSEIP_SEVERE
02 Page content
- The page presents itself as a brand TrustSniffer confirmed it does not belong to.Page content
rule:PAGE_BRAND_IMPERSONATION_CONFIRMED - The page loaded on its own domain but had no readable content.Page content
rule:PAGE_CONTENT_EMPTY - The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Signals weighed against the site
- AbuseIPDB: 51 reports on hosting IP 167.148.201.191 (MillenialHost Limited, Data Center/Web Hosting/Transit), 74% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of cloubflare.net.
- The request stayed on cloubflare.net. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-10-14. Noted
- The earliest public archive of this site is from 2024-12-17. Clear
- It is hosted on MILLENIALHOSTLIMITED-AS-GB, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | MILLENIALHOSTLIMITED-AS-GB - MillenialHost Limited, HK |
| Country | US |
| Server IP | 167.148.201.191 |
| Name servers | LEE.NS.CLOUDFLARE.COM, LOVE.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 1 |
| Edge IP addresses | 1 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2027-01-12 |
| Domain age | 1.83 years (continuous registration) |
| Domain expiry | 2027-10-14 |
| Archive first seen | 2024-12-17 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 9 flagged | AbuseIPDB: 74% confidence, 51 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about cloubflare.net at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.