Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
crackedclients.com shows high-risk / scam indicators.
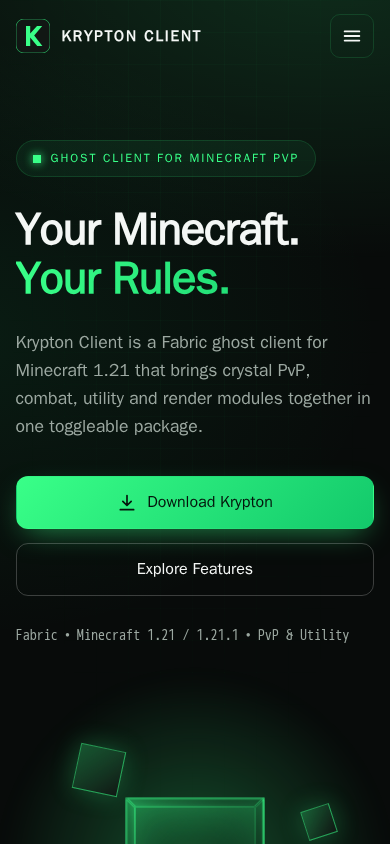
| What this site appears to be | Project page for 'Krypton Client', a Fabric-based Minecraft PvP/utility cheat client. Describes modules, supported Minecraft versions, installation steps and license key usage. Official download link is not configured and community links are marked 'coming soon'. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 1 days oldMost scam domains are under a year old | Risk |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Fortinet, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website presents Krypton Client, a Fabric-based Minecraft 1.21 PvP and utility client marketed through a software-download landing page. It describes combat, farming, rendering, and utility modules, directs visitors toward a license key and local `.jar` installation, and appears intended to distribute a paid game “ghost” client.
Scam/Impersonation Risk
The site has a critical interaction risk driven by confirmed external threat detections and blacklist status. This is not an established identity contradiction or confirmed brand impersonation finding, but the reputational evidence is decisive for sensitive use. The homepage promotes software containing Aim Assist, Auto Clicker, TriggerBot, Kill Aura, Auto Totem, ESP, Freecam, and a self-destruct function; it also directs visitors toward obtaining a license and installing a local `.jar`. The download link is not configured, community links are marked “coming soon,” and contact or address information cannot be independently substantiated from the supplied page evidence. These gaps materially increase the risk associated with executing software obtained through the site.
- External reputation checks recorded 4 malicious and 1 suspicious detections, with Fortinet and Sophos among the flagged vendors; the site is also listed by external blacklist sources.
- The homepage describes Krypton Client as a Fabric “ghost” client for Minecraft 1.21 and lists combat, utility, farming, render, and self-destruct modules.
- The homepage directs visitors to obtain a license key and install a `.jar`, while the official download link is not configured and community links are marked “coming soon.”
- Domain registration telemetry records creation on 2026-10-12, with an age of approximately 0.00 years.
Regulatory Verification Notes
The operator’s real-world identity is unverified, and the supplied site content does not claim a licensing authority or provide a license number. This is a transparency and verification gap rather than, by itself, proof of fraud; however, it is significant alongside the confirmed external threat detections. A valid domain-validated certificate and registration through Cloudflare provide transport and administrative infrastructure, not evidence that the operator is legitimate or authorized to distribute the software.
- The business-model record states that no license authority or license number is claimed or verified on the site.
- The site is registered through Cloudflare, Inc.
- The site is hosted on AS13335, CLOUDFLARENET — Cloudflare, Inc., US.
- TLS is issued by WE1 at DV validation level and is valid through 2027-01-10.
What to Verify Next
Before any sensitive interaction, an independent security review should establish the operator’s identity, confirm whether the software is authorized for the intended Minecraft environment, and validate the provenance and integrity of any installer or `.jar`. Any payment or license transaction should be checked through an independently sourced merchant record and a payment method offering dispute protection. Official support and community channels should be confirmed through an offline or independently obtained source rather than relying solely on the site.
- The homepage provides product and installation instructions but does not configure the official download link.
- The page identifies license-key usage and a paid download model without supplying an independently verified licensing authority.
- The page analysis records unverifiable contact or address information and a high-stakes evidence gap.
Summary Verdict
The website has a critical trust posture and should be treated as unsuitable for sensitive interaction. Available page content and technical stability do not offset the confirmed external threat and blacklist findings, while operator identity remains unverified.
Infrastructure Integrity
Cloudflare CDN/WAF protection is present, and all observed addresses were CDN edge addresses rather than an independently observable origin. This reduces direct exposure of the hosting origin and can mitigate some infrastructure-level attacks, but it is only a protective hosting measure and does not validate the site’s content or operator.
Closing Assessment
Prospective users should limit activity to passive observation and should not log in, submit credentials, make payments, or execute files obtained through the site unless independent identity, provenance, and file-integrity checks have first been completed.
Written analysis generated 2026-10-13 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, page content, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D - The domain is young and has almost nothing else set up around it.Hosting and network
rule:DNS_SPARSE_YOUNG_DOMAIN
03 Page content
- The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME
04 Registration and ownership
- The registration record withholds contact details for the operator.Registration and ownership
rule:KF_WHOIS_HIDDEN - The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 25% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of crackedclients.com.
- The request stayed on crackedclients.com. It was not redirected to another domain. Clear
- Registration is published under Cloudflare, Inc.. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-10-12. Noted
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Cloudflare, Inc. |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3031::6815:46e0 |
| Name servers | KARSYN.NS.CLOUDFLARE.COM, THOMAS.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-10 |
| Domain age | 0.00 years (continuous registration) |
| Domain expiry | 2027-10-12 |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about crackedclients.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.