Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
crypto-1hz.netlify.app shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 2 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 | Noted |
| Hosted by | AMAZON-02Server in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
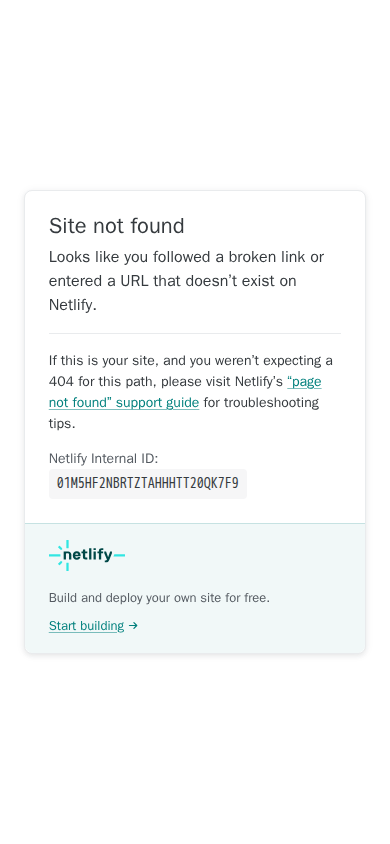
The site is a subdomain on a free application-hosting platform, with a name that suggests a cryptocurrency theme. When the page was captured, the homepage returned a "Site not found" placeholder with only a few hundred characters of text and no identifiable brand, product description, or operator. Its apparent purpose cannot be established from the visible content. The behavior observed during page loads is not consistent with an empty placeholder.
Scam/Impersonation Risk
This is a high-risk assessment, and it rests on contradictory signals. An external reputation source currently lists the site as flagged. Aggregated scanning engines returned one malicious and two suspicious detections against the domain itself, so this is a confirmed blacklist hit rather than a soft reputational hint. Behavioral testing adds to the concern. Across all three automated visits the homepage contained concealed form elements, and three password-entry fields were present on a page that shows no visible login or product. The page also made heavy external network traffic, including numerous outbound data submissions. All of it went to recognized third-party destinations. The page structure also changed dramatically after interaction, with thousands of DOM mutations. That pattern is typical of content injected or swapped after load. The visible "not found" shell therefore does not match what the page actually does, and a placeholder that carries hidden credential-capable forms is a recognized staging pattern for credential-harvesting pages. Two abuse reports exist against one of the shared edge addresses. They apply to infrastructure used by many unrelated tenants and are discounted, so they add no weight against this site. No conflicting legal entities or brand-impersonation claims were observed, because the page publishes no identity content at all.
- Homepage: the captured page presents a "Site not found" placeholder with minimal text and no brand, product, or contact details.
- Homepage behavior: concealed forms were detected in every automated run, and three password fields were present with no visible login interface.
- Homepage behavior: the page showed very heavy post-load DOM change and a near-total share of external network activity.
- External reputation: the domain carries a current blacklist listing and detections from multiple scanning engines.
Regulatory Verification Notes
The site publishes no legal, terms, privacy, about, or licensing pages, and no operator name, registration number, or regulator reference. Ownership and governance are opaque, and the real-world operator has not been independently connected to any person or company. No third-party broker or regulatory-database match exists for the name. Any financial or crypto-asset service offered through this domain would therefore have no verifiable authorization behind it. The site's transport encryption is valid, but a certificate demonstrates only that the connection is encrypted and that the hosting platform's account holder obtained one. It says nothing about the legitimacy of the content served.
- Homepage: no company name, licence, registration number, or regulator reference is published.
- Site structure: no terms, privacy, or about pages were captured.
- Hosting: served from AS16509 (AMAZON-02, Amazon.com, Inc., US).
- Transport encryption: the TLS certificate was issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 at OV validation level, with the subject organization shown as Netlify, Inc, valid to 2027-03-19. It identifies the hosting platform, not the site's operator.
What to Verify Next
Any claim that this domain belongs to a named exchange, wallet, or investment service should be checked against that organization's officially published domain, reached through an independent route rather than through any link, message, or advertisement that led here. Authorization should be confirmed directly in the relevant financial regulator's public register. If the domain was supplied in a message, social post, or advertisement, the sender's identity and channel should be confirmed offline, and the source should be treated as suspect until then. Anyone who has already entered a password or recovery phrase on this domain should rotate those credentials immediately and review the affected accounts. The hosting platform's abuse channel and the relevant security teams should be notified.
- Homepage: the page cannot tell a visitor who operates it, so identity must be established outside the site.
- Homepage forms: the concealed password-capable fields mean that any credentials entered on the domain are exposed.
- External reputation: the current blacklist listing indicates that other parties may already treat the domain as hostile.
Summary Verdict
The domain presents a clearly elevated risk posture. Convergent threat listings and concealed credential-capable behavior outweigh the technical hygiene signals that are present. The operator is unidentified, so no claim of legitimacy can be supported. The safe interpretation is that the site is a probable staging or phishing asset until proven otherwise.
Infrastructure Integrity
The site is served through Amazon-operated CDN/WAF infrastructure. All four observed addresses are edge nodes, and no origin server was observable. This is a mitigating factor only. It shows the hosting is professionally operated and the connection is encrypted, but it cannot offset the external threat detections. Edge-only visibility also prevents independent verification of where content originates and can mask rapid content swaps.
Closing Assessment
The site should be limited to passive viewing at most. No login, credentials, recovery phrase, wallet connection, payment, or personal data should be submitted, and nothing should be downloaded from it. Organizations should consider blocking the domain pending a clean re-assessment.
Written analysis generated 2026-10-22 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Behaviour in a sandbox
- The page contained a form a visitor cannot see.Behaviour in a sandbox
rule:BEHAV_HIDDEN_FORMS - Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page replaced a large part of its own content after loading.Behaviour in a sandbox
rule:BEHAV_DOM_CHANGE_HIGH - The page rewrote itself after it was interacted with, so what a visitor first sees is not what they end up on.Behaviour in a sandbox
rule:BEHAV_DOM_DIFF_AFTER_INTERACTION
Signals weighed against the site
- AbuseIPDB: 2 reports on hosting IP 2a05:d014:58f:6200::259 (Amazon Data Services Ireland Ltd, Content Delivery Network), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of crypto-1hz.netlify.app.
- The request stayed on crypto-1hz.netlify.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 2a05:d014:58f:6200::259 |
| Name servers | Not available |
| CDN / edge network | Detected (aws) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
| SSL expiry | 2027-03-19 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 1 flagged | AbuseIPDB: 0% confidence, 2 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about crypto-1hz.netlify.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.