Verdict
The site blocked our scan, so nothing was confirmed either way. Treat it as unknown and verify who runs it another way.
crypto-vgc.netlify.app blocked our automated scan and could not be verified.
- Needs Review: The site blocked or cut short the capture, so no verdict was reached.
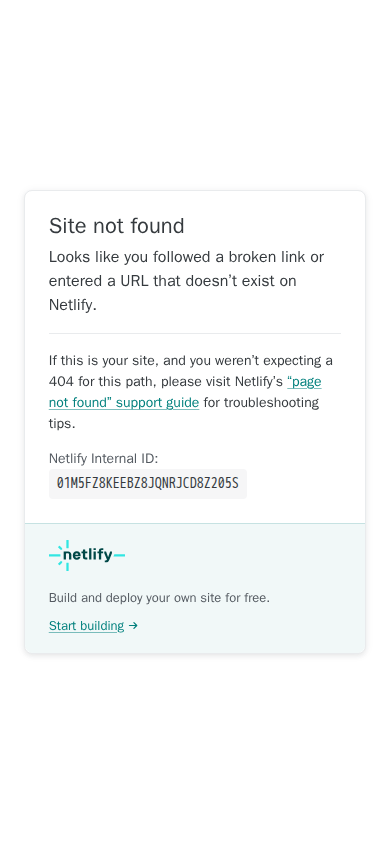
| How the site describes itself | The page is a Netlify 'Site not found' 404 error response, indicating the requested path does not exist on the Netlify-hosted site. It contains no service description, forms, links, or other site content. |
|---|
Evidence status and limitations
Evidence completeness: IncompleteThis says whether every check on the site was recorded as finished. The site blocked or cut short our capture, so the result needs review.
- Capture was incomplete or blocked; this result requires review.
- The real-world operator identity was not independently verified.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 2 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | Not availableNo registration record was returned | Noted |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 | Noted |
The page as captured
Key findings
- The site blocked automated access, so TrustSniffer could not collect enough evidence to assign a score.
Full analysis
Overview
The website is a subdomain on Netlify's shared hosting platform, and its homepage currently serves only the platform's generic "Site not found" error page. The page says the visitor followed a broken link or entered a URL that does not exist on Netlify, and it invites the site owner to consult a troubleshooting guide. It shows no products, services, branding, contact details, or forms, so its purpose and business model cannot be determined from what is publicly served. Only the hostname hints at a cryptocurrency theme.
Scam/Impersonation Risk
No contradictory signals were observed, and the contradiction severity is soft. There are no reputation-list or phishing detections, no conflicting legal identities, and no confirmed impersonation. Major threat-intelligence sources report no malicious or suspicious detections for the site. The only negative reputational signal is a small number of abuse reports (two). These were filed against the IP address 2a05:d014:58f:6200::259, which belongs to Amazon Data Services Ireland Ltd (amazon.com) and is classed as a Content Delivery Network address. The address is not whitelisted. The reports are attributed to shared infrastructure, meaning they apply to a shared provider IP and not to this site specifically. The signal also carries a confidence score of 0. For both reasons it is discounted, but it is still disclosed here. Two behavioral anomalies remain unexplained: the automated browser sessions recorded hidden forms containing password fields, and the page showed unusually heavy DOM activity for a static error page. A content-analysis check also flagged resemblance to the hosting platform's own name, which is consistent with a platform-served error page. The capture shows no sign of credential harvesting, wallet-connection prompts, clipboard manipulation, or cloaking. These items are unresolved observations, not evidence of fraud. They could change in meaning if real content is later deployed under this hostname.
- Homepage: the only content is the platform's generic 404 notice. There are no forms, links, or calls to action visible to a visitor.
- Homepage behavior: repeated automated sessions recorded hidden forms with password fields and heavy DOM mutation, and no wallet-connect, drainer, or clipboard activity.
- Reputation: two abuse reports exist only against a shared provider CDN address (Amazon Data Services Ireland Ltd). They are attributed to shared infrastructure, carry a confidence score of 0, and are discounted, so they are not treated as a finding against this site.
Regulatory Verification Notes
The site discloses no operator identity, legal entity, licence, registration number, or governance information. On-page disclosure is unclear, and governance and ownership remain opaque. The only page served is a hosting error page with no legal, terms, privacy, or about content. Nothing on it indicates a regulated activity, and no third-party broker or regulatory listing matched the site. Identity verification status is unverified (score 30, confidence 0.5), with no supporting signals. Real-world operator identity therefore remains unverified. Because the site publishes nothing, this is a gap in available information and not a contradiction. The valid, organization-validated transport certificate is issued to the hosting platform. This is consistent with the platform controlling the endpoint. It does not link the site to any business or individual.
- Homepage: no company name, licence, jurisdiction, or registration details are published, and no legal or policy pages exist.
- Transport encryption: the TLS certificate was issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 with OV validation, names Netlify, Inc as the subject organization, and is valid to 2027-03-19.
- Hosting: the site is served from AS16509 (AMAZON-02 - Amazon.com, Inc., US).
What to Verify Next
The first step is to determine whether the hostname is intended to carry a live service at all, since the current page may reflect an unpublished, removed, or misconfigured deployment. If real content appears, the operator's legal entity and any claimed licence should be confirmed against the relevant registry or regulator, and the claimed regulatory status should be checked independently. Confirm the official contact and support channels through an independent route, such as the organization's well-known primary website or a directly known representative, not through links found on this host. If the hostname is promoted as part of any crypto-related offering, the promoting party should be asked to confirm in writing that this is an official property.
- Homepage: the current absence of any content means no claims can be checked against a registry yet.
- Hostname: the name suggests a crypto-related project, but nothing on the page supports or links it to any named organization.
- Behavioral capture: hidden password-bearing forms were recorded, so a re-assessment is warranted if real content is published.
Summary Verdict
The evidence supports a measured, needs-review posture. No indication of malicious intent has been found, but nothing available allows trust to be established either. The site appears to be an empty placeholder with an unverified operator. The two discounted abuse reports on a shared provider address and the unexplained behavioral anomalies keep its classification provisional until it presents verifiable content and identity.
Infrastructure Integrity
The site resolves to provider edge nodes in the United States on the Amazon cloud network, behind the hosting platform's CDN/WAF layer. All observed addresses are edge servers, and the origin server is not exposed. This is a protective, mitigating factor for availability and resilience. It is not evidence of legitimacy, because the same shared infrastructure serves any customer who deploys a site. That sharing is also why the abuse reports on the shared CDN address are discounted and not attributed to this site. Shared platform hosting also means content under this hostname can be changed or replaced quickly, which supports re-checking the site later.
Closing Assessment
Browsing the current error page carries no apparent exposure. Account logins, credential entry, wallet connections, and payments should wait until the operator's identity has been independently confirmed and the site presents real, verifiable content.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by behaviour in a sandbox and page content.
01 Behaviour in a sandbox
- The page contained a form a visitor cannot see.Behaviour in a sandbox
rule:BEHAV_HIDDEN_FORMS - The page contained a form a visitor cannot see in more than one sandbox session.Behaviour in a sandbox
rule:BEHAV_HIDDEN_FORMS_REPEAT - The page replaced a large part of its own content during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_CHANGE_HIGH - The page rewrote itself after it was interacted with, so what a visitor first sees is not what they end up on.Behaviour in a sandbox
rule:BEHAV_DOM_DIFF_AFTER_INTERACTION - The structure of the page changed sharply during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE
02 Page content
- The page runs on a free netlify.app address instead of a domain of its own, a setup common to short-lived phishing and claim pages.Page content
rule:PAGE_BRAND_SUSPECTED
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 2 reports on hosting IP 2a05:d014:58f:6200::259 (AMAZON-02), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of crypto-vgc.netlify.app.
- The request stayed on crypto-vgc.netlify.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc. |
| Network registered in | US |
| Server IP | 2a05:d014:58f:6200::259 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (aws) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
| SSL expiry | 2027-03-19 |
| First seen (web archive) | Not available (the web archive has no record of this address; a site on netlify.app has no registration of its own) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 2 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about crypto-vgc.netlify.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.