Verdict
Our checks found nothing pointing to fraud. Ordinary care still applies when you pay or sign in.
currymessi.com appears legitimate.
- Not Scam: No check found a pattern TrustSniffer associates with fraud. That is a reading of the evidence, not a guarantee.
- Low Risk: The checks found few risk signals.
| How the site describes itself | Polish-language ecommerce storefront 'currymessi' showing product listings, discounts, categories, shipping and refund policies, contact email ([email protected]) and live chat hours. Appears to be a retail shop page rather than financial or phishing site. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-10-05 and re-scored on 2026-11-04. The certificate, the registration age and the page content describe the site as it was on 2026-10-05.
- The real-world operator identity was not independently verified.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 90/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 121 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 3.1 years oldRegistered 2023-09-09 | Clear |
| Web archive | Archived since 202442 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
Key findings
- Automated classification: Not Scam, Low Risk.
- Domain age: 3 to 10 years at capture (registered 2023-09-09).
- Public web-archive history exists since 2024.
- VirusTotal and Google Safe Browsing had no flags for this domain; its hosting IP carries AbuseIPDB reports below the confidence level TrustSniffer treats as a flag.
Full analysis
Overview
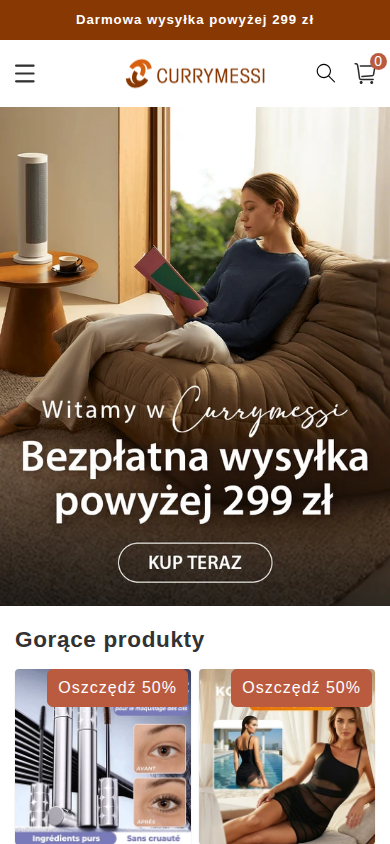
Currymessi is a Polish-language online retail storefront that presents a broad general-merchandise catalogue to visitors. Its categories cover car accessories, home and kitchen goods, electronics, tools and gadgets, clothing and swimwear, and health and beauty. The homepage advertises free shipping on larger baskets, a "hot sale" section, order tracking, a customer login and cart, and promotional bundles. The apparent business model is direct-to-consumer sales of physical goods through on-site checkout, funded by product margins and discount-led promotions.
Scam/Impersonation Risk
No contradictions were observed. There is no sign of phishing, brand impersonation, conflicting legal identities, or a confirmed hard reputation flag from any source. The storefront does not imitate a financial institution or a known retailer, and it has no wallet-connection, cryptocurrency or investment features. The sandbox behaved like an ordinary shop. Every run completed successfully, and there was no cloaking, clipboard manipulation, wallet-drainer behaviour, or password submission to external destinations. Several observations were nonetheless noted and set against the high-trust classification. The shop's network address (23.227.38.65) carries 121 abuse reports. This address belongs to Shopify, Inc., a shared content-delivery provider that serves many unrelated merchants. The provider is whitelisted and the confidence score is 0. The reports are therefore attributed to shared infrastructure and discounted, because they are not specific to this site. They remain a visible signal, but they do not count against it. One threat-intelligence source returned a single low-confidence "suspicious" flag with no corroboration. This is a soft third-party warning and reputation note, not a confirmed finding, and the major reputation sources were otherwise clean. The sandbox also recorded a hidden form, heavy page rebuilding after interaction, and requests to third-party hosts outside the expected allow-list. These are consistent with newsletter, search, and storefront widgets. Their purpose was not independently attributed, so they are noted as unexplained rather than as findings of misconduct. The pricing pattern deserves scrutiny. Nearly every featured item is shown at "Save 50%" against an inflated regular price. Examples are a "Buy 1, get 1 free" 24-hour mascara from the low 60s zł against about 120 zł, a mesh one-piece swimsuit at 109.99 zł against 219.99 zł, and tablets for "restoring shrunken clothes". Uniform half-price markdowns are a common marketing device on low-cost general-merchandise shops. They make the reference price impossible to verify, but they are not evidence of fraud.
- Homepage: product cards show uniform 50% reductions against struck-through regular prices, a buy-one-get-one-free mascara promotion, and a free-shipping threshold of 299 zł.
- Homepage: three forms are present (search, login/sign-in, and email subscribe/contact). None is flagged as sensitive or as posting to an untrusted destination.
- Sandbox behaviour: three of three runs succeeded, with no cloaking, wallet interaction, or fingerprinting detected. One hidden form and a number of third-party requests were observed, without attribution to any malicious purpose.
- Network address: 121 abuse reports on 23.227.38.65 (Shopify, Inc., content delivery network). The address is whitelisted with a confidence score of 0. The reports are attributed to shared infrastructure and discounted.
- Domain provenance: registered September 2023 (~3 years old). Web-archive history holds 42 snapshots spanning 2024–2026 (3 years tracked), with continuous activity and no content repurposing.
Regulatory Verification Notes
The storefront is not a financial or regulated service, and no licence is claimed. Licensing is therefore not a relevant test, and its absence is not a negative signal. The relevant matter is merchant disclosure. The captured homepage content shows shipping and refund policy references, contact details, and live-chat hours, but does not surface a registered legal entity name, company registration number, or business address. This is a disclosure gap in the captured content, not evidence of wrongdoing, and the real-world operator remains unverified. Independent identity verification is unverified, with a low score (30) and low confidence (0.25). No identity signals were found that independently connect the site to a real-world brand or person. Domain registration is held through a privacy service. That is an administrative convention and not treated as a security concern. No third-party broker or regulatory-database match exists for this name. Absence of a match is neutral, not a verdict in either direction.
- Homepage: shipping, refund, and contact references and live-chat hours are displayed, but no merchant legal entity, registration number, or physical address appears in the captured content.
- Domain registration: created 9 September 2023 (~3.07 years old) via the registrar NameSilo, LLC, with registrant details behind a privacy service; registration runs to September 2027.
- Transport encryption: a valid TLS certificate issued by YE2 (DV level), valid to 2026-11-11.
- Hosting: served from AS13335 (Cloudflare, Inc.).
What to Verify Next
Before sharing credentials or paying, a prospective customer should establish who is actually selling. This means finding the merchant's legal name and a physical or registered business address on the shipping, refund, or terms pages, and checking them independently. Pricing should be sanity-checked by comparing comparable items elsewhere, since the permanent half-price reductions cannot be benchmarked on the site itself. The refund policy should be read for who bears return shipping, the timeframe, and the process. The official support channels should be confirmed independently of the storefront. A small first order paid by a method with chargeback protection would test fulfilment before any larger commitment.
- Homepage: the order-tracking page and the shipping and refund policy links are the first places to check for a named merchant and a return address.
- Homepage: the featured items carry ratings of 4.8 with no visible source for the reviews, so review authenticity cannot be assessed from the page.
- Account area: login and subscribe forms exist, so stored credentials or an email address would be shared with an operator whose identity has not been independently established.
Summary Verdict
Available evidence is consistent with a long-running small retail storefront that behaves like an ordinary shop. The operator's identity is unverified, so the evidence supports this reading but does not prove legitimacy. A multi-year domain with continuous recent activity, a valid certificate, ordinary shop behaviour, and no contradictory signals converge to support a high-trust classification. The reputation picture is otherwise clean apart from two discounted or soft notes: abuse reports attributed to shared Shopify infrastructure, and one uncorroborated low-confidence "suspicious" flag from a single source. That classification concerns the site's observable conduct. It does not confirm the identity of the real-world operator.
Infrastructure Integrity
The site is served through Cloudflare's CDN and WAF network. The single observed address sits on Cloudflare's network under a US-registered provider, and the origin server was not exposed. This is a protective, mitigating arrangement that reduces direct exposure and is typical of well-run commercial sites. It does not by itself establish legitimacy. An unconfirmed heuristic noted some fragmentation in the infrastructure footprint. It is weighed lightly against the otherwise healthy configuration.
Closing Assessment
Browsing the catalogue is appropriate. Before creating an account or paying, a prospective customer should complete the independent merchant-identity, return-policy, and payment-protection checks described above, and should use a card or payment method that offers dispute rights.
Written analysis generated 2026-11-04 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by behaviour in a sandbox, registration and ownership and page content.
01 Behaviour in a sandbox
- The page contained a form a visitor cannot see.Behaviour in a sandbox
rule:BEHAV_HIDDEN_FORMS - The structure of the page changed sharply during the sandbox session.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE - The page rewrote itself after it was interacted with, so what a visitor first sees is not what they end up on.Behaviour in a sandbox
rule:BEHAV_DOM_DIFF_AFTER_INTERACTION
02 Registration and ownership
- The registration record withholds contact details for the operator.Registration and ownership
rule:KF_WHOIS_HIDDEN
03 Page content
- The page asks visitors for sensitive information.Page content
rule:PAGE_FORM_SENSITIVE
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 121 reports on hosting IP 23.227.38.65 (CLOUDFLARENET), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of currymessi.com.
- The request stayed on currymessi.com. It was not redirected to another domain. Clear
- Registered through NameSilo, LLC. Noted
- DNS for this domain is served by dnsowl.com, across 3 name servers. Noted
- The domain is registered until 2027-09-09. Noted
- The earliest public archive of this site is from 2024-05-10. Clear
- It is hosted on CLOUDFLARENET, a network registered in CA; the provider, Cloudflare, Inc., lists its country as US. Noted
Domain intelligence
| Registrar | NameSilo, LLC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. (the provider lists its country as US) |
| Network registered in | CA |
| Server IP | 23.227.38.65 (a CDN edge address; the server behind it was not observed) |
| Name servers | ns1.dnsowl.com, ns2.dnsowl.com, ns3.dnsowl.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 1 |
| Edge IP addresses | 1 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2026-11-11 |
| Domain age | 3.07 years (registered 2023-09-09) |
| Domain expiry | 2027-09-09 |
| Archive first seen | 2024-05-10 (2.4 years before capture) |
| Archive snapshots | 42 |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 121 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about currymessi.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.