Verdict
Several risk patterns were present. Do not send money or personal details until you have verified this business another way.
cyberleek.lol is low-trust and potentially risky.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 31% confidenceAbuseIPDB, 1697 reports; shared hosting inflates reports | Clear |
| Domain age | 2 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20261 snapshot | Clear |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
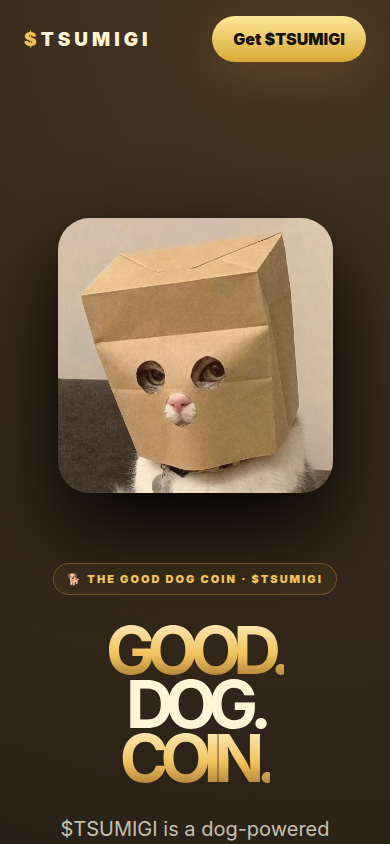
This website is a single-page promotional site titled "$TSUMIGI — Good Dog. Good Coin.", which presents a dog-themed crypto token under a meme-coin branding style. Its apparent purpose is to promote the token to visitors, most likely to drive token acquisition or community sign-up. It sits on a very recently registered domain with a novelty top-level domain.
Scam/Impersonation Risk
Contradictory signals are present. The domain is blacklisted by external threat-reputation sources: one source flags it as malicious and two more as suspicious. Page capture, archive and reputation checks also show indicators consistent with known phishing association. Together these push the assessment into a clearly cautionary, security-forward posture. The domain was registered only a couple of months ago and has almost no independent history, which is the profile typically seen in short-lived token promotions and in infrastructure built for rapid monetisation. The page is also themed around a speculative token, a category where fake launches and rug-pull schemes are common. Separately, the hosting address shows a large volume of abuse reports. These apply to a shared hosting address, so they cannot be pinned on this site alone, but they add to the unfavourable reputational picture. In mitigation, automated browsing of the homepage showed no external data posts, no wallet-drainer behaviour, no clipboard manipulation, no hidden forms and no cloaking. No conflicting legal identities and no brand impersonation were observed. The concern rests on the blacklist and the domain's immaturity, not on observed malicious page behaviour. Evidence:
- Homepage: external reputation sources currently list the domain (one malicious and two suspicious detections), and the site is treated as a known-phishing association.
- Domain registration: registered in August 2026 (about 0.19 years old, roughly 68 days), through PDR Ltd. d/b/a PublicDomainRegistry.com, expiring August 2027.
- Web archive: a single snapshot, captured 2026-08-21, so no meaningful historical continuity exists.
- Hosting address: 1,697 abuse reports on the shared address, assessed as shared-infrastructure noise, with a moderate confidence rating.
Regulatory Verification Notes
The homepage is the only page analysed. It shows no verifiable corporate entity, licensing or registration detail, and no regulator reference. For a token-promotion site, this means no basis exists for assuming any investor-protection, securities or virtual-asset service regime applies. No third-party broker or regulatory-database match was found, so no external signal of regulatory standing exists in either direction. This is a verification gap and not, by itself, evidence of wrongdoing, but combined with the blacklist it leaves nothing to offset the reputational risk. The site's technical hygiene is basic: it has a valid certificate, but certificate validation is domain-only and confirms nothing about the operator. Evidence:
- Hosting infrastructure: served from AS16509 (AMAZON-02 - Amazon.com, Inc., US).
- Transport encryption: TLS certificate issued by YE2 (DV, domain validation only), valid to 2027-01-15.
- Digital-asset directories: the domain does not appear in the DeFi directory checked, so no TVL or protocol recognition exists.
- Homepage: no company name, licence number or regulator reference is published.
What to Verify Next
Any interaction with the token should wait until the operator is independently identified. The project's claimed team, token contract address and any audit reports should be checked against sources outside this site, such as a block explorer and the official channels of established token-tracking platforms. Any claimed licence or registration should be confirmed directly with the relevant registry, using the registry's own search and not links supplied on the site. Official contact and community channels should be confirmed through an independent route. The domain's blacklist status should also be rechecked after a period, since listings can change as the site is cleaned up or as further reports arrive. Evidence:
- Homepage: the token branding gives no project documentation, team detail or contract reference to check against.
- Domain registration: the roughly two-month-old registration means no long track record exists to lean on.
- Reputation sources: the current external listings are the key item to recheck.
Summary Verdict
The site is assessed at an elevated risk level and in the low-trust band. A confirmed external blacklist and a very young, thinly documented domain outweigh its clean page behaviour and valid transport encryption. The available evidence does not support treating it as a legitimate or established operation, and the real-world operator remains unidentified.
Infrastructure Integrity
The site is delivered through an AWS CDN/WAF layer, and every observed address is an edge address, so the origin server was not visible. This protection is a mitigating factor only. It cannot offset the external threat detections, and edge-only visibility makes it harder to verify the true host and easier to swap content quickly. A heuristic flagged the domain's youth and sparse subdomain footprint, but that is unconfirmed and carries little weight on its own.
Closing Assessment
Passive viewing of the page is the only use consistent with the evidence. Logging in, entering credentials, connecting a wallet or making any payment or token purchase should be avoided until the operator is independently identified and the external listings are cleared.
Written analysis generated 2026-10-26 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, hosting and network, history in the web archive.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D - The domain is young and has almost nothing else set up around it.Hosting and network
rule:DNS_SPARSE_YOUNG_DOMAIN
03 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Signals weighed against the site
- AbuseIPDB: 1697 reports on hosting IP 35.157.26.135 (A100 ROW GmbH, Data Center/Web Hosting/Transit), 31% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of cyberleek.lol.
- The request stayed on cyberleek.lol. It was not redirected to another domain. Clear
- Registration is published under PDR Ltd. d/b/a PublicDomainRegistry.com. Clear
- DNS for this domain is served by nsone.net, across 4 name servers. Noted
- The registration is paid up to 2027-08-18. Noted
- The earliest public archive of this site is from 2026-08-21. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | PDR Ltd. d/b/a PublicDomainRegistry.com |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 35.157.26.135 |
| Name servers | DNS1.P05.NSONE.NET, DNS2.P05.NSONE.NET, DNS3.P05.NSONE.NET, DNS4.P05.NSONE.NET |
| CDN / edge network | Detected (aws) |
| Resolved IP addresses | 2 |
| Edge IP addresses | 2 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2027-01-15 |
| Domain age | 0.19 years (continuous registration) |
| Domain expiry | 2027-08-18 |
| Archive first seen | 2026-08-21 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 1 flagged | AbuseIPDB: 31% confidence, 1697 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about cyberleek.lol at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.