Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
daatfi.xyz shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: The governance checks raised a concern: a threat-intelligence listing limits the score; the domain's registration record withholds the owner's details. The findings below give the detail.
| How the site describes itself | DaatFI is a self-described experimental, testnet-only decentralized lending dApp on Arc Testnet (Chain ID 5042002). It lets borrowers request USDC loans against RWA or crypto collateral and lets lenders or pool depositors fund them for fixed interest of up to 5% per month. The page explicitly states that no real funds are used, but it promotes lender yield, lists unverified legal and jurisdictional claims, and contains an internal inconsistency between a 7% fixed rate and the 5%/month cap. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The real-world operator identity was not independently verified.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 5/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | Threat-listing ceilingA threat-intelligence feed TrustSniffer monitors listed a file on this site as malicious when the evidence was captured, and that listing caps the score. | Risk |
|---|---|---|
| Malware engines | None flagged itVirusTotal | Clear |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 6 months oldRegistered 2026-04-21 | Watch |
| Web archive | Archived since 20263 snapshots; the archive has almost no record of this site, which counted against it | Watch |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-04-21).
- Public web-archive history exists since 2026.
- No flags from the reputation services TrustSniffer consulted when the evidence was captured.
Full analysis
Overview
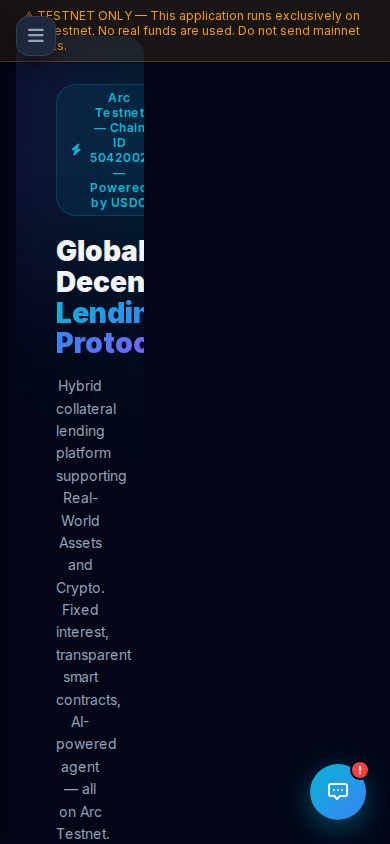
DaatFI is a decentralized lending web application that presents itself as an experimental prototype running only on a test network (Arc Testnet, Chain ID 5042002). It invites visitors to connect a crypto wallet and request USDC loans against real-world or crypto collateral. It also invites them to lend or deposit into a liquidity pool to earn fixed interest of up to 5% per month. The platform charges a 2% fee on loan principal. The apparent business model is peer-to-peer and pooled yield lending, with a loan marketplace, NFT-collateral loans, token swap and bridge functions, and an "AI agent" that executes payment commands.
Scam/Impersonation Risk
Confirmed contradictions are present, and they are serious. A threat-intelligence feed currently lists this site as distributing phishing. The site is the actor in that listing, not a compromised victim, and the listing is decisive for the assessment. A separate external reputation source also flags the domain, so the site is blacklisted by more than one independent signal. The domain was registered only about half a year ago and has almost no archived history. Newly created, thinly documented crypto-lending domains are a common profile for credential and wallet-harvesting operations. The homepage's "testnet only, no real funds" banner does not offset this. A testnet label costs nothing to display, and the listing shows the domain is being treated as a live phishing vector. The page's own content adds to the concern. It advertises a headline "Max Interest 5% Fixed / month", which compounds to a very high annualised return. It also states a fixed 7% rate in the Loan Request panel, which contradicts the 5% monthly cap published elsewhere. That mismatch means the site's own numbers cannot be relied on. The site claims it can enforce real-world collateral such as cars, houses and jewelry "across any jurisdiction", backed by a notarized document hash on IPFS. It shows no legal entity or enforcement mechanism that could back this up. The interaction surface is also broader than a "testnet demo" needs. The site prompts for wallet connection and on-chain transaction signing, and it carries a personal-information form and a settings page that accepts API keys. These are the inputs a phishing operation would want.
- Homepage: a testnet-only warning banner sits beside a "Max Interest 5% Fixed / month" tile, "Lend & Earn" prompts, and a Loan Request panel quoting a fixed 7% rate that conflicts with the 5%/month cap.
- Homepage forms: five forms were detected, covering a loan-application wizard, personal identity information, collateral token entry, pool deposit/withdraw, and API-key entry in settings. The site also issues wallet-connection and transaction-signing prompts.
- Domain registered 2026-04-21 (~0.5 years old), so the domain has existed for only a few months.
- Web archive holds only 3 snapshots, spanning 2026-04-27 to 2026-04-28 (1 year tracked), so there is no meaningful operating history.
Regulatory Verification Notes
The site discloses no licensing, regulatory registration, or operating legal entity, and no physical contact address. It nonetheless markets itself as a global lending protocol, offers lending against real-world assets, and publishes legal and jurisdictional statements that cannot be checked against any registry. For a platform that accepts personal data and promotes yield, this is a material gap in on-site disclosure. In isolation it would be a verification gap rather than proof of wrongdoing. Here it compounds the confirmed threat listing and does not stand alone. No third-party broker or regulator database entry matched this site, so there is no outside reputational record to cite in its favor or against it. The site's own claim that it is "non-custodial" and testnet-only is self-asserted and unaudited, and the site references no security audit.
- Homepage and navigation: no licence, registration number, legal entity name, or terms-of-service identity are shown.
- Homepage: real-world collateral and "any jurisdiction" enforcement are claimed without a named entity, notary, or legal framework.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: TLS certificate issued by WE1 (DV level), valid to 2027-01-14. A basic domain-validated certificate confirms only that the domain is encrypted, not who operates it.
What to Verify Next
No wallet connection, signature, deposit, or personal data entry should take place on this site. Verification therefore applies only to anyone who already interacted with it. A user who connected a wallet or signed anything should review and revoke the token approvals the site requested, using the approval-management feature of a reputable blockchain explorer. A user who typed API keys, identity details, or collateral information into the site's forms should treat that data as exposed. Such a user should rotate the keys and monitor the related accounts. Anyone considering the project independently should look for a named legal entity, a published security audit, and a verifiable code repository. They should find these through channels they can confirm are official and not through links on this site. Confirm official support and contact channels through an independent route before any further engagement.
- Homepage: the only external links point to a block explorer, an RPC endpoint, and a third-party site. No audit report or source-code link is offered.
- Homepage settings area: a form accepting API keys indicates a credential-exposure path.
- Homepage: social links (X, Telegram, email) appear as navigation items only and lead to no verifiable organizational profile.
Summary Verdict
The overall posture is high risk. A current threat-intelligence listing identifies this site as an active phishing source, and that finding outweighs everything favorable. The site's polished interface, working application behaviour, and stable technical presentation show effort, but they do not establish legitimacy. Its operator is unidentified, and the identity of the real-world party behind it remains unverified. The testnet framing does not reduce the risk, because the confirmed external findings and the data-collection and signing features point the same way.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and WAF. All observed addresses are edge servers, and the origin server is not observable. This is a mitigating factor only. It shows commodity, professionally managed protection, and it also prevents independent verification of where the content is actually hosted. That can mask rapid content swaps. The shared infrastructure is not itself abusive, and it does not offset the external threat findings.
Closing Assessment
The site should be treated as unsafe for any login, wallet connection, credential entry, or financial interaction, and at most viewed passively. Anyone who has already interacted with it should revoke wallet approvals and rotate any keys or credentials they entered.
Written analysis generated 2026-11-04 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by governance, external reputation, page content and history in the web archive.
01 Governance
- A threat-intelligence feed TrustSniffer monitors listed a file on this site as malicious when the evidence was captured, and that listing caps the score.Governance
rule:gov_active_threat_listing
02 External reputation
- Three or more VirusTotal engines, or two including a leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_HIGH
03 Page content
- The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of daatfi.xyz.
- The request stayed on daatfi.xyz. It was not redirected to another domain. Clear
- Registered through DYNADOT LLC. Noted
- DNS for this domain is served by ns.cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-04-21. Noted
- The earliest public archive of this site is from 2026-04-27. Watch
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | DYNADOT LLC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3031::6815:5292 (a CDN edge address; the server behind it was not observed) |
| Name servers | aiden.ns.cloudflare.com, clarissa.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-14 |
| Domain age | 197 days (registered 2026-04-21) |
| Domain expiry | 2027-04-21 |
| Archive first seen | 2026-04-27 (191 days before capture) |
| Archive snapshots | 3 |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about daatfi.xyz at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.