Verdict
Several risk patterns were present. Do not send money or personal details until you have verified this business another way.
dapps-sync.pages.dev is low-trust and potentially risky.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 3 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | CLOUDFLARENETServer in US | Noted |
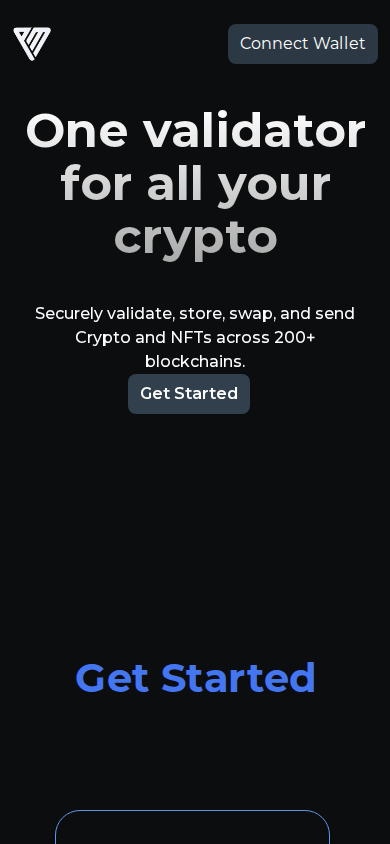
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
This website is a single-page site served from a free subdomain of a public web-hosting platform. The page title is "Mainnet Chains Validator", which presents it as a blockchain network or validator utility. The homepage carries a modest amount of text and renders its content dynamically. No named operator, product catalogue, or commercial offer could be established from the supplied evidence, so its business purpose is unclear. The pairing of blockchain-validator branding with a disposable hosting subdomain matches a pattern commonly used to lure crypto users into connecting wallets or entering credentials.
Scam/Impersonation Risk
The dominant concern is external threat reputation. Several independent security engines currently classify the domain as malicious or suspicious, and it is blacklisted on a confirmed basis. Reputation intelligence also associates the domain with known phishing activity. The evidence does not show a conflicting legal identity or a named brand being imitated. The risk therefore rests on the blacklisting and the phishing association, not on a visible impersonation. The domain also closely resembles the hosting platform's own domain, a structural trait that suits deceptive use because the address appears to carry the platform's credibility. The page title and presentation suggest a crypto-validator or network-synchronisation theme. That theme is a common pretext for wallet-connection and credential-harvesting lures. Automated interaction did not trigger a wallet prompt, clipboard manipulation, hidden forms, external form posts, or cloaking, but this does not offset the active threat listings. The page also changed heavily after interaction, with a very large number of DOM mutations. This shows the content is assembled dynamically after load, which makes a static first look an unreliable guide to what a visitor would eventually see. Evidence:
- Homepage: the page title reads "Mainnet Chains Validator" and the site sits on a shared platform subdomain, so the operator cannot be told from the address.
- Reputation checks: multiple security engines flag the domain, and phishing-association intelligence is present. This is a confirmed blacklisting.
- Behavioural sandbox: three successful runs found no external requests, wallet-provider calls, clipboard writes or hidden forms. The homepage DOM mutated 2,363 times after interaction.
Regulatory Verification Notes
The evidence shows no regulatory standing for this site. No regulator or registry confirms any licence, registration or supervised status, and no third-party broker-reputation record matches the site. Independent identification of an operator was not possible, and no organisation or person has been connected to the site. Both ownership and governance information are opaque. That opacity is a verification limitation, not an identity contradiction. The threat listings, not the missing disclosures, drive the elevated assessment. For any site that invites investment, staking or asset-linked activity, the absence of a verifiable regulated entity removes the recourse that licensed providers would offer. Evidence:
- Homepage: no identifiable operator, legal entity, licence or registration reference could be established from the captured content.
- Transport encryption: the TLS certificate is issued by WE1 at domain-validation level and is valid to 2026-12-07. This confirms encrypted transport only, not operator identity.
- Hosting: the site is served from AS13335 (Cloudflare, Inc., US).
What to Verify Next
Any claim that this site is an official validator, network or protocol interface should be tested against the project's own channels, reached through an independently sourced address. The platform's abuse-reporting channel and the relevant security-intelligence portals should be checked for current takedown or suspension status. If the site presents itself as a financial or crypto service, its claimed regulator should be asked directly whether it holds a registration, using contact details taken from the regulator's own publications. Any official support or contact channels should be confirmed offline, not through links on the page. Evidence:
- Homepage: the validator branding implies an association with blockchain networks, but no named project or organisation is given for comparison.
- Threat listings: they are current, so the status of the listing should be rechecked before any decision to engage.
- Certificate: it expires in 43 days, which is a routine date to note when re-checking the site's state.
Summary Verdict
The overall posture is clearly cautionary. Confirmed adverse reputation findings are decisive, and nothing in the supplied evidence about content, behaviour or technical hygiene is enough to offset them. The site's real-world operator is not independently connected to any known entity, and apparent technical cleanliness cannot be read as legitimacy.
Infrastructure Integrity
The site is delivered through Cloudflare, a mainstream CDN and WAF provider on AS13335 in the United States. All observed addresses are edge servers, and the origin host was not observable. This is a mitigating factor only. It shows ordinary, competent hosting and a valid certificate, but it says nothing about the operator's honesty. Edge-only visibility also prevents independent verification of the hosting and can conceal rapid content swaps. Evidence:
- Hosting: four edge addresses across IPv4 and IPv6, all within AS13335 (Cloudflare, Inc., US).
- TLS: certificate issued by WE1 (DV), valid to 2026-12-07.
Closing Assessment
The site should be treated as read-only at most, and ideally not visited at all. Wallet connections, logins, credential entry, signing of transactions and any financial or asset-related interaction should be avoided entirely. Anyone who has already interacted with the site should review their wallet permissions and change any credentials they entered.
Written analysis generated 2026-10-25 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, registration and ownership.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Behaviour in a sandbox
- The structure of the page changed sharply while it was loading.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE
03 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of dapps-sync.pages.dev.
- The request stayed on dapps-sync.pages.dev. It was not redirected to another domain. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2efd |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-07 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 3 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about dapps-sync.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.