Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
debridge-secure.pages.dev shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 13 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 1.9 years oldRegistered history | Clear |
| Web archive | Archived since 20243 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
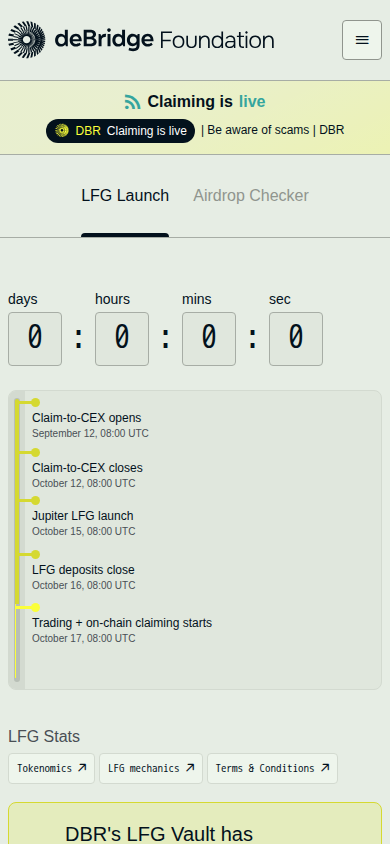
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: 1 to 3 years (registration continuity).
- Public web-archive history exists since 2024.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
The site is a single-page web application served from a free subdomain on a shared page-hosting platform. Its address pairs the name of a well-known cross-chain bridge protocol with the reassuring word "secure". The homepage is titled "DBR Checker" and carries a modest amount of text, which presents it as a utility-style checking tool. The capture offers no readable company description, product catalogue or stated business model, so the apparent purpose is to get visitors to interact with a "checker" under a bridge-protocol-style identity.
Scam/Impersonation Risk
This is the decisive area of concern. Hard contradictions are present: the domain is on a confirmed blacklist and is flagged as malicious by a large cluster of independent security engines, including two top-tier security vendors. That level of agreement is enough to trigger an automatic ceiling on the trust assessment, regardless of any positive technical hygiene. The historical record also associates the domain with a prior phishing report. The address itself combines a recognisable DeFi bridge brand name with a "secure" qualifier on a shared free-hosting subdomain. That pattern is typical of lookalike or "checker" pages built to lure users into wallet or credential interactions, and it is not how a legitimate protocol would publish its own services. No conflicting legal-entity names were found, and the sandbox did not observe wallet-connection prompts, clipboard tampering, hidden forms, cloaking or credential posts to external parties. These behavioural results do not offset the blacklist and the brand-lookalike naming. A page can be benign in a short sandbox session and still be switched to a malicious payload later. No contact email was published on the captured pages, so there is no contact-channel anomaly to report.
- The homepage is titled "DBR Checker", and the domain name pairs a bridge-protocol brand with "secure" on a shared free-hosting subdomain.
- Threat-intelligence results from multiple independent engines flag the domain as malicious, including two top-tier vendors, and the domain is on a confirmed blacklist.
- The domain is about 1.9 years old, with 3 archive snapshots spanning 2024-12-15 to 2024-12-19 (1 year tracked). The archive record also carries a prior phishing association.
- The sandbox ran 3 successful sessions and observed 74 external XHR/fetch requests, all to whitelisted destinations. It saw no wallet-connect, clipboard-hijack, hidden-form or cloaking behaviour.
Regulatory Verification Notes
The captured homepage discloses no legal entity, licence, registration number or governing jurisdiction, so no regulatory standing can be inferred for any financial or digital-asset function. Ownership is opaque, and nothing on the site independently connects it to the protocol brand its address evokes. The site is also absent from the decentralised-finance protocol directory that would be expected to list an authentic bridge deployment. No third-party broker or regulator record matched this site. Valid transport encryption is present, but a domain-validated certificate only proves control of the hostname. It says nothing about who operates the site or whether it is legitimate.
- The homepage and its captured text identify no company name, licence, registry number or jurisdiction.
- The site is not recognised in the DeFi protocol directory, and no broker-reputation record matched.
- The TLS certificate was issued by WE1 at DV (domain-validated) level and is valid to 2026-12-24.
- The site is served from AS13335 (Cloudflare, Inc., US).
What to Verify Next
Anyone who encounters this address should treat it as unverified and should not rely on it to reach the bridge protocol. Reach the genuine service only through its officially published domain, taken from an independent source such as the project's verified social accounts or a bookmark made earlier. The same independent route should be used to confirm the project's official support channels. Any prompt to connect a wallet, sign a transaction or "check" an address on this domain should be refused. Organisations that received this link in a message or advertisement should trace where it came from and report it to the hosting platform's abuse desk and to the protocol team.
- The "DBR Checker" homepage is the only observed interactive surface, and no on-site channel confirms who runs it.
- The domain was first captured in the archive on 2024-12-15, which postdates the brand it resembles by a wide margin. This is consistent with a recent registration trading on that name.
- The domain sits on a shared free-hosting platform, so the hosting platform's abuse reporting is the practical takedown route.
Summary Verdict
The overall posture is high-risk and clearly cautionary. A confirmed blacklist and broad malicious detections override the modest technical hygiene seen elsewhere. Identity is unverified, and the brand-lookalike naming raises the probability of deceptive intent. The evidence does not support treating this site as a legitimate destination for any sensitive activity.
Infrastructure Integrity
The site is delivered through a mainstream CDN and WAF platform, and all observed addresses are edge servers, so the true origin host cannot be seen. This is a mitigating factor only. The shared, ephemeral nature of such hosting means content can be replaced quickly without any visible change in the infrastructure, so it gives no assurance about who controls the content. The certificate is valid with a known issuer, and the hosting provider shows no abuse reports of its own. These are hygiene points that do not offset the reputation findings.
Closing Assessment
Do not log in, connect a wallet, sign transactions, enter seed phrases or credentials, or make any payment on this site. Do not download anything from it. If the address arrived through a link or message, discard it and navigate to the official service by an independently verified route.
Written analysis generated 2026-10-26 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by governance, external reputation, registration and ownership, behaviour in a sandbox.
01 Governance
- A threat feed lists this domain as malicious, and that caps the score whatever the other checks found.Governance
rule:GOV_CRITICAL_BLACKLIST
02 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
03 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
04 Behaviour in a sandbox
- The page made many background requests to other domains while it was open.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_XHR_HEAVY
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of debridge-secure.pages.dev.
- The request stayed on debridge-secure.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2024-12-15. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2c8f |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-24 |
| Domain age | 1.86 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2024-12-15 |
| Archive snapshots | 3 |
| Reputation | VirusTotal: 13 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about debridge-secure.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.