Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
donutbasefinder.com shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: The governance checks raised a concern: the kind of site it appears to be limits how high the score can go, because its operator could not be verified; a threat-intelligence listing limits the score; the domain's registration record withholds the owner's details. The findings below give the detail.
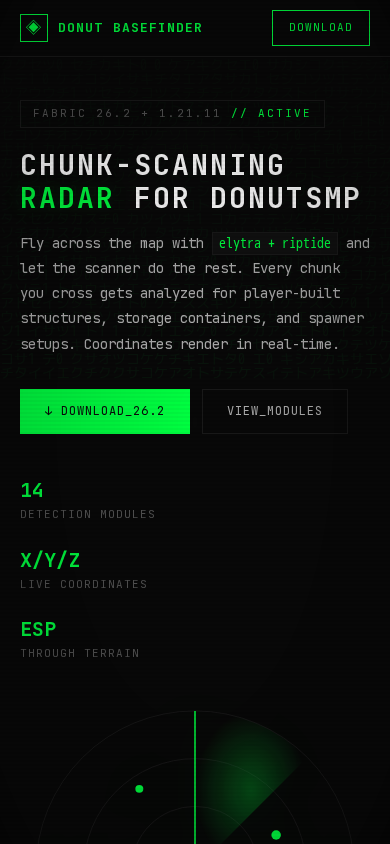
| How the site describes itself | DonutBaseFinder is a client-side Minecraft mod (ESP/base scanner) for Fabric 26.2 and 1.21.11 that detects player bases, storage containers, spawners, tunnels, and logs coordinates; provides module list and installation instructions and direct download links for jar files. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-10-18 and re-scored on 2026-11-04. The certificate, the registration age and the page content describe the site as it was on 2026-10-18.
- The real-world operator identity was not independently verified.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 5/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | Business-model ceiling; Threat-listing ceilingTrustSniffer limits the score of a site whose operator it could not verify, according to the kind of site it appears to be; here that limit is what sets the score. A threat-intelligence feed TrustSniffer monitors listed a file on this site as malicious when the evidence was captured, and that listing caps the score. | Risk |
|---|---|---|
| Malware engines | None flagged itVirusTotal | Clear |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 30 days oldRegistered 2026-09-18 | Risk |
| Web archive | Archived since 20262 snapshots; the archive has almost no record of this site, which counted against it | Watch |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-09-18).
- Public web-archive history exists since 2026.
- No flags from the reputation services TrustSniffer consulted when the evidence was captured.
Full analysis
Overview
DonutBaseFinder is a single-purpose software-download website that promotes a client-side Minecraft mod for the Fabric loader (versions 26.2 and 1.21.11). The mod is an ESP-style "base scanner" aimed at the DonutSMP server. The homepage presents fourteen detection modules, installation instructions and direct download links for the mod's jar files. It is a free-standing utility distribution page with no visible pricing, donation or payment flow, so its monetization model is unclear.
Scam/Impersonation Risk
The decisive finding is that a threat-intelligence feed (recorded as a malware listing) currently lists this site as distributing malware. The listing was last observed after the domain was registered. This is a blacklist hit attributed to that single feed, and the site itself is treated as the actor. The hit is not corroborated by a Google Safe Browsing match or by two or more malicious VirusTotal detections. That limits how far the listing can be independently verified, but it does not remove the signal. The risk is concrete because the site's only function is to hand visitors executable jar files that run inside the game client with the user's privileges. The page does promote cheating tooling (through-terrain highlighting of bases, chests, shulker boxes and spawners, plus coordinate export to a Discord webhook or Xaero's map format). That audience is used to disabling safeguards and sideloading unsigned files. The page itself shows no brand impersonation, credential forms, wallet-connection prompts, cloaking or conflicting legal identities, and its behavioral profile was quiet. The malware listing is given more weight than those clean page-level signals, because a site can look benign while a hosted file is malicious. Classification confidence is moderate (0.75), so this assessment is evidence-based and not conclusive.
- Homepage download section: direct jar download links for the 26.2 and 1.21.11 builds. A feed currently flags the site for malware distribution. This is a single-source listing with no second-source corroboration.
- Domain provenance: registered 2026-09-18 (~0.08 years old). The web archive holds only 2 snapshots, both on 2026-09-19 (1 year tracked), so there is no meaningful operating history.
- Homepage and sandbox runs: no login form, no hidden forms, no external form posts, no wallet or clipboard activity across 3 runs. These signals do not offset the active malware listing.
Regulatory Verification Notes
The site does not claim any licence, registration or regulated status, and it has no legal-entity, terms or about pages naming an operator. No third-party regulatory source was found, and on-page disclosure is unclear. For a game-modification utility this is not a financial-licensing issue. It does mean the operator cannot be tied to a real-world person or company on the available evidence. Identity is therefore unverified (score 30, confidence 0.25), and nothing here supports a claim about who runs the site. Distributing cheating software may also breach the terms of the game and of the DonutSMP server. No third-party broker reputation record matched the site.
- Homepage and navigation (home, scanner, download, archive, about): no named company, contact route or legal notice is presented.
- Domain registration: registrar is Internet Domain Service BS Corp., with the registration running to 2027-09-18.
- Transport encryption: DV certificate issued by WE1, valid to 2026-12-17. DV validation indicates control of the domain only, not the operator's identity.
- Hosting: served from AS13335 (Cloudflare, Inc.).
What to Verify Next
No download from this site should be treated as safe, and no file already obtained should be run until it has been scanned. Anyone who has already installed a jar from the site should remove it, scan the machine with an up-to-date endpoint security tool, and change passwords for accounts used on that device, starting with game, email and Discord accounts. Before any future engagement, the listing status should be re-checked after the site owner states that it has been cleaned. The mod's origin should also be confirmed through an independent channel, such as the DonutSMP community or a developer's source repository, rather than through links on the site.
- Homepage download links: the jar files are the specific artifacts the active malware listing appears to concern.
- Coordinate-export feature: it sends detections to a Discord webhook, so a tampered build could leak data through the same channel. This is a possible risk, not an observed one.
- Domain history: the site is about a month old and has an almost empty archive, so no earlier clean record exists to rely on.
Summary Verdict
The site is rated critically low in trust (score 5.0) and carries an elevated risk posture. An active malware-distribution listing from a threat-intelligence feed is the decisive factor. It outweighs the otherwise tidy appearance of the page, its quiet behavioral profile and its encrypted connection, even though no second source corroborates it. Identity is unverified and the domain is very new, so nothing in the available evidence offsets the listing.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and WAF, and all observed addresses are edge servers, so the origin host cannot be examined independently. The edge network and the valid certificate are mitigating factors only. They do not show that the files served are clean, and edge-only visibility makes it harder to detect rapid content swaps behind the same domain. Light DNS heuristics about a young domain with sparse subdomains are consistent with its age and are not independent evidence of abuse.
Closing Assessment
Prospective users should not download, install or run anything from this site, and should not enter credentials or make payments through it. Any use should be limited to read-only viewing until the malware listing is cleared and the operator's identity is established independently.
Written analysis generated 2026-11-04 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by governance, hosting and network, history in the web archive, and registration and ownership.
01 Governance
- TrustSniffer limits the score of a site whose operator it could not verify, according to the kind of site it appears to be; here that limit is what sets the score.Governance
rule:gov_business_model_cap - A threat-intelligence feed TrustSniffer monitors listed a file on this site as malicious when the evidence was captured, and that listing caps the score.Governance
rule:gov_active_threat_listing
02 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, less than three months before capture.Hosting and network
rule:DNS_NEW_DOMAIN_90D - The domain is young and has almost nothing else set up around it.Hosting and network
rule:DNS_SPARSE_YOUNG_DOMAIN
03 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
04 Registration and ownership
- Some registration details are held behind a privacy service. This is common and legal, and it narrows what can be checked about who runs the site.Registration and ownership
rule:KF_WHOIS_PRIVATE
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of donutbasefinder.com.
- The request stayed on donutbasefinder.com. It was not redirected to another domain. Clear
- Registered through Internet Domain Service BS Corp. Noted
- DNS for this domain is served by ns.cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-09-18. Noted
- The earliest public archive of this site is from 2026-09-19. Watch
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Internet Domain Service BS Corp. |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3030::ac43:8e71 (a CDN edge address; the server behind it was not observed) |
| Name servers | andy.ns.cloudflare.com, brenna.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-17 |
| Domain age | 30 days (registered 2026-09-18) |
| Domain expiry | 2027-09-18 |
| Archive first seen | 2026-09-19 (29 days before capture) |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 0 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about donutbasefinder.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.