Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
donutsmp-mod.github.io shows high-risk / scam indicators.
| What this site appears to be | A third-party hub distributing cracked Minecraft clients and mods targeted at DonutSMP, advertising 'undetected' bypasses, base finders, AH snipers and automation bots. Provides download sizes, requirements (Fabric Loader/API), installation steps and FAQs. Contains warnings about detection and ban risk. No verifiable trust or regulatory information present. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 8% confidenceAbuseIPDB, 6 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Security Alert
Fortinet, Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
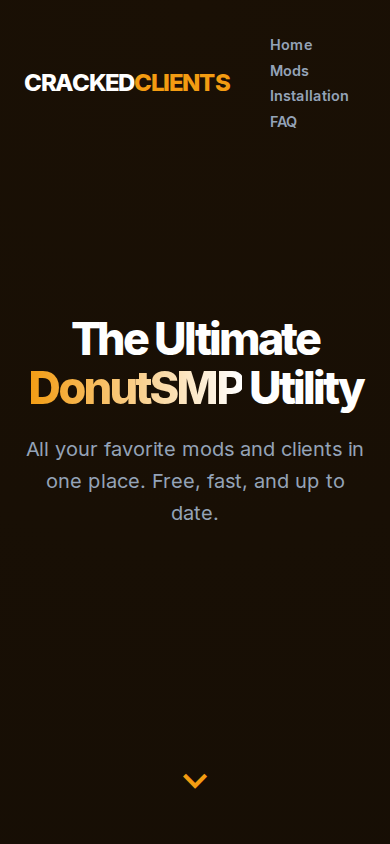
This website is a single-page download hub for cracked Minecraft cheat clients and mods aimed at the DonutSMP server. It presents "undetected" combat clients, base finders, auction-house snipers and anti-cheat bypass utilities for Minecraft 1.21.x. Each listing carries a file size, Fabric Loader and Fabric API requirements, installation steps and an FAQ. The apparent purpose is to distribute free pirated and rule-evading game software, with monetization most likely through advertising or affiliate traffic rather than a sale of any regulated product.
Scam/Impersonation Risk
Contradictory signals are present and are serious. Two major security vendors currently flag the site as malicious, and a third rates it suspicious. Together these amount to a confirmed blacklist hit on external reputation. The offering itself fits a known malware-delivery pattern. The homepage invites visitors to run executable files such as "Vape V4 Client Cracked" (a 2.63 MB download), the "OpSec Anti-Cheat Bypass" mod (420 KB) and the "Krypton Client Cracked". Bundled features include StorageESP, Xray, SilentAura, AimAssist, AutoTotem and auction-house sniping. The page claims they are "100% undetected", that they "spoof your client", and that they "cleanly bypass" server anti-cheat. It offers no evidence for any of this and discloses no author. Cracked cheat binaries are a common vehicle for credential stealers and loaders, and the sandbox found the page itself passive. The risk therefore lies in the files a visitor is invited to run, not in any on-page behavior. Separately, six abuse reports exist against an address on the shared content-delivery network used by the hosting platform. Those reports apply to the platform's shared infrastructure, not specifically to this site, and carry little weight on their own. No confirmed brand impersonation was found. Its name resembles the hosting platform's only because it is a subdomain of that platform. No phishing form, login prompt or wallet-connection mechanic was observed. Evidence:
- Homepage: lists cracked clients and bypass mods with "UNDETECTED" badges, requiring Fabric Loader and Fabric API, with executable download links.
- Homepage: the site's browser-behavior analysis flagged executable downloads, undetectability promises and policy-violating content.
- External reputation: two security vendors rate the domain malicious and one rates it suspicious, with no clean third-party corroboration.
- Web archive: 1 snapshot, first and last seen 2026-10-02, so there is no established history.
Regulatory Verification Notes
The site publishes no legal entity name, terms page, privacy policy, licensing information or verifiable contact route. Its operator is anonymous, and ownership and governance opacity are real and consistent with the nature of the content. The distributed software is built to evade game anti-cheat and is described as cracked, so no regulatory or licensing status could legitimately apply to it. No third-party broker or regulatory record matched this domain. The page's own disclosures consist only of warnings about detection and ban risk, which concern the visitor's exposure and say nothing about the operator's accountability. Hosting and certificate details are routine, and a valid certificate does not offset the reputation findings. Evidence:
- Homepage, installation and FAQ content: no company name, address, licence, terms or privacy documentation.
- Hosting: served from AS54113 (Fastly, US).
- Transport encryption: TLS certificate issued by YR1 (DV), valid to 2026-10-31.
- Third-party broker dataset: no match for the domain.
What to Verify Next
Any need for the advertised tools should be met through the game server's official rules, which will likely prohibit them, and through reputable open-source mod repositories whose code and authors are publicly auditable. Any file already downloaded from this site should be treated as untrusted and not executed. If it has been run, the device should be scanned with a current endpoint-security product, and passwords for game, email and payment accounts should be rotated from a clean device. Because the site sits on a shared hosting platform, its content can be reported to the platform's abuse process. Evidence:
- Homepage: the download listings carry no published checksums, source code or author attribution that would allow independent file validation.
- Homepage: cheat clients and bypasses are marketed as unaffected by anti-cheat, a claim that cannot be tested independently.
- External reputation: current malicious and suspicious ratings from security vendors apply to the domain.
Summary Verdict
The assessment is critical and high-risk. Converging external threat detections, an anonymous operator and a product built around evading protections and running unvetted executables outweigh the benign behavior seen in the page's own sandbox run. The domain shows no sign of the established, accountable operation that would justify trust.
Infrastructure Integrity
The site is delivered through the hosting platform's content-delivery layer, with Fastly as the hosting provider and Akamai edge servers also detected. All observed addresses are edge servers, and the delivery layer is mainstream and well run. This is only a mitigating factor. It reflects the platform's infrastructure and says nothing about the legitimacy or safety of the content published on it, and it cannot offset the reputation findings.
Closing Assessment
The site should not be used for downloads, installation of its files, or any login or financial interaction. Read-only viewing is the most that is proportionate. Anyone who has already run its files should treat the device and the accounts used on it as potentially compromised.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by external reputation, page content.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED - The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME
Signals weighed against the site
- AbuseIPDB: 6 reports on hosting IP 2606:50c0:8000::153 (GitHub, Inc., Content Delivery Network), 8% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of donutsmp-mod.github.io.
- The request stayed on donutsmp-mod.github.io. It was not redirected to another domain. Clear
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | Not available |
| Country | Not available |
| Server IP | 2606:50c0:8000::153 |
| Name servers | Not available |
| CDN / edge network | Lookup incomplete |
| SSL issuer | YR1 |
| SSL expiry | 2026-10-31 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not available |
| Reputation | VirusTotal: 2 flagged | AbuseIPDB: 8% confidence, 6 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about donutsmp-mod.github.io at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.