Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
donutsmpclient.com shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: An ownership check raised a concern: the domain's registration record withholds the owner's details. On its own this does not say who runs the site or that anything is wrong with it.
| How the site describes itself | A site offering free DonutSMP Fabric clients for Minecraft 1.21.11 with direct downloads and Discord community. Emphasizes 'undetected' cheat capability and claims to be free of adware; no independent verification or security provenance visible, making executable downloads potentially risky. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-10-05 and re-scored on 2026-11-04. The certificate, the registration age and the page content describe the site as it was on 2026-10-05.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 13 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 42% confidenceAbuseIPDB, 109 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 23 days oldRegistered 2026-09-12 | Risk |
| Web archive | Archived since 202617 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-09-12).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Overview
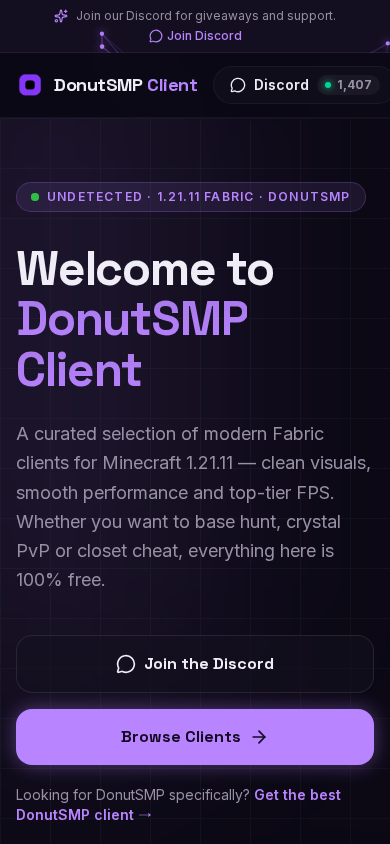
DonutSMP Client is a newly launched download site offering free "DonutSMP" Fabric-based clients for Minecraft 1.21.11. A visitor sees a landing page with Home, Clients, Setup, FAQ and Discord sections, direct .jar downloads and a Discord community invitation. The site's own copy openly advertises "undetected" cheat functionality for base hunting, crystal PvP and "closet cheat" use. It appears to operate as a cheat-client distribution and community-growth funnel, with no visible monetization.
Scam/Impersonation Risk
The site shows confirmed adverse contradictions: it is blacklisted by external threat-intelligence sources, and a substantial number of security engines independently classify the domain as malicious, including three top-tier endpoint-security vendors. That convergence is decisive, and the site's own business model fits it. The primary action offered is downloading unsigned executable archives that run inside a player's game environment, a classic malware-delivery vector (infostealers, session-token theft, remote-access payloads). The homepage's reassurances rest on assertion alone: "zero adware", "no malware", "verified and cleanly packaged" and "Direct & Safe Downloads", with no checksums, code signing, source repository or independent audit. The statistics also do not agree with each other. The hero card advertises "100+ Modules" while the stats row says "80+", and "17k+ downloads", "1.4K Discord members" and "99.9% uptime" counters appear on a domain that has existed only weeks. These are unverifiable social-proof devices. The "undetected" selling point means the product is built to evade anti-cheat, and legitimate security tooling is likely to treat that evasion as malicious. Abuse reports exist against the network address the site resolves to, but that address is shared CDN infrastructure, so those reports are not reliably attributable to this site alone and carry limited weight beside the direct detections. No brand impersonation, credential-harvesting form, wallet-connect flow or cloaking was observed, and no conflicting legal identities appear. The risk is malicious-payload exposure rather than phishing.
- Homepage: advertises "Undetected · 1.21.11 Fabric", "100% free" cheat clients and a "DonutSMP Client Hack" link, with direct .jar downloads as the main call to action.
- Homepage: contradictory module counts ("100+ Modules" vs "80+") and round-number popularity counters, with no verifiable provenance for the safety claims.
- Domain provenance: registered 2026-09-12 (~23 days old, 0.06 years); the web archive holds 17 snapshots, all from 2026 (2026-09-12 to 2026-09-13, 1 year tracked), so there is no established history.
- Reputation: 13 security engines flag the domain as malicious and 2 as suspicious; the abuse-report volume of 109 applies to the shared CDN address.
Regulatory Verification Notes
The site is not presented as a regulated service, and no licensing is relevant to its stated activity. The only disclosure on the pages reviewed is a footer notice that the project is not affiliated with Mojang Studios or Microsoft and that "Minecraft" is a trademark of Mojang Synergies AB. No operating company, individual, contact address, terms of service, privacy policy or complaint channel is identified. For a site distributing executable software, this absence of accountable-party disclosure is a transparency gap that removes any route for redress. No third-party broker or regulatory-database entry was matched, so no external reputational context exists beyond the threat detections. The site's technical hygiene is basic: it has valid transport encryption, but the certificate is only domain-validated and says nothing about the operator.
- Footer: the only disclosure is the Mojang/Microsoft non-affiliation and trademark statement; no legal entity, address or policy pages are linked.
- Navigation: the Clients, Setup, FAQ and Discord pages sit on-domain, but none was observed to carry operator identity or terms.
- Transport security: TLS certificate issued by WE1 (domain-validated), valid to 2026-12-11; registrar NAMECHEAP INC.
- Hosting: served from AS13335 (Cloudflare, Inc.).
What to Verify Next
The domain's status should be treated as unresolved until the detections are cleared by the reporting vendors. Anyone who still needs this software should skip the site and use only a source with a published code repository, reproducible builds and a verifiable maintainer history. If a file has already been downloaded, it should not be run. It should be scanned and, if necessary, analysed in an isolated, disposable environment, and any account that has run it should be treated as potentially exposed. The Discord invitation should be assessed independently of the website, and official support or contact channels confirmed through a route that does not depend on this site's links.
- Homepage and Clients pages: downloads are served as bare .jar files with no published hash, signature or source link to compare against.
- Homepage: the Discord invite is the sole external destination, so the community's authenticity cannot be established from the site itself.
- Runtime behaviour: repeated page loads produced heavy external-resource traffic, a final-destination mismatch and 48 console errors, so a fresh independent scan of any downloaded file is warranted.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
Summary Verdict
The assessment is critical and clearly cautionary. Independent threat detections, a weeks-old domain and a business built on distributing undetectable executable cheat tools converge on a high likelihood of malicious or harmful software delivery. Real-world operator identity remains unverified, and nothing in the evidence offsets the adverse findings.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and WAF, and only edge addresses were observable. That is a mitigating factor for availability and basic transport security, not evidence of legitimacy. Edge-only visibility also prevents independent verification of the true hosting origin, and it can make rapid content swaps harder to spot. The young domain with a sparse DNS footprint is consistent with a recently stood-up property.
Closing Assessment
The site should not be used for downloading or running any of its files, and no login credentials, payment details or game-account access should be given to it or to anything obtained from it. At most, passive read-only viewing is proportionate, and any prior interaction should be followed by an account-security review.
Written analysis generated 2026-11-04 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content, hosting and network and behaviour in a sandbox.
01 External reputation
- A confirmed external listing marks this domain as malicious: at least five security engines including a leading vendor, ten engines, or Google Safe Browsing.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
03 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, less than three months before capture.Hosting and network
rule:DNS_NEW_DOMAIN_90D
04 Behaviour in a sandbox
- Most of the files the page loaded (scripts, images, fonts) came from other domains. This is about where its content is hosted, not about data being sent elsewhere.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 109 reports on hosting IP 185.158.133.1 (CLOUDFLARENET), 42% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of donutsmpclient.com.
- The request stayed on donutsmpclient.com. It was not redirected to another domain. Clear
- Registered through NAMECHEAP INC. Noted
- DNS for this domain is served by registrar-servers.com, across 2 name servers. Noted
- The domain is registered until 2027-09-12. Noted
- The earliest public archive of this site is from 2026-09-12. Clear
- It is hosted on CLOUDFLARENET, a network registered in AE; the provider, Cloudflare, Inc., lists its country as US. Noted
Domain intelligence
| Registrar | NAMECHEAP INC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. (the provider lists its country as US) |
| Network registered in | AE |
| Server IP | 185.158.133.1 (a CDN edge address; the server behind it was not observed) |
| Name servers | dns1.registrar-servers.com, dns2.registrar-servers.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 1 |
| Edge IP addresses | 1 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-11 |
| Domain age | 23 days (registered 2026-09-12) |
| Domain expiry | 2027-09-12 |
| Archive first seen | 2026-09-12 (23 days before capture) |
| Archive snapshots | 17 |
| Reputation | VirusTotal: 13 malicious | AbuseIPDB (CDN edge address, not the host): 42% confidence, 109 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about donutsmpclient.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.