Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
eltoadpepe.xyz shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 12 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 3 months oldMost scam domains are under a year old | Risk |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
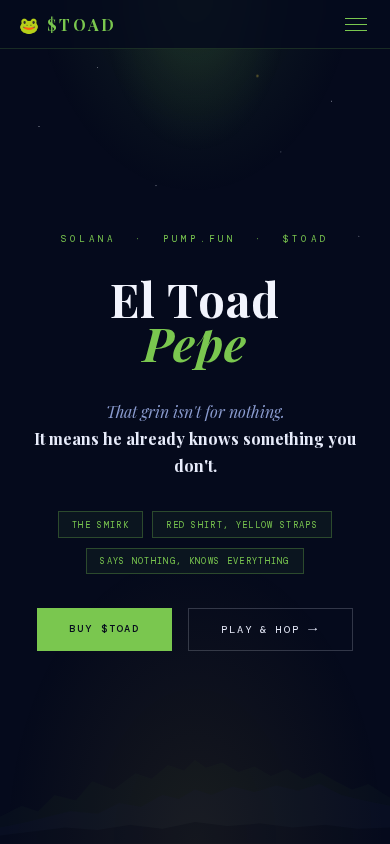
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
El Toad Pepe is a single-domain promotional website for a meme-coin project branded "El Toad Pepe ($TOAD)". Its homepage carries the tagline "That Grin Means Something". It presents a cryptocurrency token themed on the Pepe frog meme and appears to exist to promote the token and attract visitors toward holding or trading it.
Scam/Impersonation Risk
Multiple independent security vendors currently flag the domain as malicious, including several tier-one engines, and the site also appears on an external blacklist. This is a confirmed blacklist condition. It is the decisive finding and is serious enough to override every mitigating technical signal. Taken with a domain registered only weeks ago and a meme-token theme, a category associated with rapid launch-and-abandon schemes, the pattern warrants a clearly cautionary posture. No conflicting legal identities and no brand impersonation were observed, and the wallet-interaction tests found no drainer behaviour, clipboard tampering or content cloaking. Even so, the homepage generated a high proportion of traffic to external hosts, several background requests and form submissions to third parties, and repeated script errors during browsing. That behaviour is consistent with a hastily assembled or externally dependent page and offers no reassurance against the vendor detections. Evidence:
- Homepage and domain reputation: several tier-one security vendors currently rate the site malicious, and an external blacklist also lists it.
- Domain provenance: registered 8 August 2026 (~0.22 years, ~79 days old), expiring 8 August 2027, through Global Domain Group LLC.
- Homepage behaviour: three of three sandbox visits completed, with 14 external background requests, 4 external POST submissions, and 10 console errors. No wallet-drainer, clipboard-hijack or cloaking activity was detected.
Regulatory Verification Notes
The operator's real-world identity could not be independently established, and ownership of the domain is opaque. That opacity is an administrative limitation, not an identity contradiction. No financial or virtual-asset regulatory standing for the project could be linked to the site, and the third-party broker reputation database returned no match. That absence is neutral and is not a verdict. Any token sale, trading or yield function would, in most jurisdictions, fall under virtual-asset or securities rules, so the lack of an identifiable, accountable operator matters more here than for an informational site. The transport-layer posture is routine and offers no evidence of legitimacy. Evidence:
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Encryption: the TLS certificate was issued by WE1, with domain-validation (DV) only and no organisational identity validation, and is valid to 2027-01-04.
- Third-party database: no broker-reputation record matched the site.
What to Verify Next
Before any engagement, the token's contract address and the project's official social channels should be confirmed through an independent route, such as a reputable block explorer or the channels of exchanges that claim to list it. The site's own links should not be used for this. The flagged status should be re-checked on the major reputation services in a few weeks, to see whether the detections persist or clear. If the project claims any licensing or registration, it should be confirmed directly with the issuing registry. Evidence:
- Homepage token branding: the "$TOAD" ticker and tagline are marketing claims and cannot be treated as proof of a legitimate token.
- Domain age: a registration of about eleven weeks leaves no operating history against which to judge the project's claims.
- Reputation status: the current vendor detections are the baseline against which any future re-check should be compared.
Summary Verdict
The assessment is critically low and security-forward. Active external threat detections, compounded by a very young domain and an unestablished operator, outweigh the site's technically sound basics. The available evidence does not support treating the site as safe for sensitive interaction.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and WAF, and only edge addresses were observed, so the true hosting origin could not be seen. A valid certificate from a recognised issuer and mainstream infrastructure are mitigating factors only. They are widely available to any registrant, including malicious ones, and cannot offset the reputation findings. Edge-only visibility also means page content could be changed quickly without any change in the observable hosting.
Closing Assessment
Wallet connections, credential entry and payments or token purchases should be avoided entirely. Any review of the site should be limited to passive, read-only viewing from an isolated environment. Nothing should be downloaded from it.
Written analysis generated 2026-10-27 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, behaviour in a sandbox, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D - The domain is young and has almost nothing else set up around it.Hosting and network
rule:DNS_SPARSE_YOUNG_DOMAIN
03 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH
04 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of eltoadpepe.xyz.
- The request stayed on eltoadpepe.xyz. It was not redirected to another domain. Clear
- Registration is published under Global Domain Group LLC. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-08-08. Noted
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Global Domain Group LLC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3032::ac43:b91c |
| Name servers | KONNOR.NS.CLOUDFLARE.COM, VENUS.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-04 |
| Domain age | 0.22 years (continuous registration) |
| Domain expiry | 2027-08-08 |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 12 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about eltoadpepe.xyz at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.