Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
ethzm.club shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 2 months oldMost scam domains are under a year old | Risk |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | CLOUDFLARENETServer in US | Noted |
The page as captured
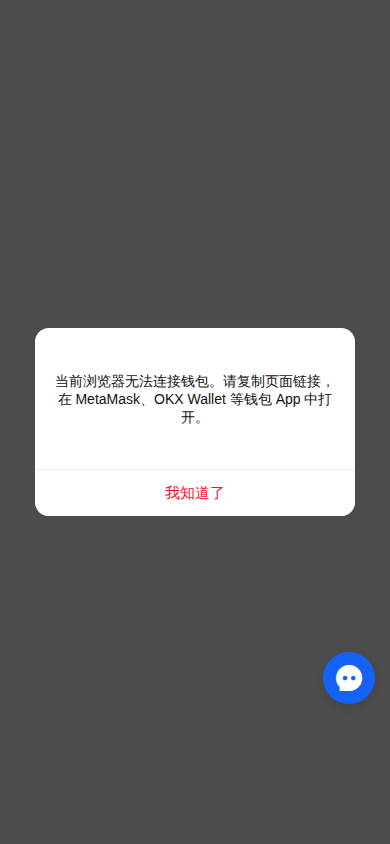
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
This website is a very recently launched, single-page property whose homepage is titled "DeFi" and carries only a few lines of text, roughly a sentence or two. It presents itself under a decentralised-finance label but offers no visible product descriptions, team information, or documentation. Its apparent purpose is to serve as a front for a crypto or DeFi-themed offering, though the page content does not say what that offering is.
Scam/Impersonation Risk
Contradictory signals are present and decisive. The domain is currently flagged as malicious by multiple threat-intelligence engines and as suspicious by others, and it also appears on an external blacklist. That convergence is a confirmed blacklist-level warning rather than a soft reputational note. The risk is heightened by the domain's extreme youth: it was registered only a couple of months before analysis, so there is no operating history to offset the flags. The homepage is nearly empty yet still triggers heavy third-party traffic. In the sandbox, the page made dozens of external requests, including a notable number of outbound POST submissions, all to destinations on the known-benign list. No wallet-connection prompts, clipboard manipulation, hidden forms, credential forms posting off-site, cloaking, or fingerprinting were observed. The behaviour therefore does not show an active drainer, but it also does not explain why a one-paragraph page needs that much outbound data flow. No conflicting legal identities or brand impersonation were observed. The elevated risk rests on the blacklist and threat-intelligence listings and on the lack of any track record. Evidence:
- Homepage: a "DeFi" title with about 150 characters of visible text and no described products, yields, or tokens.
- Domain registration: registered August 2026 (about 66 days old, ~0.18 years).
- Threat intelligence: 2 engines report the domain as malicious and 2 as suspicious, and an external blacklist also lists it.
- Sandbox behaviour (3 of 3 runs completed): 23 external XHR/fetch calls and 12 external POSTs, none to non-whitelisted hosts; no wallet, clipboard, or cloaking activity.
Regulatory Verification Notes
The homepage, the only page captured, discloses no operating company, licence, registration number, or jurisdiction. It also has no terms, privacy, or risk-disclosure content. The site presents itself in a financial-technology category, so these omissions matter for any user considering a financial interaction. This is a verification gap and not by itself proof of wrongdoing. Real-world operator identity remains unverified, and nothing on the site supports a regulated or licensed status. No third-party broker-reputation data was available to add context. The technical posture is that of a standard, freshly provisioned site, and it does not offset the threat listings. Evidence:
- Homepage: no company name, licence, registration number, or legal pages are presented.
- Domain registrar: registered through eName Technology Co., Ltd., with a registration term running to August 2027.
- Hosting: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: TLS certificate issued by WE1 (domain-validated only, DV), valid to January 2027. This confirms an encrypted connection and does not confirm the operator's identity.
What to Verify Next
Before any engagement, establish who operates the site through independent channels. Check any claimed company or licence in the relevant national financial-regulator registries, because the site itself offers nothing to check. Confirm the official support and contact channels through an offline or independently sourced route. Re-check the domain's threat-intelligence status at a later date to see whether the listings are retracted or confirmed. If the site later presents wallet connections, token approvals, or deposit flows, these should be treated as unverified until independent confirmation of the operator exists. Evidence:
- Homepage: no identifiable operator or registry reference exists to cross-check.
- Domain history: the domain is only a few months old, so there is no prior ownership or content history to rely on.
- Threat listings: current detections can change, so re-checking them is a meaningful step.
Summary Verdict
The overall posture is clearly cautionary and high-risk. A confirmed blacklist-level warning from several independent threat sources, combined with a brand-new domain and a content-free page, outweighs the technically valid encryption and clean sandbox behaviour. Identity is unverified, and the evidence supports no basis for treating this site as legitimate.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and WAF, and all four observed addresses (two IPv4, two IPv6) are Cloudflare edge servers in the US, with no origin server visible. This is a mitigating factor only. It shows the site uses mainstream protective infrastructure, but it prevents independent verification of where the content is actually hosted and allows content to be swapped quickly behind the edge. The certificate is valid and issued by a known authority. A domain-age and sparse-subdomain heuristic is consistent with a newly created property, but it is unconfirmed and carries little weight on its own. The infrastructure cannot offset the reputational risk.
Closing Assessment
The site should not be used for login, credential entry, wallet connection, or any financial transaction, and read-only viewing is the most that is prudent. It should be re-assessed only if the threat listings are cleared and a verifiable operator identity emerges.
Written analysis generated 2026-10-25 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, hosting and network, registration and ownership, behaviour in a sandbox.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D - The domain is young and has almost nothing else set up around it.Hosting and network
rule:DNS_SPARSE_YOUNG_DOMAIN
03 Registration and ownership
- The registration record withholds contact details for the operator.Registration and ownership
rule:KF_WHOIS_HIDDEN - Registration details are held behind a privacy service, so no operator is named publicly. This is common and legal, and it also means there is nobody to check.Registration and ownership
rule:KF_WHOIS_PRIVATE
04 Behaviour in a sandbox
- Many of the responses the page received looked generated rather than served normally.Behaviour in a sandbox
rule:BEHAV_SYNTHETIC_RESPONSES_HIGH
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 15% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of ethzm.club.
- The request stayed on ethzm.club. It was not redirected to another domain. Clear
- Registration is published under eName Technology Co., Ltd.. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-08-19. Noted
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | eName Technology Co., Ltd. |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3032::ac43:c285 |
| Name servers | kira.ns.cloudflare.com, fonzie.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-16 |
| Domain age | 0.18 years (continuous registration) |
| Domain expiry | 2027-08-19 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 2 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about ethzm.club at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.