Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
fomovotes-45.pages.dev shows high-risk / scam indicators.
| What this site appears to be | A memecoin trading interface centred on the $SPACEHOOD token on Robinhood Chain. It shows buy/sell controls, a cash deposit prompt, a leaderboard of large unverified PnL figures, and a '100x' promotional line, with no disclosed operator, audit, risk warning, or contact information. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Listed as unsafeGoogle | Risk |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 7 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20261 snapshot | Clear |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Google flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
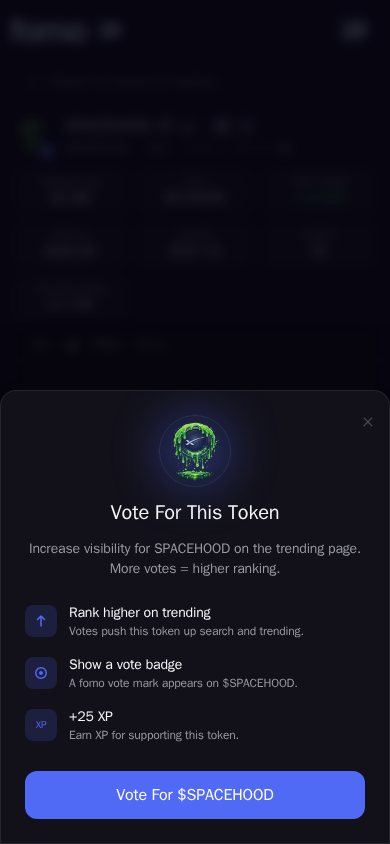
This website is a single-page memecoin trading interface, branded "fomo votes", centred on a token called $SPACEHOOD on a chain named Robinhood Chain. It presents buy and sell controls with preset amounts from $10 to $1,000, a prompt to deposit cash, a trending token list, and a leaderboard of individual traders' profit figures with attached "thesis" comments. Its apparent business model is to draw visitors into depositing funds and trading speculative tokens, with revenue implied from trading fees.
Scam/Impersonation Risk
This is a high-risk site, and the contradictions are confirmed. The domain is on a blacklist, and a major browser-security threat feed has classified it under social engineering, which covers deceptive or phishing-type content. A separate multi-engine reputation scan also returned one malicious and one suspicious detection. Behavioural testing found strong cloaking: the page's content and appearance changed substantially once the sandbox interacted with it. That pattern is consistent with a page that shows different material depending on the visitor's actions. The site sits on a free subdomain of a shared hosting platform and was created only days ago, with a single archive capture to its name. Page analysis flagged a close resemblance between the hostname and the hosting platform's name, but no specific brand impersonation was confirmed. The page's own content adds to the concern. The leaderboard shows unverifiable profit figures such as a trader reporting a gain above $63,000, or +1,151.27% on one position. Another trader's note reads "400k in fees sitting there". A promotional line states "many of you will never hit a 100x. I will." The trending list advertises gains of 66,295.08% and 102,401.75% on individual tokens. Together with a deposit prompt and trade presets, these claims create high-pressure, fear-of-missing-out conditions around funds the operator can take custody of. The token metrics shown (about 5,000 holders, roughly $237K of liquidity) cannot be tied to any independent audit or proof of reserves. The name Robinhood Chain may also lead visitors to assume an association with a well-known financial brand, and the page offers nothing to substantiate one. Evidence:
- Homepage trading view: the deposit prompt, the $10–$1,000 buy presets and the "100x" promotional line, with no risk warning.
- Homepage leaderboard: individual profit figures (for example $59,142.92 and $63,270.44, and +1,151.27%) and the "400k in fees sitting there" comment, none of them verifiable.
- Behavioural sandbox: strong content change after interaction across three runs, and a threat-feed classification for social engineering.
- Domain provenance: created in 2026 (about 8 days old). The web archive holds 1 snapshot, captured on 2026-10-11 (first and last seen on the same date).
Regulatory Verification Notes
The page identifies no operator, company name, registered address, licence, or registration number. It also publishes no terms, privacy policy, or audit report, and it offers no contact channel. The business is a custodial-style deposit and trading service in high-risk digital assets, and for that activity these omissions are material. Owner details are incomplete, so there is no independent route from the site to a responsible legal entity. This is ownership opacity rather than an identity contradiction. On its own, the absence of a licence is a verification gap and not proof of wrongdoing. Here it adds to the confirmed contradictions above. No third-party broker-reputation record matched this site, so that source adds nothing in either direction. Evidence:
- Homepage: no operator, licence, risk disclosure, or contact information is present anywhere in the captured page content.
- Hosting infrastructure: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: TLS certificate issued by YE2 (DV, domain-validated only), valid to 2026-12-31. This confirms an encrypted connection only, not the identity of the operator.
What to Verify Next
Treat the site as unsafe for any financial or credential interaction until an independent party has established who operates it. The token's contract address should be checked on an independent blockchain explorer, covering holder concentration, liquidity lock status, and any audit. The claim of a link to Robinhood or its chain should be tested by going to that company's official website from a separately sourced address and not through this page. Any claimed operator, licence, or registration should be checked directly with the relevant financial regulator's public register. Official support or contact channels should be confirmed through an independent route and not through the site. Evidence:
- Homepage: the token contract address is shown in truncated form, so the full address needs independent confirmation.
- Homepage: no operator or licence is stated, so any regulatory check has no named entity to start from.
- Threat-feed status: the classification is current as of this analysis and should be rechecked before any reassessment.
Summary Verdict
The available evidence supports a clearly adverse trust posture. Confirmed blacklisting, deceptive-content classification, and cloaking behaviour all point the same way, and the page content matches the profile of a high-pressure speculative scheme. Nothing found offsets this, and the site's operator identity remains unverified.
Infrastructure Integrity
The site is delivered through Cloudflare's CDN and WAF, and every observed address is an edge server. The origin server was not observable, so hosting cannot be verified independently. The transport encryption is valid and the hosting provider is mainstream. These are mitigating factors only, and they do not offset the reputation findings. This kind of shared infrastructure is also freely available to new, anonymous sites, so it says nothing about the operator's legitimacy.
Closing Assessment
The site should be avoided for any login, credential entry, deposit, or trade, and nothing should be connected to it or sent to it. Anyone who has already interacted with it should stop, review recent account and wallet activity, and report the page to the relevant security authority.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, hosting and network, page content.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of fomovotes-45.pages.dev.
- The request stayed on fomovotes-45.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-10-11. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2f55 |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 8 |
| Edge IP addresses | 8 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2026-12-31 |
| Domain age | 0.02 years (continuous registration) |
| Domain expiry | Not available |
| Archive first seen | 2026-10-11 |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 1 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 1 match |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about fomovotes-45.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.