Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
getbackevm.netlify.app shows high-risk / scam indicators.
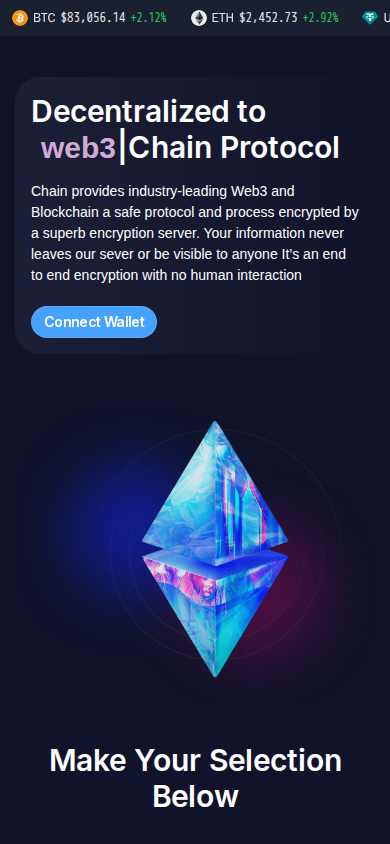
| What this site appears to be | A React single-page site that describes itself as a Web3 'Chain Protocol' support hub. It lists many support categories, including claiming tokens, presales, airdrops, fund recovery for missing balances, and wallet login help, with a stated requirement to be a 'trusted payment source' before buying tokens. The page names Coinbase Wallet and Ledger but gives no company identity, contact channel, or verifiable service terms. The copy claims end-to-end encryption and no human interaction, which is unsupported. The fund-recovery and token-purchase flows are high-stakes and lack any proof, which matches common wallet-support scam pattern... |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | None flagged itVirusTotal | Clear |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 1% confidenceAbuseIPDB, 4 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by DigiCert Global G2 TLS RSA SHA256 2020 CA1 | Noted |
| Hosted by | AMAZON-02Server in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- VirusTotal and Google Safe Browsing had no flags for this domain; its hosting IP carries AbuseIPDB reports below the confidence level TrustSniffer treats as a flag.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
This website is a single-page React application, hosted as a subdomain on a developer platform. It presents itself as a Web3 "Chain Protocol" support hub. It offers a menu of help categories for crypto-wallet users, including token claims, presales, airdrops, and recovery of "lost or missing funds". It appears to function as a wallet-support and token-claim landing page, and no revenue model is stated.
Scam/Impersonation Risk
No identity contradictions, confirmed phishing, or confirmed impersonation were observed, but the content of the homepage carries a clearly elevated fraud profile. The page offers a long menu of high-stakes support flows: "Claim Token", "Claim Airdrop", "Presale" (buy/claim), "Missing/Irregular balance" (recover lost or missing funds), "Wallet glitch / wallet error", "Login", "Locked Account", cross-chain bridge, staking, swap, and NFT minting. It names Coinbase Wallet and Ledger, but no operator, address, or contact channel is given. The "Buy Coins/Tokens" entry says an account "must be marked as a trusted payment source" before trading. This is an unexplained gating mechanism that implies payments or asset transfers to an unidentified party. This combination of unsolicited fund recovery, presale purchasing, and wallet-login help is a well-known pattern in wallet-support and drainer-style schemes. The page also claims that data is protected by a "superb encryption server", that "your information never leaves our server", and that the service is "end to end encryption with no human interaction". These claims are unsupported and technically incoherent for a support service that depends on user interaction. The page title is the unmodified default "React App", with no description or structured metadata, which suggests a minimally built page rather than an established service. The domain sits on a free platform-hosted subdomain, which gives no independent branding or ownership signal. One threat-intelligence engine flagged the site as suspicious; this single flag is unconfirmed. Taken with the content findings, it supports caution but is not treated as a confirmed listing. Evidence:
- Homepage: lists token claim, presale, airdrop, wallet login, locked-account, and "recover lost/missing funds" flows, with the "trusted payment source" requirement for token purchases.
- Homepage: asserts end-to-end encryption, "no human interaction", and data that "never leaves our server" with no supporting evidence, and names Coinbase Wallet and Ledger without any partnership proof.
- Homepage: titled only "React App" with no meta description, canonical, or structured data, and no links to any other pages were captured.
- Behavioral observation: three sandbox runs found no wallet-drainer activity, clipboard manipulation, hidden forms, or cloaking on the initial page. This applies only to the landing page and not to the destinations behind each "Click here" option.
Regulatory Verification Notes
The site presents no legal or identity pages: no company name, registered address, terms of service, privacy policy, refund terms, or licence or registration claim. For a service that asks users to claim assets, buy presale tokens, or recover funds, this is a material disclosure gap. The site makes no regulatory claim, so none can be assessed, and there is no third-party reputational match for this site. The site's registration and operator identity remain unconfirmed, and the transport-layer evidence below cannot establish who runs the service. Evidence:
- Homepage: no operating entity, jurisdiction, licence, or registration number appears, and no terms or privacy page is linked.
- Transport encryption: the TLS certificate is organisation-validated, issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1, valid to 2027-03-19, with the subject organisation Netlify, Inc. This identifies the hosting platform, not the operator of the support page.
- Hosting: the site is served from AS16509 (AMAZON-02, Amazon.com, Inc., US).
What to Verify Next
Whoever is considering interacting with the site should first establish who operates it. The wallet vendors it names, Coinbase Wallet and Ledger, should be asked through their own official support channels whether this page is an authorised support route. Any claim about token claims, airdrops, presales, or fund recovery should be checked against the official project's own announcements, reached from a source other than this page. Any contact channel should be confirmed through an independent route. The "trusted payment source" requirement should be questioned before any payment or transfer is considered, because no legitimate custodian needs a user to approve a destination through an anonymous support page. Evidence:
- Homepage: names two wallet brands without any stated relationship, so an authorisation claim can be tested directly with those vendors.
- Homepage: the stated "trusted payment source" gating has no explanation, fee schedule, or refund terms.
- Homepage: no operator name or contact channel is published, so identity must be established outside the site.
Summary Verdict
The available evidence supports an elevated-risk assessment. The page's content pattern, the absence of any verifiable operator, and the unsupported security claims converge on a profile typical of wallet-support and fund-recovery schemes. No hard contradiction was found, but the site cannot be treated as an apparently legitimate service. The valid certificate and clean-looking technical behavior do not offset the content risk.
Infrastructure Integrity
The site is served through AWS-based CDN/WAF edge infrastructure, and all four observed addresses are edge nodes, so the origin server is not observable. This is a mitigating factor only and says nothing about the operator's legitimacy. Edge-only visibility also prevents independent hosting verification and can allow content to be swapped quickly. Four abuse reports exist against one of the shared provider addresses. Because these addresses are shared CDN infrastructure used by many tenants, the reports are not attributed to this site specifically.
Closing Assessment
Treat the site as unsuitable for wallet connection, seed-phrase or credential entry, and payments or asset transfers. Anyone needing wallet support or a token claim should use the official channels of the wallet or project concerned, reached independently of this page.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by page content, several checks together.
01 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED
02 Several checks together
- No external feed lists the site, but its own page content reads as risky.Several checks together
rule:HYB_POSITIVE_EXTERNAL_NEGATIVE_PAGE
Signals weighed against the site
- AbuseIPDB: 4 reports on hosting IP 2a05:d014:58f:6200::258 (Amazon Data Services Ireland Ltd, Content Delivery Network), 1% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of getbackevm.netlify.app.
- The request stayed on getbackevm.netlify.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc., US |
| Country | US |
| Server IP | 2a05:d014:58f:6200::258 |
| Name servers | Not available |
| CDN / edge network | Detected (aws) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | DigiCert Global G2 TLS RSA SHA256 2020 CA1 |
| SSL expiry | 2027-03-19 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 0 flagged | AbuseIPDB: 1% confidence, 4 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about getbackevm.netlify.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.