Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
gibddru.vercel.app shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on vercel.app, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
| How the site describes itself | The page offers a downloadable recording and instructs the user to bypass warnings and enable installation from unknown sources. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-10-10 and re-scored on 2026-11-03. The certificate, the registration age and the page content describe the site as it was on 2026-10-10.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 marked it maliciousVirusTotal; a single engine, not a confirmed listing | Watch |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 74 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | Not availableNo registration record was returned | Noted |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by WR1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
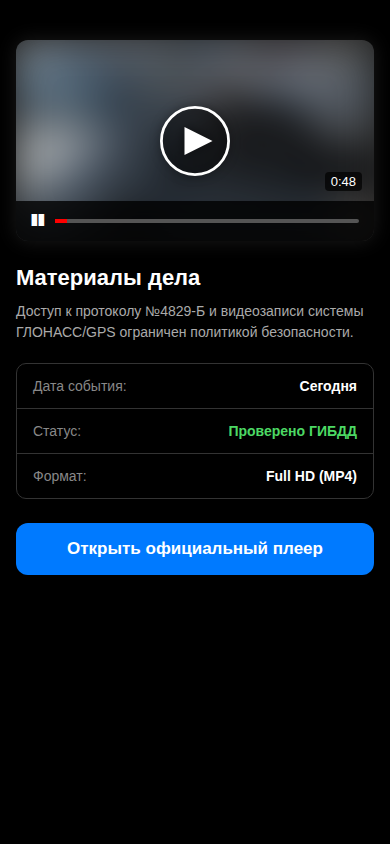
This website is a single-page download prompt, written in Russian and styled as an official traffic-incident "Recorder" viewer. It claims to hold a case file, a protocol number and a Full HD dashcam video of an event dated "today", and it says the material is restricted by security policy and "verified by the traffic police". The page then pushes the visitor to download a small file of about 2.4 MB and to install it by following step-by-step instructions. Its apparent purpose is to distribute an executable or mobile (APK) payload under a pretext of official evidence access, not to provide a verifiable service.
Scam/Impersonation Risk
Contradictory signals are present, and the posture is explicitly cautionary. An external threat-intelligence source has the site blacklisted, and page analysis classifies the homepage as a malicious download and install prompt. The mechanics match a known social-engineering pattern for malware delivery. The page instructs the visitor to click "Download anyway" or "OK" if a browser warning appears, then to open the file and enable installation "from this source" in device settings. Each step is designed to defeat a protective control. The "restricted case file", the protocol number and the "Verified by traffic police" status are asserted with nothing to support them. They work as pressure and credibility cues. The page offers no verifiable contact route or operator identity, so the claim of official provenance cannot be corroborated. No brand impersonation or conflicting legal identities were established, and no credential-harvesting form was observed. The risk is therefore driven by payload delivery and by the instructions to override safeguards. No fraud-style transactions were seen. Sandbox runs recorded no external network posts, hidden forms or clipboard manipulation. This does not offset the explicit instruction to sideload an application, which is the central danger.
- Homepage: instructs the visitor to bypass download warnings and enable installation from unknown sources, which is characteristic of malicious APK distribution.
- Homepage: asserts "verified by traffic police" status and a restricted protocol and video record, with no supporting substantiation or contact route.
- Homepage: shows a repeat-download link and an "Open recording" button for a 2.4 MB file, consistent with a lure-and-install flow.
- External reputation: at least one threat-intelligence engine rates the site malicious and another rates it suspicious, and an external blacklist flag is raised.
Regulatory Verification Notes
The site presents no legal, terms, privacy or about pages. It names no operating entity and states no licence or registration, and it holds no regulatory standing that could be assessed. Its pretext as a police-linked service cannot be reconciled with a site that publishes no institutional identity. No third-party broker or regulatory-database match exists for it, so no reputational signal arises from that channel. The site's hosting and transport layer are ordinary and do not indicate legitimacy. Cheap, anonymous platform hosting is available to anyone and carries no assurance about the operator.
- Homepage: contains no operator name, address, licence, registration number or legal documentation.
- Hosting infrastructure: served from AS16509 (AMAZON-02, Amazon.com, Inc., US), a generic cloud-platform tenancy.
- Transport encryption: TLS certificate issued by WR1 at domain-validated (DV) level, valid to 2026-11-27 (48 days remaining). DV certificates confirm only domain control, not organisational identity.A TLS certificate is what puts the padlock and https:// in your browser and encrypts the connection. "WR1 at domain-validated" is the name of the authority that issued it. DV (domain validated) means the issuer only confirmed who controls the domain name, not which person or company runs the site. "Valid to" is the date it expires.
- Third-party broker dataset: no match for this site.
What to Verify Next
Because the site's own content is the hazard, verification should not involve interacting with it. Any claim of an incident, a protocol number or a video record should be checked through the traffic police's genuine public channels, reached independently of this page. Anyone who has already downloaded or installed the file should treat the device as potentially compromised. They should remove the application, revoke the "install from this source" permission and run a reputable mobile security scan. If accounts, banking apps or messaging apps were opened on that device afterwards, credentials for them should be changed from a clean device. Organisations seeing this link in messages or campaigns should report it to the hosting platform and to the national cyber-incident authority.
- Homepage: the only action offered is a file download with sideloading instructions, so no on-site step can be treated as safe.
- Homepage: the page names no verifiable contact route, so confirmation of the claimed case must come from official channels outside this site.
- Browser behaviour: the page prompts a download and requests that unknown-source installation be enabled, so any device that followed the steps warrants a security check.
Summary Verdict
The site is assessed as high-risk and untrustworthy. Content analysis, external threat intelligence and behavioural review converge on a malicious-software distribution lure, and the governance and page-risk assessments cap the outcome at the lowest tier. No credible legitimacy evidence offsets this. The site is best regarded as an active threat to visitors' devices and personal data.
Infrastructure Integrity
The site sits behind Cloudflare and Vercel edge infrastructure, with six observed addresses, all edge-side. The origin server was not observable, so the underlying host cannot be independently confirmed, and edge-only visibility can mask rapid content swaps. Roughly seventy abuse reports attach to a Vercel shared-platform address linked to this site. They were assessed as applying to shared provider infrastructure and were discounted. The abuse feed itself lists the address as a whitelisted content-delivery address. The platform's protections and valid certificate are mitigating context only. They do not offset the page-level and reputation findings.
Closing Assessment
The page should not be opened on a personal or corporate device, and nothing from it should be downloaded or installed. No permission to install from unknown sources should be granted for it. Links to it should be blocked, reported and deleted without further interaction.
Written analysis generated 2026-11-03 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by external reputation, page content and several checks together.
01 External reputation
- Two VirusTotal engines, or one leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_MEDIUM
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 74 reports on hosting IP 216.198.79.67 (AMAZON-02), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of gibddru.vercel.app.
- The request stayed on gibddru.vercel.app. It was not redirected to another domain. Clear
- It is hosted on AMAZON-02, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | AMAZON-02 - Amazon.com, Inc. |
| Network registered in | US |
| Server IP | 216.198.79.67 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare, vercel) |
| Resolved IP addresses | 6 |
| Edge IP addresses | 6 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR1 |
| SSL expiry | 2026-11-27 |
| First seen (web archive) | Not available (the web archive has no record of this address; a site on vercel.app has no registration of its own) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 1 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 74 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about gibddru.vercel.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.