Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
hifibridge.org shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 14 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 3 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20263 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
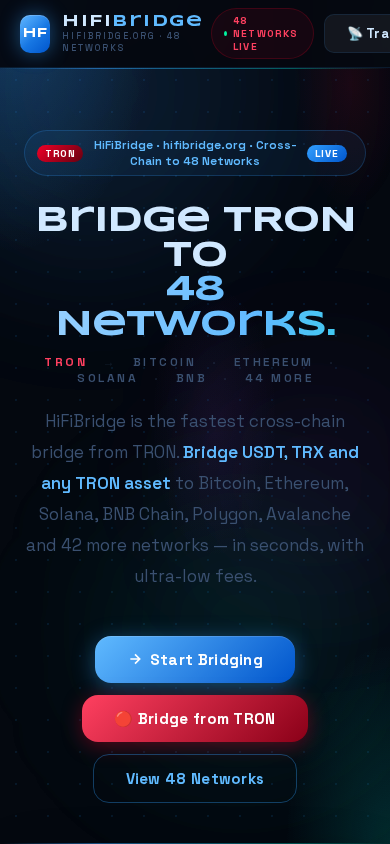
HiFiBridge is a single-page website that presents itself as a TRON-centred cross-chain bridge. Its homepage title promises transfers between TRON and Bitcoin, Ethereum, Solana and 48 networks in total. The apparent business model is a crypto-asset bridging and transfer service. A visitor would be asked to move digital assets between blockchains through the site's interface. These descriptions come from the site's own presentation. Identity verification status is unknown (score 50, confidence 0.3), because AI page analysis was unavailable. The page was captured, but the site's connection to a real-world brand or person has not been independently established.
Scam/Impersonation Risk
Contradictory signals are present. VirusTotal and an external blacklist source both report the domain. Several security engines, including established endpoint-security vendors, flag it as malicious. At least two engines do so, and the external detections are unspecified. Together these meet the confirmed-blacklist condition, which is a hard contradiction. Google Safe Browsing did not flag the domain. No brand impersonation, phishing indicators or conflicting legal identities were observed. The concern therefore rests on third-party blacklist detections rather than on an identity contradiction. This is not a finding of impersonation. The domain was registered only a few months ago, and its archive record is thin and recent. The site therefore has no track record that could offset the detections. That weighs heavily because a bridge asks users to authorise on-chain transfers that are irreversible once signed. The sandbox found no wallet-drainer behaviour, clipboard manipulation, hidden forms or cloaking. These observations are mitigating, but they do not cancel the external detections, which come from independent engines rather than from this sandbox run. The homepage also sends a large share of its requests to third-party endpoints, and some data submissions go to destinations outside the expected set. That pattern is consistent with the external detections, though it is not proof of malicious intent. It prevents the site from being treated as self-contained. Evidence:
- Homepage: independent security engines (VirusTotal and an external blacklist source) currently classify the domain as malicious, and the combined detections trigger a confirmed blacklist condition.
- Domain registered 2026-07-10 (~0.29 years old), as shown in the registration record.
- Web archive holds 3 snapshots from 2026-09-05 to 2026-09-21 (reported as 1 year tracked), so there is no meaningful history.
- Homepage behaviour: most observed network requests went to external hosts, and some non-whitelisted destinations received submitted data.
Regulatory Verification Notes
The site is not covered by any third-party regulated-entity record, and no broker-reputation match exists. Its legal and governance disclosures could not be established from the evidence, and the registration record does not identify an owner. On-page disclosure is unclear. This is ownership and governance opacity, not an identity contradiction. A service that moves customer assets across chains would ordinarily be expected to name an operating entity, a jurisdiction and any applicable money-transmission or virtual-asset registrations. The evidence does not establish that any of these exist. The site's real-world operator is not independently verified, and no authority has vouched for it. Any statement about who runs the site should be read as unconfirmed. The domain also does not appear in the DeFi protocol directory consulted, so no independent protocol recognition supports the bridge's claims. Transport encryption is valid, but a certificate only secures the connection. It says nothing about the operator's legitimacy. Evidence:
- Registration record: registrar is Atak Domain Bilgi Teknolojileri; owner details are incomplete.
- TLS certificate issued by WE1 (DV, domain validation only), valid to 2026-12-10.
- Hosted on AS13335 (Cloudflare, Inc., US).
- Homepage: no regulatory registration or named legal entity could be confirmed from the captured content.
What to Verify Next
The priority is to avoid any wallet connection, token approval or fund transfer until the detections are resolved. If the service is genuinely needed, its operator and official channels should be confirmed through an independent route, such as a project profile from an established blockchain ecosystem directory or the official TRON community channels. The bridge's smart-contract addresses should be compared with an independent block explorer, and a published security audit should be checked against its auditor's own site. Any licensing or registration claim should be confirmed with the relevant financial regulator's registry. The current status of the security-engine detections should also be re-checked, since they may be cleared if the operator remediates and requests a review. Evidence:
- Homepage: the stated reach of 48 networks cannot be corroborated from the evidence available.
- Domain registration is under four months old, so no long-standing community references can be assumed.
- Third-party detections are active at the time of assessment and should be re-checked before any reconsideration.
Summary Verdict
The site carries a high-risk posture, and the trust score is 0.0 (critical trust band). The external blacklist detections are the decisive factor. They outweigh the otherwise unremarkable technical hygiene. The operator's identity is unverified, and the domain is too new to build a reliable reputation. Classification confidence is 0.75, so this is a strong but not absolute assessment. The evidence does not support treating the site as trustworthy for any sensitive or financial activity.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and WAF, and all observed addresses are edge servers, so the origin host was not visible. This is a mitigating factor only. It is consistent with a mainstream front end, but it also limits independent verification of where the content is actually served. It does not offset the external blacklist detections.
Closing Assessment
The site should be limited to passive viewing only. No wallet should be connected, no credentials entered, and no funds sent through it. Organisations should block or escalate access until the operator is independently verified and the security-engine detections are cleared.
Written analysis generated 2026-10-26 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by external reputation, hosting and network, history in the web archive, behaviour in a sandbox, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
03 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
04 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS
05 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of hifibridge.org.
- The request stayed on hifibridge.org. It was not redirected to another domain. Clear
- Registration is published under Atak Domain Bilgi Teknolojileri A._.. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-07-10. Noted
- The earliest public archive of this site is from 2026-09-05. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Atak Domain Bilgi Teknolojileri A._. |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3031::6815:bcc |
| Name servers | david.ns.cloudflare.com, virginia.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-10 |
| Domain age | 0.29 years (continuous registration) |
| Domain expiry | 2027-07-10 |
| Archive first seen | 2026-09-05 |
| Archive snapshots | 3 |
| Reputation | VirusTotal: 14 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about hifibridge.org at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.