Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
higgspad.app shows high-risk / scam indicators.
| What this site appears to be | Higgspad's page describes the $HIGGS Holder Crates program, where wallets holding the $HIGGS token on Solana can see a tier and a potential allocation based on amount and duration held. The page discloses that allocations are not guaranteed, the token is speculative, and tier boundaries and snapshot dates are not published. It also describes Higgspad as a Solana launchpad for AI influencer tokens, with fees funding a $HIGGS burn. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 5 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 15 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 202636 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
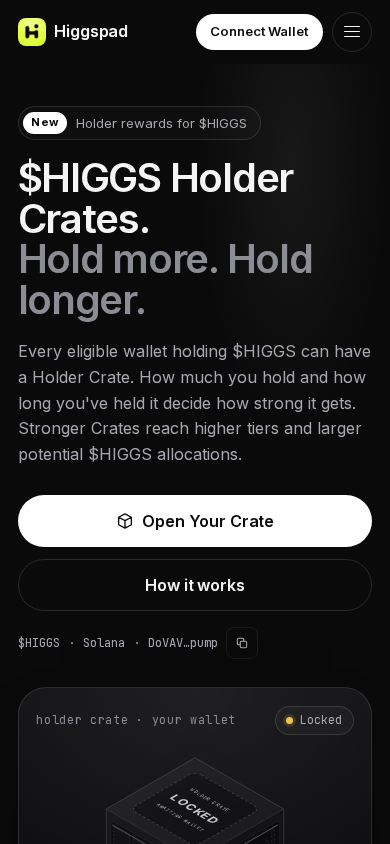
Higgspad is a Solana crypto-token launchpad site for AI-influencer tokens. The page analysed presents the "$HIGGS Holder Crates" program, a rewards page where a connected wallet holding the $HIGGS token is shown a tier from Copper to Platinum and a "potential" token allocation. The allocation depends on the amount held and the holding time. The apparent business model is to turn creator fees from launched tokens into buy-and-burn of $HIGGS, funded by trading activity on a third-party token-launch platform. The site promotes a speculative, newly created token.
Scam/Impersonation Risk
Contradictory signals are present, and they drive a clearly cautionary assessment. Several independent threat-intelligence engines flag the domain as malicious or suspicious, including at least one tier-one security vendor. Together these constitute a confirmed blacklist hit. No brand impersonation, phishing form, credential-harvesting login, wallet-drainer behaviour, or conflicting legal identity was observed, so the concern comes from reputation and from the domain's extreme newness, not from a demonstrated impersonation. The site's own content adds structural risk. The Holder Crates page invites visitors to hold more and hold longer to reach higher tiers and larger allocations, yet it publishes no tier boundaries, allocation formula, or snapshot dates. This is an opaque value flow. Visitors are encouraged to accumulate a speculative token without being able to calculate what they would receive. The same page links the burn mechanism to trading volume on a memecoin launch platform, so the program's value depends on continued trading activity. The page does acknowledge that allocations are not guaranteed and that the token is speculative, which is candid but does not offset the opacity. The wallet-connect feature is described as not yet live, and sandbox testing found no wallet-drainer or clipboard-hijack behaviour. However, the browsing sessions did record several outbound data submissions to non-whitelisted external destinations, which warrants attention on a page that will eventually ask for a wallet connection. Evidence:
- Domain registered 2026-10-04 (~15 days old, 0.04 years) through NICENIC INTERNATIONAL GROUP CO., LIMITED; the domain is brand new for a site soliciting token-holder engagement.
- 36 archive snapshots spanning 2026-10-04 to 2026-10-07, which confirms the site is only days old.
- Holder Crates page: tiers (Copper to Platinum) and "potential allocation" are shown without any published thresholds, formula, or snapshot dates.
- Sandbox sessions on the Holder Crates page recorded outbound POST requests to non-whitelisted external destinations.
Regulatory Verification Notes
The site shows no regulatory standing of any kind. The page claims no licence, registration, or regulator. It names no legal entity, team members, or operator, and it shows no smart-contract audit. Domain ownership details are also incomplete, which adds ownership opacity. This is a governance gap, separate from the reputational findings above. The page states that the program is speculative, but it does not identify who administers the allocations or who controls the burn mechanism. Without a named accountable party, a participant has no recourse route if allocations are withheld or the program changes. No third-party broker or regulatory-database match was found, and that absence is neutral and not a verdict. The visitor-facing security basics are in place. The site uses a valid certificate, but that only encrypts traffic and says nothing about the operator. Evidence:
- Holder Crates page: no licence, registration number, legal entity, team identity, or audit report is shown.
- Served from AS13335 (Cloudflare, Inc., US); the hosting provider reveals nothing about the operator.
- TLS certificate issued by YE1 (DV, domain-validated only), valid to 2027-01-02.
What to Verify Next
Any contact with this site should start with independent confirmation of who runs it. Check the token's contract address on a public Solana block explorer, looking at the creator wallet, holder concentration, and the authority settings, and compare them with what the page says. Look for the burn transactions the page describes, and check whether the claimed buy-and-burn actually occurs on-chain. Confirm the site's official social account and domain through channels independent of the site itself, because a domain this new could be copied or mimicked. Re-check the threat-intelligence listings after a few weeks to see whether the detections persist or clear. Confirm the official support and contact channels offline before sharing any information. Evidence:
- Holder Crates page: the token contract is referenced only by a truncated address, so the full address needs to be taken from an independent source.
- Holder Crates page: the burn mechanism is described only in prose, with no transaction or dashboard reference.
- Holder Crates page: the only social presence is a single X account, which needs independent confirmation.
Summary Verdict
The assessment is critical. Confirmed blacklist detections on a days-old domain, together with an undisclosed operator and an allocation scheme with unpublished rules, put the site in the elevated-risk category. The site shows no conclusive evidence of impersonation, so the concern is reputational and structural, not a demonstrated scam. Legitimacy cannot be established on the available evidence, and the posture is clearly cautionary.
Infrastructure Integrity
The site is fronted by Cloudflare's CDN and WAF. All four observed addresses are CDN edge servers, and the origin server was not observable. The edge-only view stops independent verification of the real hosting and can mask rapid content swaps. This protective infrastructure is only a mitigating factor. It is standard and available to any site, legitimate or not, and it cannot offset the external threat detections.
Closing Assessment
Treat the site as read-only content at most. Do not connect a wallet, sign transactions, buy or hold $HIGGS on the strength of the page, or provide credentials or payment details until the operator has been identified independently and the external detections have cleared.
Written analysis generated 2026-10-19 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by governance, external reputation, hosting and network, page content, behaviour in a sandbox, registration and ownership.
01 Governance
- A threat feed lists this domain as malicious, and that caps the score whatever the other checks found.Governance
rule:GOV_CRITICAL_BLACKLIST
02 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
03 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
04 Page content
- The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME
05 Behaviour in a sandbox
- The page sent data to a destination TrustSniffer does not recognise.Behaviour in a sandbox
rule:BEHAV_NONWHITELISTED_POSTS
06 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 55/100 |
| Identity verification confidence | 60% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of higgspad.app.
- The request stayed on higgspad.app. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-10-04. Noted
- The earliest public archive of this site is from 2026-10-04. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3032::6815:2f33 |
| Name servers | olof.ns.cloudflare.com, rita.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2027-01-02 |
| Domain age | 0.04 years (continuous registration) |
| Domain expiry | 2027-10-04 |
| Archive first seen | 2026-10-04 |
| Archive snapshots | 36 |
| Reputation | VirusTotal: 5 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about higgspad.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.