Verdict
Several risk patterns were present. Do not send money or personal details until you have verified this business another way.
hihiihageg.pages.dev is low-trust and potentially risky.
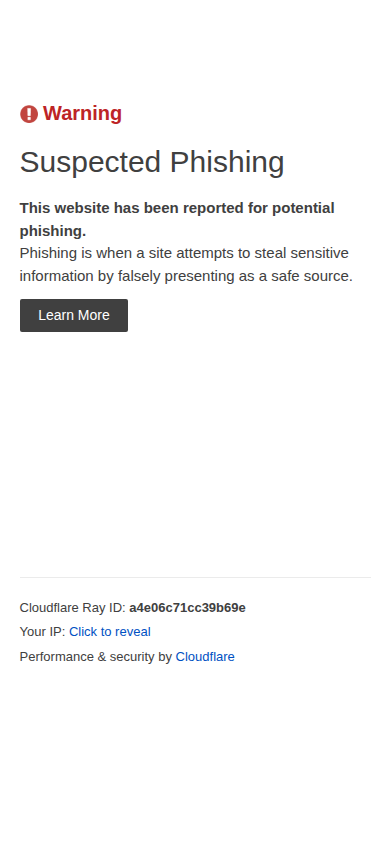
| What this site appears to be | The captured page is a Cloudflare interstitial warning that the target website has been reported for potential phishing. It contains no service content, forms, or links, so the site's actual purpose and legitimacy cannot be verified from this capture. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
| Hosted by | CLOUDFLARENETServer in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
The assessed website is a subdomain on a free static-hosting platform, with a randomly generated name. When visited, it does not show its own content. It returns a security warning page stating that the site "has been reported for potential phishing". The page has no products, forms, links, contact details or legal text, so the site's purpose and business model cannot be determined from what was captured.
Scam/Impersonation Risk
Contradictory signals are present, and they justify a clearly cautionary posture. Independent threat-intelligence sources currently flag the domain as malicious, which amounts to a confirmed blacklist listing. The platform's own gateway also interposes a phishing warning in place of the site's content. The page analysis shows a strong lookalike resemblance between the subdomain and the hosting platform's own domain, which is a typical pattern for credential-harvesting pages that borrow the credibility of a well-known service. Because the warning page replaced the real content, the nature of the underlying lure (login capture, payment or onboarding) could not be observed. For the same reason, the absence of visible forms or wallet interactions should not be read as reassurance. Free-hosting subdomains of this kind can be swapped to different content quickly, and the site's own behavior ranges from a bare notice to heavy background network traffic. No conflicting legal identities were observed, and no specific brand other than the hosting platform was targeted.
- Homepage capture: a phishing-suspected interstitial replaced the site's content, and the capture was blocked with an access-denied response.
- Reputation checks: two independent security engines classify the domain as malicious, and the external blacklist flag is confirmed.
- Homepage analysis: the subdomain closely resembles the hosting platform's own domain, a typosquat-style similarity.
- Behavioral sandbox: three runs completed, with 13 console errors and 51 external background requests, none to non-whitelisted destinations.
Regulatory Verification Notes
No licensing, registration or legal-entity information could be assessed, because the only content observed was the warning notice and not the site's own legal, about or terms pages. The operator's real-world identity could not be independently connected to any person or organization. No third-party broker or regulatory-database record matched this domain. That absence is neutral, but it offers no mitigating context against the threat listings described above. The business model could not be classified, so no financial-services or custody claims can be credited to the site.
- Homepage capture: no company name, license number, jurisdiction or policy text is visible.
- Broker-reputation lookup: no match for this domain.
- Hosting infrastructure: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: the TLS certificate was issued by YE1 (DV, domain-validated only) and is valid to 2026-12-26. Domain-level validation confirms control of the domain, not the operator's identity.
What to Verify Next
Before any engagement, the origin of the link that led to this domain should be established, and any message, advertisement or referral that supplied it should be treated as suspect until independently confirmed. Anyone claiming to be represented by this site should be contacted through an official channel found independently of this domain. Credentials, payment details and wallet approvals should not be submitted to it. If the domain was entered by an existing user of a legitimate service, that service's official application or bookmarked address should be used instead. A site owner who believes the listing is erroneous should seek review with the hosting platform and the listing sources.
- Homepage capture: the platform warning states the site was reported for phishing, so referral provenance is the main open question.
- Reputation checks: the active malicious detections must clear before any independent re-assessment.
- Page analysis: no contact or support channel is exposed on the captured page, so only an independently sourced route is viable.
Summary Verdict
The available evidence supports an elevated-risk, clearly cautionary posture. Confirmed threat-intelligence detections, a platform-issued phishing warning and a lookalike naming pattern converge on the same conclusion, and no offsetting legitimacy evidence outweighs them. Sensitive interactions such as login, credential entry and financial activity fall outside any defensible use of this site, and the most that can be said for it is read-only observation.
Infrastructure Integrity
The site is served entirely through Cloudflare's CDN and WAF network, with four edge addresses on AS13335 in the United States and no origin server address visible. The protection is a mitigating factor only. The edge-only view prevents independent verification of the real hosting location and can mask rapid content changes behind the same address. The valid TLS certificate and the recognized network provider say nothing about the operator's intent, and they cannot offset the active reputation detections.
Closing Assessment
The domain should not be used for login, credential entry, payments or file downloads, and any link to it should be treated as hostile until the listings are cleared and a fresh assessment is made.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by page content, several checks together, external reputation.
01 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
02 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
03 External reputation
- A small number of malware engines flagged this domain. On its own this is a weak signal.External reputation
rule:EXT_BLACKLIST_MEDIUM
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of hihiihageg.pages.dev.
- The request stayed on hihiihageg.pages.dev. It was not redirected to another domain. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:310c::ac42:2ef6 |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2026-12-26 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 2 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about hihiihageg.pages.dev at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.