Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
hopium.web.app shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on web.app, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
| How the site describes itself | A crypto dashboard for 'HOPIUM MACHINES' that runs a token risk-scoring tool (rug detector) and sells paid credits payable only in its own $HOPIUM token. Users connect a wallet on Robinhood Chain (id 4663) with a signature, and the page promotes staking and machine rewards without disclosing the source of rewards, the operating entity, or contact details. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-10-22 and re-scored on 2026-11-05. The certificate, the registration age and the page content describe the site as it was on 2026-10-22.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 3% confidenceAbuseIPDB, 4 reports; shared hosting inflates reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | Not availableNo registration record was returned | Noted |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by WR4 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
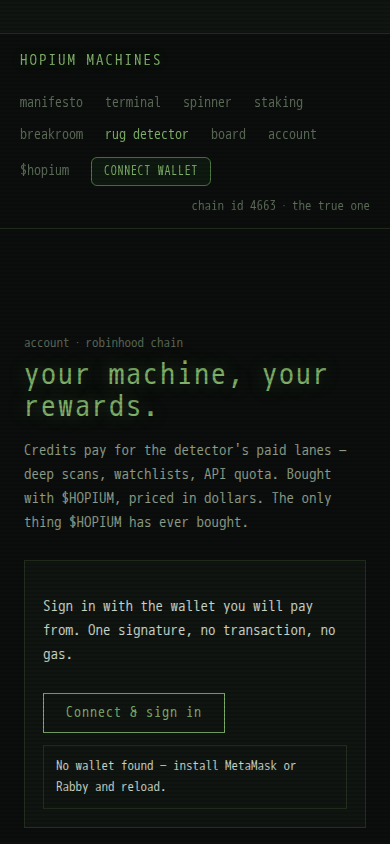
HOPIUM MACHINES is a crypto-token dashboard presented as a "rug detector": it assigns risk labels such as "too new" or "high" to a list of small-cap tokens. It sells paid credits for deep scans, watchlists and API quota, and those credits can be bought only with the project's own $HOPIUM token. Visitors are prompted to connect a browser wallet and sign in on a chain labelled "Robinhood Chain" (chain id 4663, described on the page as "the true one"). The page also promotes staking and "your machine, your rewards". The apparent business model is a token-utility project that monetises its own currency.
Scam/Impersonation Risk
Contradictory signals are present, so this is the dominant concern. The site is blacklisted by external threat-intelligence sources: several independent detection engines flag it as malicious or suspicious, and a separate reputation listing corroborates this. No brand impersonation, phishing form or conflicting legal identity was observed. The risk comes from the reputation findings combined with the page's own mechanics. The page presents itself as an independent token-risk auditor, yet it accepts payment only in its own $HOPIUM token, which it describes as "the only thing $HOPIUM has ever bought". It does not disclose this conflict of interest. Its closing note that the page "is not satire" is a self-assertion, not evidence. The staking and "machine rewards" messaging gives no source or funding mechanism for the rewards, a pattern consistent with token-promotion schemes that depend on new buyers. The wallet sign-in asks for a signature without a transaction. The sandbox did not observe drainer or clipboard-hijacking behaviour, but a wallet-signature prompt on a flagged site is still a sensitive interaction. The sandbox also saw a large share of outbound network activity to third-party destinations and a heavy rate of script errors. Four abuse reports exist against a shared edge address belonging to a large infrastructure provider. They apply to shared infrastructure and cannot be attributed to this site specifically, so they are context only.
- Homepage: credits are "bought with $HOPIUM, priced in dollars", with no alternative payment route and no disclosure that the same project issues the token being sold.
- Homepage: "your machine, your rewards" and the staking menu entry appear with no explanation of reward origin or funding.
- Homepage: the scanned tokens, including names such as DOGSHIT, ELON and COW, are labelled "too new" or "high" with no methodology or independent audit.
- Behavioural sandbox: the wallet-connect and signature-request prompts were triggered across all three runs, with substantial external traffic and repeated console errors.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
Regulatory Verification Notes
The page names no operating company, registered address, licence or jurisdiction, and offers no working contact channel. Ownership and governance are therefore opaque. This is a disclosure gap in its own right, and it matters more here because the site invites users to hold, stake and spend a token. No regulatory registration or third-party broker listing was found, and no licensing claim is made on the page. The only disclaimer is that risk scores are heuristics and not financial advice. The site runs on a shared hosting-platform subdomain, so the address itself carries no brand or corporate identity. A valid but basic domain-validated certificate confirms only encrypted transport, not who operates the site.
- Homepage: no company name, licence number, physical address or support contact is shown.
- Homepage footer note: "risk scores are heuristics, not financial advice, not proof of fraud. do your own research".
- Transport encryption: TLS certificate issued by WR4 (DV), valid to 2026-12-22.A TLS certificate is what puts the padlock and https:// in your browser and encrypts the connection. "WR4" is the name of the authority that issued it. DV (domain validated) means the issuer only confirmed who controls the domain name, not which person or company runs the site. "Valid to" is the date it expires.
- Hosting: served from AS54113 (Fastly, Inc., US).
What to Verify Next
Before any wallet interaction, the claimed chain (id 4663) should be checked against independent, official chain registries and the issuer's own channels. The $HOPIUM token contract, its supply distribution, holder concentration and liquidity locks should be inspected on a public block explorer. An independent smart-contract audit should be requested, and any staking or reward contract should be reviewed for who controls minting and withdrawals. The operating entity and official support channels should be confirmed through an independent route, not through links on the site itself. Any wallet used for testing should be a fresh, empty one. The signature request should be read in full before it is approved.
- Homepage: wallet sign-in is advertised as "one signature, no transaction, no gas", which should be checked against the actual message text shown by the wallet.
- Homepage: no contract address, audit report or reward-source documentation is linked.
- Threat-intelligence results: the malicious and suspicious detections should be re-checked for current status before any engagement.
Summary Verdict
The assessment is clearly adverse. Corroborated external threat detections, an undisclosed conflict of interest, and unexplained reward mechanics together outweigh the site's technically sound basics. Operator identity remains unverified, and nothing on the page supports the legitimacy claims it makes.
Infrastructure Integrity
The site is delivered through a recognised content-delivery network with a valid certificate. This is a mitigating factor for transport integrity and availability only. All observed addresses are edge nodes, so the origin server is not visible. Protective infrastructure does not offset the reputation findings and says nothing about the operator's intent.
Closing Assessment
Read-only viewing is the only appropriate use. Wallet connection, signature approval, credit purchases, staking and any token purchase should be avoided until independent audits and a verifiable operator identity exist.
Written analysis generated 2026-11-05 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by external reputation, page content and behaviour in a sandbox.
01 External reputation
- Three or more VirusTotal engines, or two including a leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY
03 Behaviour in a sandbox
- Most of the files the page loaded (scripts, images, fonts) came from other domains. This is about where its content is hosted, not about data being sent elsewhere.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 4 reports on hosting IP 2620:0:890::100 (FASTLY), 3% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of hopium.web.app.
- The request stayed on hopium.web.app. It was not redirected to another domain. Clear
- It is hosted on FASTLY, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | FASTLY - Fastly, Inc. |
| Network registered in | US |
| Server IP | 2620:0:890::100 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (fastly) |
| Resolved IP addresses | 2 |
| Edge IP addresses | 2 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR4 |
| SSL expiry | 2026-12-22 |
| First seen (web archive) | Not available (the web archive has no record of this address; a site on web.app has no registration of its own) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 2 malicious | AbuseIPDB (CDN edge address, not the host): 3% confidence, 4 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about hopium.web.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.