Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
hyperfoundationstakings.xyz shows high-risk / scam indicators.
| What this site appears to be | A page styled as an official 'Pre-Trial Claims Portal' for delivering copyright claim notices naming Sony Music Entertainment as claimant. It supplies no verifiable court, legal-identity, or contact details, uses a blank correspondence address and garbled text, and sets a response deadline with an account-based appeal route. These are typical markers of a legal-threat scam pattern, so the page is rated high risk. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 2 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 22 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20262 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE2 | Noted |
The page as captured
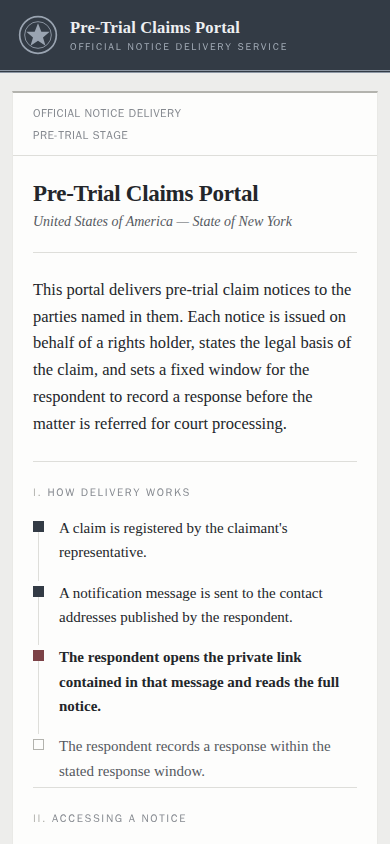
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
The website is a single-page site styled as an official "Pre-Trial Claims Portal" and "Official Notice Delivery Service" for the State of New York. It says it delivers pre-trial copyright claim notices on behalf of a rights holder, and it names Sony Music Entertainment as claimant. It tells recipients to open a private link from a notification message, record a response within a fixed window before the matter is "referred for court processing," and use an account-based appeal route. It shows no payment flow, and its only apparent purpose is to make visitors respond to a legal threat.
Scam/Impersonation Risk
Cross-source evidence converges on a high-risk, actively cautionary posture. External reputation sources currently flag the domain as malicious and suspicious. This includes detections from major security vendors, and the domain also appears on an external blacklist. This is a confirmed blacklisting, not a soft reputational signal. The page content matches the reputation data. It presents itself as an authority and sets a deadline, which is a legal-threat pattern, but it gives no court name, case reference, legal entity, or working contact route. The correspondence address is blank and the text is garbled and incomplete. The page says notices are reachable only through a private link and that appeals require an account. This is a typical funnel for pressuring recipients into following links and creating credentials. The assurance that the portal "never asks for a password, a verification code, a one-time code or payment details" does not offset these gaps, because the page is the delivery mechanism for that kind of approach. The domain name refers to staking and "hyperfoundation," which has no evident link to a legal-notice service. That mismatch suggests the domain was registered for another purpose, or is a throwaway. The page names a well-known music company as claimant but gives no verifiable connection to it. No brand impersonation was detected, and no phishing form was observed. No conflicting legal identities were found, because the site gives no identity at all.
- Homepage: presents itself as an "Official Notice Delivery Service" for New York, with no court, case number, legal entity, or working correspondence address. The address field is blank and the text is garbled.
- Homepage: sets a fixed response window with a threat of court referral, delivers notices only through private links, and ties appeals to an account.
- Domain registration: registered in 2026 (about 22 days old, ~0.06 years), through NICENIC INTERNATIONAL GROUP CO., LIMITED, with expiry in 2027-09.
- Web archive: only 2 snapshots, both from 2026 (1 year tracked), so there is no established history behind the site.
- External reputation: 2 malicious and 3 suspicious detections, with two tier-one security vendors among the flaggers, plus an external blacklist hit.
Regulatory Verification Notes
The site claims a quasi-judicial function but cites no statute, court, registry, or licence. No regulator, licensing body, or registration number is referenced, and no entity is named as operator. A real notice service, court, or law firm would be expected to disclose these, so the omission is significant here. The site's authority rests only on its own styling. No third-party broker or regulatory record matched this domain, and that absence neither supports nor weakens the site's claims. The reputational warnings above come from threat-intelligence sources and are not a regulatory ruling.
- Homepage: lists no licence, court, registry, or legal-entity details despite presenting itself as an official notice authority.
- Homepage: gives no identifiable operator or working contact channel. Real-world identity could not be tied to any person or organisation.
- Hosting and encryption: TLS certificate issued by YE2 (domain-validated only, valid to 2026-12-28). Domain-validated encryption confirms only control of the domain, not the identity of any operator.
What to Verify Next
Anyone who received a message pointing to this portal should treat it as unverified. They should not open its private links. They should check whether any real claim exists by contacting the named claimant or its legal department through a channel they find independently, not through any link or address in the message. If the message mentions a court or case, that should be checked directly with the relevant New York court clerk through its published public contact details. Organisations should route the message and link to their security team for reporting and blocking, and should confirm official support or contact channels offline before anyone replies.
- Homepage: states that notices can be reached only at the private address in the notification message. That address cannot be checked from the site itself.
- Homepage: names a specific rights holder as claimant, so that claimant is the right party to confirm or deny any claim.
- Domain registration: created about 22 days before this analysis, which is inconsistent with any long-running legal notice operation.
Summary Verdict
The site is assessed as high-risk and unsafe for any sensitive interaction. Confirmed external blacklisting, a very recently registered domain, and a page that mimics legal authority without verifiable substance all point the same way. These signals point to a likely legal-threat scam, not to a legitimate notice service.
Infrastructure Integrity
The site is served through Cloudflare's CDN and WAF (AS13335, Cloudflare, Inc., US). All four observed addresses are Cloudflare edge servers, and the origin server was not observable. This protective infrastructure is a mitigating factor only. It shows that the site is hosted on mainstream infrastructure, but it says nothing about the operator's legitimacy. It can also hide the actual host and make rapid content changes harder to detect. It does not offset the external threat detections or the content-level findings. A heuristic flag for a young domain with sparse subdomains is consistent with the registration timeline but is not independently confirmed.
Closing Assessment
Do not click links, enter credentials or personal data, create an account, or pay anything in response to messages that point to this site. Delete such messages and report them to the relevant security team or fraud-reporting body. Anyone who has already interacted with the site should change any passwords they entered and watch their accounts for unusual activity.
Written analysis generated 2026-10-21 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, page content, several checks together, hosting and network.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of hyperfoundationstakings.xyz.
- The request stayed on hyperfoundationstakings.xyz. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-29. Noted
- The earliest public archive of this site is from 2026-09-29. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3033::ac43:a150 |
| Name servers | ANDRONICUS.NS.CLOUDFLARE.COM, LEANNA.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE2 |
| SSL expiry | 2026-12-28 |
| Domain age | 0.06 years (continuous registration) |
| Domain expiry | 2027-09-29 |
| Archive first seen | 2026-09-29 |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 2 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about hyperfoundationstakings.xyz at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.