Verdict
Several risk patterns were present. Do not send money or personal details until you have verified this business another way.
incident-ledger.com is low-trust and potentially risky.
| What this site appears to be | Security advisory describing a 2026 seed-generation vulnerability affecting older Ledger devices, guidance to update firmware, replace seeds, and migrate funds, plus product and support links. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 7 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 20253 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2025.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Kaspersky flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
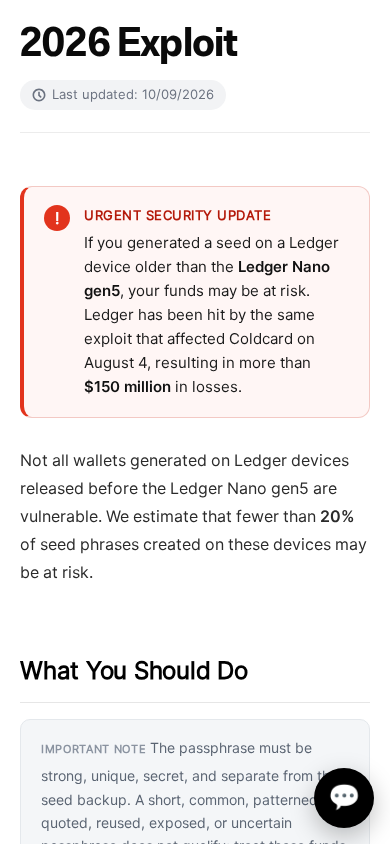
The website is an informational security-advisory site presenting itself as a Ledger hardware-wallet communication. It warns about a purported seed-generation vulnerability affecting older Ledger devices, provides firmware-update and fund-migration guidance, and links visitors toward hardware products, support, downloads, and related services.
Scam/Impersonation Risk
No confirmed blacklist, phishing, impersonation, or conflicting-identity finding was supplied, so no direct contradiction was observed. However, the site carries a material external reputation signal: one major security vendor classified the domain as malicious, although this does not constitute a confirmed blacklist finding. The advisory uses urgent language, cites more than $150 million in losses, estimates that fewer than 20% of affected seed phrases may be vulnerable, and promotes a browser-based seed-checking process. Those claims concern highly sensitive cryptocurrency credentials and create a meaningful social-engineering exposure even though the page states that checks occur locally and that seed phrases are not uploaded. The page analysis found no login form, sensitive-input form, wallet connection, or wallet-drainer behavior.
- Homepage: The page is titled “Scams Targeting Crypto Holders” and presents an urgent 2026 Ledger security advisory concerning older devices.
- Homepage: The advisory claims more than $150 million in losses and estimates that fewer than 20% of relevant seed phrases may be at risk.
- External reputation observation: One evaluated security vendor flagged the domain as malicious; blacklist and Google Safe Browsing findings were not present.
- Domain registration: Registered 2026, approximately 0.02 years old; creation date 2026-10-10T12:15:14Z and expiry date 2027-10-10T12:15:14Z.
- Archive records: 3 snapshots spanning 2025-04-17T04:35:22Z to 2026-10-10T12:53:11Z, covering 2 years; the records show no supplied repurposing conflict.
Regulatory Verification Notes
The apparent business model is a hardware-wallet vendor providing devices, accessories, enterprise solutions, support, downloads, and developer resources. The reviewed content is professionally structured as a security advisory, but the available evidence does not independently verify the operator behind the Ledger-related presentation. The reviewed page does not establish a legal entity, licensing authority, or registration number, leaving a material disclosure gap for any commercial or financial engagement. A separate broker-reputation dataset produced no match; that is contextual only and does not establish licensing or regulatory standing.
- Homepage: The stated commercial context is hardware-wallet sales and related support, enterprise, download, and developer services.
- Hosting telemetry: Served from AS13335, CLOUDFLARENET - Cloudflare, Inc., US.
- Transport telemetry: TLS certificate issued by YE1 with DV validation, valid to 2027-01-08T11:18:53+00:00.
- Registration telemetry: Registrar identified as NICENIC INTERNATIONAL GROUP CO., LIMITED; the supplied page evidence contains no licensing authority or registration number.
What to Verify Next
Before any sensitive interaction, an independent official Ledger channel should be used to confirm that the advisory, domain, security claims, and any associated seed-checking tool are genuine. The operator’s legal identity, applicable consumer terms, sales entity, returns process, and payment protections should be confirmed through independently obtained records rather than links or contact details presented by the site. Any request to enter, disclose, migrate, or replace wallet credentials should be validated through an offline or independently sourced support route.
- Homepage: The advisory directs users toward product and support resources while discussing seed replacement and fund migration.
- Homepage: The page states that seed checks are performed locally in the browser and that seed phrases are not sent to or stored on the site; this claim should be validated independently before sensitive use.
- Behavioral observation: Three successful page runs recorded no hidden forms, external password submissions, wallet-provider detection, clipboard hijacking, or wallet-drainer execution.
Summary Verdict
The overall posture is low trust with sensitive-interaction risk. The site presents coherent corporate-style advisory content and no confirmed contradiction, but the operator identity is unverified and the external malicious classification materially weakens confidence in the site as a safe destination for sensitive activity.
Infrastructure Integrity
Cloudflare CDN/WAF protection provides a mitigating layer, and all observed addresses were CDN edge servers rather than identifiable origin infrastructure. This supports transport and availability resilience but does not authenticate the publisher or validate the advisory’s claims.
Closing Assessment
Prospective users should limit initial activity to independently validated, read-only review and authenticate the publisher through an established offline or official channel before any login, credential, device, migration, or payment action.
Written analysis generated 2026-10-18 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by external reputation, hosting and network, history in the web archive, behaviour in a sandbox, page content.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Hosting and network
- The domain was registered less than three months ago.Hosting and network
rule:DNS_NEW_DOMAIN_90D - The domain is young and has almost nothing else set up around it.Hosting and network
rule:DNS_SPARSE_YOUNG_DOMAIN
03 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
04 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH
05 Page content
- The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of incident-ledger.com.
- The request stayed on incident-ledger.com. It was not redirected to another domain. Clear
- Registration is published under NICENIC INTERNATIONAL GROUP CO., LIMITED. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-10-10. Noted
- The earliest public archive of this site is from 2025-04-17. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3034::ac43:c312 |
| Name servers | CARLOS.NS.CLOUDFLARE.COM, DIVA.NS.CLOUDFLARE.COM |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2027-01-08 |
| Domain age | 0.02 years (continuous registration) |
| Domain expiry | 2027-10-10 |
| Archive first seen | 2025-04-17 |
| Archive snapshots | 3 |
| Reputation | VirusTotal: 1 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about incident-ledger.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.