Verdict
The site blocked our scan, so nothing was confirmed either way. Treat it as unknown and verify who runs it another way.
ixmeraauth.io blocked our automated scan and could not be verified.
- Needs Review: The site blocked or cut short the capture, so no verdict was reached.
| How the site describes itself | Interstitial human-verification challenge asking the visitor to type displayed characters and enter a code. No service, brand, or business content is visible. |
|---|
Evidence status and limitations
Evidence completeness: IncompleteThis says whether every check on the site was recorded as finished. The site blocked or cut short our capture, so the result needs review.
- The site showed automated visitors only a bot-protection challenge, so its own pages could not be read. The behaviour findings below measured that challenge page, not the site behind it.
- Capture was incomplete or blocked; this result requires review.
- The real-world operator identity was not independently verified.
At a glance
The checks that decide most of this verdict.
| Malware engines | 1 marked it maliciousVirusTotal; a single engine, not a confirmed listing | Watch |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 9 months oldRegistered 2026-02-21 | Watch |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by YE1 | Noted |
The page as captured
Key findings
- The site blocked automated access, so TrustSniffer could not collect enough evidence to assign a score.
Full analysis
Overview
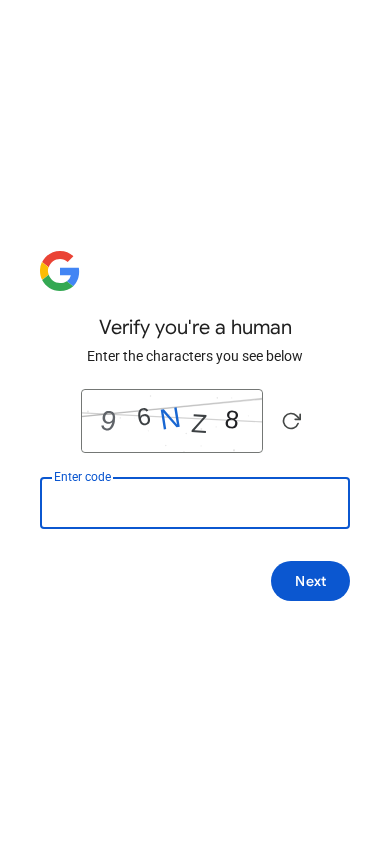
The website at ixmeraauth.io served a single human-verification page titled "Verify". It asked the visitor to type a short string of displayed characters (K, H, T, 2, 6) and enter a code before pressing "Next". The page shows no brand, product, service description or business content. It therefore presents no discernible purpose or business model beyond acting as a gatekeeping interstitial.
Scam/Impersonation Risk
No confirmed listing, phishing finding, brand impersonation or conflicting legal identity was observed, so no contradictions were found. One engine in an external malware-scanning aggregator flagged the domain as malicious. This is a soft third-party reputation note, and it is discounted because no leading vendor and no second source agreed, and Google Safe Browsing did not list the site. It remains an isolated, uncorroborated signal and not a confirmed listing. Separately, the page's structure matches that of two other verification-style hostnames that the analysis flagged. This resemblance is a scored negative finding, attributed to the page-structure comparison. It is discounted because it indicates a shared template and does not establish who operates any of the sites. The domain name suggests an authentication service, but the page offers nothing beyond the challenge itself, and no brand is claimed. Behavioural testing found no wallet-connection prompts, clipboard manipulation, hidden forms, cloaking or credential-harvesting behaviour. The only form on the page was the character challenge. The domain was registered recently. Together with the signals above, this calls for a measured assessment and does not support a confirmed-fraud conclusion.
- Registration record: the domain was registered on 2026-02-21, 262 days before capture.
- VirusTotal: 1 engine reported the domain as malicious and none as suspicious. No top-tier vendor was among them, and Google Safe Browsing did not list it. This is a soft, uncorroborated reputation note.
- Verification page: the one form seen was a character challenge, with no login, password or payment fields.
- Page-structure comparison: the page matched the template of two other verification-style hostnames flagged by the analysis. This is scored, but discounted because a shared template does not identify an operator.
Regulatory Verification Notes
The business type could not be determined. The page makes no licence claim and offers no financial or regulated service, so licensing is not at issue. Only the verification page was read. On the pages read, no named operator, company details, terms of use or privacy notice were found. The only identity-like text is the generic word "Verify". Identity checks rate a connection to a real-world brand or person as likely, with a score of 70 but low confidence (0.36). The evidence is consistent with such a connection, but it is not verified, and the thin text cannot independently tie the site to a particular business. The page content is thin, and that is a scored finding. It is attributed to the single page read, and it is discounted because that page is a challenge interstitial that would not be expected to carry business content. The domain's registration privacy is also a scored finding. It is attributed to the registration record, and it is discounted because privacy registration alone does not show who controls the domain or whether they have bad intent. The registrar named in the registration record is Global Domain Group LLC. No broker or regulator-style reputational record was matched, and none is implied.
- Verification page: the quoted claims are only "Verify you're a human" and "Enter the characters you see below". No company name, address or policy text was present on the page read.
- Registration record: registered through Global Domain Group LLC, with owner details under privacy registration.
- Hosting network: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: the TLS certificate was issued by YE1 (DV) and was valid until 2027-01-13.
What to Verify Next
The next steps depend on what sits behind the challenge. A visitor who arrived through a link should confirm independently, with the party that supplied it, that the link and the service it fronts are intended. After the challenge, the destination should be checked for a named operator, terms, a privacy notice and working contact routes before any information is shared. If the site later presents account, payment or file-download functions, those need fresh scrutiny, because none were present in this assessment.
- Verification page: it was the only page read, and no destination beyond the challenge was observed.
- Page behaviour: 21 console errors were recorded across 3 test runs. This is a scored finding, attributed to the behavioural test runs. It is discounted because no hostile page behaviour was observed alongside the errors.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Page behaviour: 12 requests went to other hosts, 3 of them to destinations TrustSniffer does not recognise. This is an observation and was not scored.
Summary Verdict
The site sits in a review-level posture. It shows no confirmed listing, no contradictory identity and no hostile page behaviour. Its content is also too sparse to demonstrate what it is, who runs it or why it exists. The evidence is consistent with a recently created, minimally populated verification page whose legitimacy remains undetermined, and it does not point to either an established service or a confirmed threat.
Infrastructure Integrity
All four addresses the domain resolved to were Cloudflare edge addresses, and no separate origin server was observed. The behavioural testing also detected bot-protection behaviour attributed to Cloudflare. The CDN is treated as neutral. It neither raises nor lowers the assessment and says nothing about who operates the site or what lies behind it. The domain also presented a valid DV certificate, which confirms encrypted transport and not the operator's identity.
Closing Assessment
Ordinary caution is appropriate. The page should not be treated as a trusted service until a named operator and a purpose have been established through an independent route. Any further step, particularly entering information beyond the displayed characters, should follow that confirmation.
Written analysis generated 2026-11-10 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by code shared with sites rated critical, page content, registration and ownership and behaviour in a sandbox.
01 Code shared with sites rated Critical
- The site runs the same code, or has code wired to the same hidden endpoint, as other sites TrustSniffer rated Critical.Code shared with sites rated Critical
rule:KIT_SHARED_WITH_CRITICAL_SITE
02 Page content
- The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN
03 Registration and ownership
- The registration record withholds contact details for the operator.Registration and ownership
rule:KF_WHOIS_HIDDEN
04 Behaviour in a sandbox
- The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH
Identity verification
| Status | LIKELY (NOT INDEPENDENTLY VERIFIED) |
|---|
What the page shows points to a real-world brand or person, but nothing was independently checked.
- org:Verify
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of ixmeraauth.io.
- The request stayed on ixmeraauth.io. It was not redirected to another domain. Clear
- Registered through Global Domain Group LLC. Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2027-02-21. Noted
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Global Domain Group LLC |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3036::6815:1917 (a CDN edge address; the server behind it was not observed) |
| Name servers | noah.ns.cloudflare.com, dana.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | YE1 |
| SSL expiry | 2027-01-13 |
| Domain age | 262 days (registered 2026-02-21) |
| Domain expiry | 2027-02-21 |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 1 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about ixmeraauth.io at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.