Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
kinetiq-en.firebaseapp.com shows high-risk / scam indicators.
| What this site appears to be | Kinetiq is a liquid staking and perpetual futures platform on Hyperliquid. It advertises kHYPE staking with a 1.98% APY, eight security audits, a $1M bug bounty, and institutional staking rails, but the captured text shows no legal entity or contact address. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 3 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 4% confidenceAbuseIPDB, 4 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Web archive | Never archivedNo public history of this site | Watch |
| Certificate | Encrypted connectionIssued by WR4 | Noted |
The page as captured
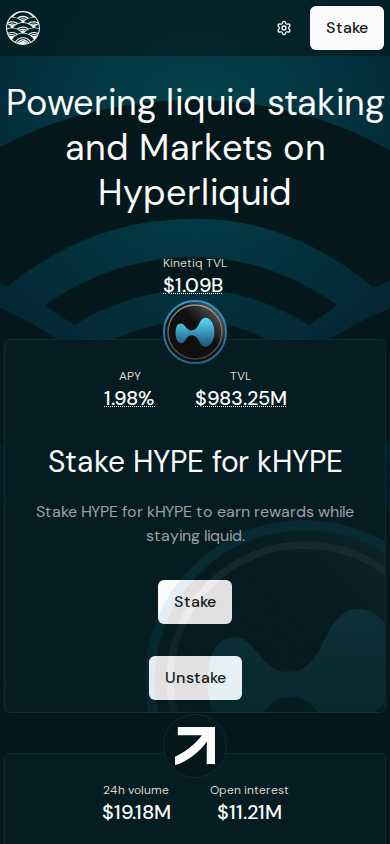
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
The website presents itself as Kinetiq, a liquid-staking and perpetual-futures platform for the Hyperliquid ecosystem. Visitors are invited to stake HYPE in exchange for the liquid token kHYPE, trade perpetual futures markets, and explore an institutional staking product. It is served from a free Google Firebase-hosted subdomain rather than a dedicated domain. Its apparent business model is yield and fee generation from deposited crypto assets, but the page does not disclose fee rates, the reward split, or the revenue mechanism.
Scam/Impersonation Risk
Hard contradictory signals are present. Multiple threat-intelligence engines flag this address as malicious or suspicious, and it also appears on an external blacklist. This is the decisive factor in the assessment, and the site's infrastructure and polished content cannot offset it. The hosting arrangement adds to the concern. The site runs on a generic, free application-hosting subdomain with an "-en" suffix, not on a dedicated domain controlled by the project. Anyone can register this pattern for a lookalike of a known brand, so it fits a mirror or clone of a legitimate project. The analysis did not confirm brand impersonation, and no conflicting legal identities were found, but the blacklist and hosting pattern together call for a security-forward reading. The homepage product claims raise the stakes for a deposit-first flow. It advertises a 1.98% APY on kHYPE staking, perpetual futures on equities, indices, currencies and commodities "24/7/365", and an institutional product (iHYPE) described as "compliant" and "custody-integrated". It also shows large credibility cues: a headline TVL of $1.09B, a second and different TVL of $983.25M, 24-hour volume of $19.18M, open interest of $11.21M, "eight" security audits, and a "$1M" bug bounty described as "the largest on Hyperliquid". None of these figures link to verifiable evidence on the captured page. The two inconsistent TVL values on one screen are a data-integrity concern. Automated browsing found no wallet-connection prompts, hidden forms, clipboard manipulation or drainer behaviour. It did observe repeated outbound POST traffic and a final-destination mismatch, flagged as suspicious network behaviour. Users deposit assets before receiving any service, and the token set (HYPE, kHYPE, KNTQ, iHYPE, kStake) is the kind of surface on which counterfeit staking interfaces typically operate. A small number of abuse reports on the shared edge address are recorded. They apply to shared provider infrastructure and say little about this site on their own, so they are a soft reputational signal and not part of the blacklist finding. Evidence:
- Homepage: staking and trading calls to action, a 1.98% APY, a $1.09B headline TVL beside a conflicting $983.25M TVL, and the eight-audit and $1M bug-bounty claims, none of them supported by verifiable references.
- Domain: the site is served from a free Firebase application-hosting subdomain with an "-en" suffix, not from a project-owned domain.
- Behavioural analysis: three of three sandbox runs loaded successfully; no wallet-connect or drainer activity, but external POST traffic and a final-destination mismatch were flagged.
- External reputation: multiple security engines report malicious or suspicious verdicts, and an independent blacklist listing is active.
Regulatory Verification Notes
The homepage shows no legal entity, registered company, business address, or licence. This is a disclosure gap in its own right, and it undercuts the institutional claim for iHYPE, a product marketed to "regulated entities and enterprises" as compliant. No regulator, registry number or custodian is named to support that wording. The site has no terms, privacy, risk-disclosure or about page in the captured content. Identity could not be independently tied to a real-world brand or person, and the available evidence does not establish who operates this deployment or whether it is the genuine project. The missing disclosures matter more here than they would on an otherwise clean site, because they sit alongside the active threat listing and a product that takes custody of user funds. No third-party broker-review match exists, so no broker-reputation signal applies. The security posture of the transport layer is adequate but offers no assurance of legitimacy. Evidence:
- Homepage: no legal entity, company registration, address, licence number, or regulator reference appears anywhere in the captured text.
- Homepage: the iHYPE institutional product is described as "compliant" and "custody-integrated" with no named regulator, custodian or registry.
- Hosting: served from AS54113 (Fastly, Inc., US), with only edge addresses observed.
- Transport encryption: TLS certificate issued by WR4 at domain-validated (DV) level, valid to 2026-12-22. DV certification confirms control of the hostname only, not the operator's identity.
What to Verify Next
Before any interaction, confirm independently whether this address is an official property of the Kinetiq project. Use only links published on a project channel reached through a route not originating from this site, such as the project's documented social profiles, or a reputable protocol aggregator cross-checked against several sources. Compare the staking contract addresses, the token addresses for kHYPE, KNTQ and iHYPE, and the stated TVL and APY against the project's on-chain data and its published audit reports. Confirm the audits and the bug-bounty programme directly on the auditors' and the bounty platform's own pages. Request the operating entity's registration and any claimed regulatory status from the project's official channels. Treat any prompt for a wallet signature, token approval or seed phrase from this address as unverified until all of these checks pass. Evidence:
- Homepage: the "View audits" and "View bug bounty program" prompts need confirmation at the auditors' and bounty platform's own pages, since the claims are unsupported on-site.
- Homepage: the staking and token details need comparison against independently sourced on-chain records.
- Homepage: the conflicting TVL figures should be reconciled against an independent analytics source.
Summary Verdict
The assessment is elevated risk with a cautionary posture. Active third-party threat detections and an unverified operator override an otherwise professional presentation and clean behavioural testing. The site is best regarded as a potentially hostile or counterfeit deployment of a staking product until its link to the genuine project is established. It cannot be treated as an established or reliable counterparty.
Infrastructure Integrity
The site is delivered through Fastly's content-delivery network, and every observed address belongs to its edge servers. The origin hosting could not be observed, so the actual host cannot be independently verified, and content can be swapped behind the edge without visible change. The edge provides a protective layer and the delivery appears stable, but this is a mitigating factor only. It does not indicate legitimacy and cannot offset the reputational findings.
Closing Assessment
Users should not log in, connect a wallet, approve token spending, stake, trade or deposit funds through this address, and should treat it as read-only at most. Anyone who has already interacted with it should review and revoke wallet approvals and move assets to a fresh wallet. Operators or partners of the genuine project should consider reporting it as a suspected lookalike for takedown.
Written analysis generated 2026-10-20 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, behaviour in a sandbox.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META
03 Behaviour in a sandbox
- A large share of what the page loaded came from other domains.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_MODERATE - Many of the responses the page received looked generated rather than served normally.Behaviour in a sandbox
rule:BEHAV_SYNTHETIC_RESPONSES_HIGH
Signals weighed against the site
- AbuseIPDB: 4 reports on hosting IP 2620:0:890::100 (Google LLC, Content Delivery Network), 4% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of kinetiq-en.firebaseapp.com.
- The request stayed on kinetiq-en.firebaseapp.com. It was not redirected to another domain. Clear
- It is hosted on FASTLY, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | FASTLY - Fastly, Inc., US |
| Country | US |
| Server IP | 2620:0:890::100 |
| Name servers | Not available |
| CDN / edge network | Detected (fastly) |
| Resolved IP addresses | 2 |
| Edge IP addresses | 2 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR4 |
| SSL expiry | 2026-12-22 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | 0 |
| Reputation | VirusTotal: 3 flagged | AbuseIPDB: 4% confidence, 4 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about kinetiq-en.firebaseapp.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.