Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
littlepepelive.pages.dev shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: as a site on pages.dev, this address has no registration record of its own (the platform's domain is registered, not the site). That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
| How the site describes itself | Presale page for the LILPEPE token of a claimed Layer 2 EVM meme-coin chain. Visitors connect a crypto wallet and buy tokens in escalating stages, with tokens claimable only after the presale ends. The page relies on price-growth promises, urgency and a giveaway, while the legal entity, team, full contract address and audit details are not verifiable from the page. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-11-01 and re-scored on 2026-11-05. The certificate, the registration age and the page content describe the site as it was on 2026-11-01.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | 3 marked it maliciousVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| First seen | 5 months before captureWeb archive; a site on pages.dev has no registration of its own | Risk |
| Web archive | Archived since 20262 snapshots; the archive has almost no record of this site, which counted against it | Watch |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- First seen: less than 1 year before capture (web archive; a site on pages.dev has no registration of its own).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Overview
This website is a single-page cryptocurrency token presale for "LILPEPE" (Little Pepe), which describes itself as a meme-themed, low-fee Layer 2 EVM blockchain. It invites visitors to connect a crypto wallet and buy tokens in escalating price stages with ETH, USDT or card. Tokens are claimable only after the presale closes, so the business model is advance payment in return for a promised future asset.
Scam/Impersonation Risk
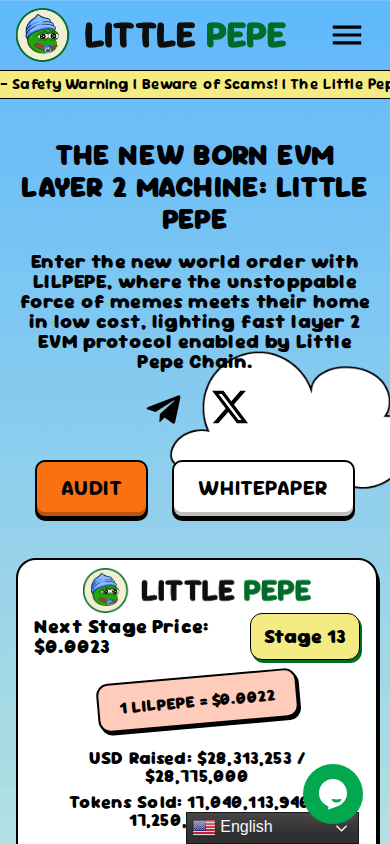
Active contradictions are present. Reputation sources have flagged the site, and the combined detections amount to a confirmed blacklisting. Protective infrastructure and a valid certificate do not offset this. The presale mechanics also fit a high-risk pattern. The page shows "Stage 13" pricing of $0.0022 per token, with the next stage at $0.0023. It reports roughly $28.3 million of a $28.775 million target raised and 98.78% of tokens sold, which creates urgency. It adds a "+777k Giveaway" and growth claims such as "1 BILLION MCAP or bust", "Hits TOP 100 CMC" and "Listed on Top Exchanges". None of these claims is backed by anything a visitor can check. The token contract address appears only in truncated form ("0xdd...0315"). The audit and whitepaper are presented as links without substantiating detail. No team or recipient of funds is named. The page's own safety banner tells visitors to verify official links only through a different, standalone domain. Yet the page itself is served from a free shared-platform subdomain with a name closely resembling that brand. This mismatch is unresolved. No brand impersonation or conflicting legal identities were confirmed, but the claim-versus-evidence gap and the payment-first structure are decisive. Scam-warning text and a disclaimer on the page do not change this.
- Homepage: the presale widget shows Stage 13 pricing, the funds-raised and tokens-sold counters, and the giveaway banner alongside the unsubstantiated "Top 100" and "Listed on Top Exchanges" claims.
- Homepage: the contract address is shown only in truncated form, and no named team or fund recipient appears.
- Homepage safety banner: names a separate domain as the only official source, while the page is served from a shared hosting subdomain.
- Domain provenance: the domain is about 138 days old (~0.4 years), and the web archive holds only 2 snapshots, from 2026-06-16 to 2026-07-04 (1 year tracked).
Regulatory Verification Notes
The site claims no license, registration or regulatory authority, and no third-party regulatory source corroborates one. The homepage names no legal entity, registered address, directors or operating team. Together with the unclear ownership, this is a governance and ownership opacity problem. For a token sale that takes payments from the public, it is a material shortfall against the disclosure a financial counterparty would require. The absence of a licence is a transparency gap rather than proof of wrongdoing, but here it sits alongside confirmed reputation detections. No matched broker-reputation record exists for this project, so there is no independent third-party standing to weigh. The site's transport encryption is a domain-validated certificate. It confirms an encrypted connection but says nothing about who operates the site.
- Homepage and navigation (About Us, Roadmap, Tokenomics, Dashboard, Contact Us): none discloses a legal entity, licence, or registered address.
- Hosting infrastructure: served from AS13335 (Cloudflare, Inc., US).
- Transport encryption: TLS certificate issued by WE1 (DV), valid to 2027-01-29.A TLS certificate is what puts the padlock and https:// in your browser and encrypts the connection. "WE1" is the name of the authority that issued it. DV (domain validated) means the issuer only confirmed who controls the domain name, not which person or company runs the site. "Valid to" is the date it expires.
- Page content: wallet-connect and network-switch prompts are triggered on load, and the legal status of the token sale cannot be verified from the page.
What to Verify Next
Independent confirmation should be obtained before any interaction, and it must come from sources other than this page. The full token contract address should be checked on a public blockchain explorer, covering deployer, holder concentration and any transfer restrictions. Any audit should be obtained directly from the named auditor and matched to that exact contract. The claimed exchange listings and market-ranking milestones should be checked against the listing venues themselves. Official project channels should be confirmed through an independent route, not through links on this page. The legal entity behind the sale should be identified and checked with the relevant securities or financial regulator in the buyer's jurisdiction.
- Homepage: the audit and whitepaper links are offered without any identified auditor or author.
- Homepage: the listing and ranking claims are made without any named exchange or dated milestone.
- Homepage: the project's official domain is asserted in the safety banner but not demonstrated by the page's own address.
Summary Verdict
The assessment is clearly adverse. Confirmed reputation detections combine with a payment-first, claim-heavy presale structure and no verifiable operator to place the site in an elevated-risk category. Its trust standing is critical, and nothing in the evidence supports treating it as a legitimate counterparty at present.
Infrastructure Integrity
The site sits behind Cloudflare's CDN and web application firewall. All observed addresses are edge servers, and the origin server was not observable, which limits independent verification of the hosting and means content could be swapped quickly. This is the only mitigating infrastructure signal, and the infrastructure was assessed as sound. It describes the delivery layer, not the operator, and it cannot offset the reputational detections.
Closing Assessment
The site should not be used for any financial or credential interaction. Visitors should not connect a wallet, approve transactions, or send ETH, USDT or card payments. Any use should be limited to read-only viewing. Anyone who has already interacted should revoke wallet approvals and move assets to a fresh wallet.
Written analysis generated 2026-11-05 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by external reputation, page content and history in the web archive.
01 External reputation
- Three or more VirusTotal engines, or two including a leading vendor, marked this domain as malicious.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED
03 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking. Any operator the page names in its own words (see how the site describes itself, above) is not verified here.
What TrustSniffer observed
First-party facts recorded during the assessment of littlepepelive.pages.dev.
- The request stayed on littlepepelive.pages.dev. It was not redirected to another domain. Clear
- The earliest public archive of this site is from 2026-06-16. Watch
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:310c::ac42:2ce8 (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-29 |
| First seen (web archive) | 138 days before capture; a site on pages.dev has no registration of its own |
| Domain expiry | Not available |
| Archive first seen | 2026-06-16 (138 days before capture) |
| Archive snapshots | 2 |
| Reputation | VirusTotal: 3 malicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about littlepepelive.pages.dev at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.