Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
neoclaimhub.com shows high-risk / scam indicators.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 12 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Listed as unsafeGoogle | Risk |
| Abuse reports on the host | 37% confidenceAbuseIPDB, 50 reports; shared hosting inflates reports | Clear |
| Domain age | 4 months oldMost scam domains are under a year old | Risk |
| Certificate | Encrypted connectionIssued by YR2 | Noted |
| Hosted by | PONYNETServer in US | Noted |
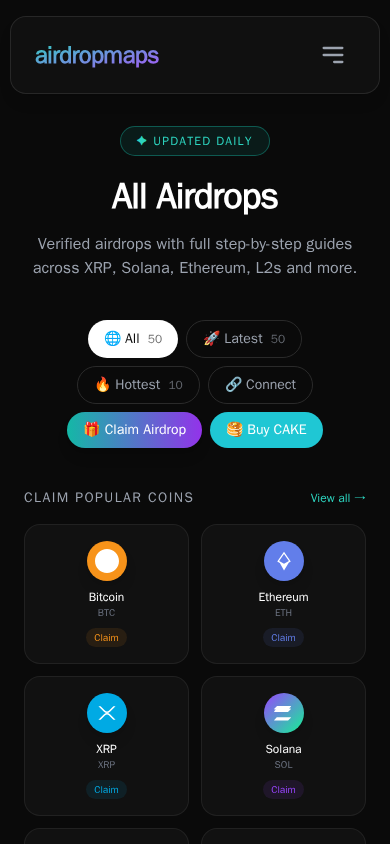
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Google, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
This website presents itself as a crypto-airdrop information and claim portal. Its homepage is titled "Airdrops | airdropmaps", while the domain name, neoclaimhub, points to token claiming. It appears to rely on the promise of free token distributions to draw visitors toward claim actions. Automated analysis of the page content did not complete, so the operator behind it is not independently identified.
Scam/Impersonation Risk
Contradictory signals are present and are the decisive factor in this assessment. A major browser safe-browsing service classifies the domain under its social-engineering category, which covers phishing-style deception. A substantial group of independent security engines also rates the domain malicious, and several more rate it suspicious. The combined picture is a confirmed blacklisting across independent sources. That fits the pattern of airdrop-claim lures, where visitors are pushed to "claim" tokens as a pretext for connecting a wallet or surrendering credentials. A domain name built around "claim" and a page headline about airdrops that do not match each other reinforce that reading. The sandbox sessions did not observe wallet-connection prompts, clipboard manipulation, hidden forms, credential posts to third parties, or content cloaking. Those results are a limited mitigating observation, because a lure page can stay passive until a visitor engages. No conflicting legal identities or direct impersonation of a named brand were found. The risk rests on the external threat detections. Evidence:
- Homepage: the page is titled "Airdrops | airdropmaps", a title that differs from the domain's own naming.
- A browser safe-browsing service flags the domain for social engineering. 12 security engines rate it malicious and 3 suspicious.
- Domain registered 2026-07-09 (~0.3 years, about 109 days old). Very young domains are common among short-lived lure campaigns.
- Behavioral sandbox, 3 of 3 runs successful: no wallet-connect, clipboard-write or hidden-form activity, and no external XHR or POST traffic.
Regulatory Verification Notes
The site discloses no regulatory status, licence, or corporate registration that can be matched to a legal entity. The domain's registration details are incomplete, which amounts to ownership opacity. That opacity is an administrative limitation and not an identity contradiction. A claim-and-distribution service that handles digital assets would normally be expected to name an accountable operator, and none could be tied to this site. The registrar is established, but registrar choice does not establish who operates the site. No third-party broker or regulatory-database match was found. The absence of one is neutral, but it means nothing offsets the threat findings. Evidence:
- Domain registered through Gransy, s.r.o., created 2026-07-09 and expiring 2027-07-09.
- Served from AS53667 (PONYNET – FranTech Solutions, US).
- TLS certificate issued by YR2 (DV, domain-validated only), valid to 2026-12-17 with 50 days remaining. DV encryption confirms control of the domain, not the operator's identity.
- No match in the DeFiLlama protocol directory, so no recognised DeFi project stands behind the domain.
What to Verify Next
Any airdrop the site claims to offer should be checked against the announcements of the token project it refers to. Those announcements should be reached through an independently sourced official channel, never through links on this site. Visitors should confirm the contact channels of any project that appears to be distributing tokens through a route found independently of this domain. If a legal entity is later named, its existence and any licence should be checked directly with the relevant registry. Anyone who has already interacted with the site should review wallet approvals and revoke any that are unfamiliar. They should also change credentials entered on the site and move assets to a fresh wallet if there is any doubt. Evidence:
- Homepage: the airdrop theme and claim-oriented domain name are the specific claims to check against official project announcements.
- No on-site legal entity or licence reference was identified to validate against a registry.
- The safe-browsing social-engineering classification is the basis for treating any wallet or credential interaction as potentially compromised.
Summary Verdict
The overall posture is high risk. Independent threat detections, a very recent registration, and the absence of any verifiable operator outweigh the technically valid encryption and the passive behaviour seen in testing. The site cannot be treated as legitimate, and its apparent purpose is consistent with a social-engineering lure rather than a genuine airdrop service.
Infrastructure Integrity
The site is hosted on a single IP address within the FranTech Solutions network (AS53667, US). No CDN or WAF layer was detected, so the origin server is directly exposed and no protective infrastructure mitigates the threat findings. About 50 abuse reports have been filed against that IP address, with the most recent only days ago. These reports apply to a hosting provider's shared address space and cannot be attributed to this domain alone. They still add a reputational burden to the hosting context. Valid TLS certificate chains are present but do not offset this.
Closing Assessment
The site should not be used for anything beyond passive viewing, and wallets, credentials, and payment details should stay out of any interaction with it. Nothing should be downloaded from it, and its claim flows should be avoided entirely.
Written analysis generated 2026-10-27 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
4 findings contributed to this verdict, raised by external reputation, behaviour in a sandbox, hosting and network, registration and ownership.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Behaviour in a sandbox
- Most of what the page loaded came from other domains rather than from this one.Behaviour in a sandbox
rule:BEHAV_EXTERNAL_RATIO_HIGH - The structure of the page changed sharply while it was loading.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE
03 Hosting and network
- The domain was registered between three and six months ago.Hosting and network
rule:DNS_YOUNG_6M
04 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Signals weighed against the site
- AbuseIPDB: 50 reports on hosting IP 198.251.89.30 (FranTech Solutions, Content Delivery Network), 37% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of neoclaimhub.com.
- The request stayed on neoclaimhub.com. It was not redirected to another domain. Clear
- Registration is published under Gransy, s.r.o.. Clear
- DNS for this domain is served by asurahosting.com, across 2 name servers. Noted
- The registration is paid up to 2027-07-09. Noted
- It is hosted on PONYNET, from a server in US. Noted
Domain intelligence
| Registrar | Gransy, s.r.o. |
|---|---|
| Hosting | PONYNET - FranTech Solutions, US |
| Country | US |
| Server IP | 198.251.89.30 |
| Name servers | NS23.ASURAHOSTING.COM, NS24.ASURAHOSTING.COM |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR2 |
| SSL expiry | 2026-12-17 |
| Domain age | 0.30 years (continuous registration) |
| Domain expiry | 2027-07-09 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 12 flagged | AbuseIPDB: 37% confidence, 50 reports | Google Safe Browsing: 1 match |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about neoclaimhub.com at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.