Verdict
The site's own pages showed several warning signs that deceptive sites commonly use, and together with the other checks they put it in the critical-risk band. Do not pay, sign in, or share personal details with this site.
oakslog.com shows critical-risk indicators.
- Sensitive Interaction Risk: The overall risk is high enough that entering private details here (a password, card number or wallet recovery phrase) could be unsafe.
- Governance Risk: An ownership check raised a concern: the site asks visitors to sign in while its operator could not be verified and the registration lookup did not return the domain's registrant and country. On its own this does not say who runs the site or that anything is wrong with it.
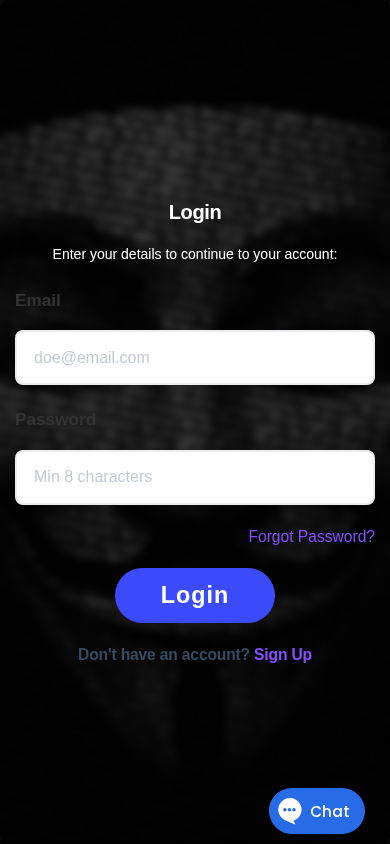
| How the site describes itself | Login page of a shop that advertises 'Legit Bank Logs', shop scripts and webmail access, with a sign-up page linked. No legal identity, contact, address or policy is disclosed, and the offer is for stolen account data. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-11-10 and re-scored on 2026-11-16. The certificate, the registration age and the page content describe the site as it was on 2026-11-10.
- The real-world operator identity was not independently verified.
- These checks returned no result: web archive lookup.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 2/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| Malware engines | None malicious; 1 marked it suspiciousVirusTotal | Watch |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 1 report; shared hosting inflates reports | Clear |
| Domain age | 3 months oldRegistered 2026-07-29 | Risk |
| Certificate | Encrypted connectionIssued by YR1 | Noted |
| Hosted by | PONYNETNetwork registered in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2026-07-29).
- No security engine marked this domain as malicious and Google Safe Browsing does not list it; some engines marked it suspicious, which TrustSniffer does not count as a listing. Its hosting IP carries AbuseIPDB reports below the confidence level TrustSniffer treats as a flag.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
Oaklogs, served from the domain oakslog.com, is a login-gated storefront whose homepage title advertises "Get Legit Bank Logs, Shopwithscripts, webmails and mant more" (quoted as written, including the typo). A visitor sees only an email-and-password sign-in form, a "Forgot Password?" link and a sign-up route that opens a registration form headed "Create an Account". The business model is the sale of stolen banking access data, shop scripts and webmail credentials to registered account holders. The site offers no product description, price list or fulfilment terms.
Scam/Impersonation Risk: The site's own homepage offers stolen bank account data for sale, and this is the decisive finding. The "bank logs" it advertises are, by the site's own framing, illicit banking access credentials, and the adjoining offers of webmail access and shop scripts belong to the same trade. Buying such goods is a crime in most jurisdictions. Shops of this kind commonly take payment and deliver nothing, or deliver data that has already been revoked. The report rates this as critical risk. No brand impersonation was detected, no conflicting legal identities appear, and Google Safe Browsing did not list the site. One security engine rated it suspicious but did not flag it as malicious. That is not a detection, and the assessment does not rest on it. The sign-in and registration pages are the entry points to the marketplace, and they collect email addresses and passwords, so any credentials typed into them would go to an operator who cannot be identified.
Regulatory Verification Notes: On the two pages read (the homepage and the registration page), no legal entity, licence, physical address, contact channel, terms of service or privacy policy is disclosed. A business selling stolen credentials cannot lawfully hold any registration or licence. The missing disclosures are therefore not a transparency gap that a licence check could resolve. The only identity the site offers is the brand label "Oaklogs", which is a claim and not a verified operator. The registration lookup lacked the registrant and country fields, and the absence of registrant details is a scored finding. No third-party broker or regulatory source references the site.
What to Verify Next: Verification of the operator is not a useful step for this site, because the offer is unlawful on its face. The practical steps concern response and exposure. A person who was directed to the site, for instance through a message or forum post, should treat the source of that referral as compromised or malicious and report it. A bank, payment provider or email host that suspects its customers' data is being traded should check its own fraud-monitoring and credential-reset records, not engage with the storefront. A relevant national cybercrime or fraud-reporting body is the appropriate recipient of a report about the site's content. The hosting provider's abuse desk is a secondary route.
Summary Verdict: The site is assessed at critical risk. Its stated purpose is the sale of stolen financial and account access data. It is a new, anonymous storefront with no accountable operator, and no evidence in the record offsets that purpose. The posture is unsuitable for any interaction beyond documentation.
Infrastructure Integrity: The site resolves to a single origin address on a commercial hosting network in the United States, with no CDN or edge layer observed. The absence of a CDN is neutral and is neither a mitigating factor nor a source of exposure. One abuse report exists against the host address. It belongs to the provider's shared address and was discounted, so it is not attributed to this site.
Closing Assessment: The site should not be used. No account should be registered, no email address or password entered, and nothing purchased. Anyone who has already entered credentials there should change them on every service where they are reused, and should alert the affected provider.
- Homepage: the title and visible text advertise "Legit Bank Logs, Shopwithscripts, webmails and mant more" directly beside a login form. No description of the goods, prices or delivery appears on the pages read.
- Registration page: the "Create an Account" form asks visitors for an email and password to "get started", and no policy or operator information accompanies it.
- Registration record: the domain was registered on 2026-07-29, which was 104 days before capture.
- Behaviour capture of the homepage: 192 console errors were recorded across three runs, which is a scored finding.A console error is a technical error message that the page's own code reported inside the browser while it ran. It describes how the page is built, and on its own it is not proof that the site is harmful.
- Homepage and registration page: neither lists contact details, a postal address, terms or a privacy policy on the pages read.
- Registration record: registered through Gransy, s.r.o. on 2026-07-29 with expiry on 2027-07-29. The registrant and country fields were absent.
- Hosting: the site is served from AS53667 (PONYNET - FranTech Solutions, US).
- Transport encryption: the certificate seen at capture was a domain-validated certificate issued by YR1 and valid to 2026-12-27. Encryption protects the connection only and says nothing about the operator.
- Homepage: the stolen-data offer is visible without logging in, so the content can be documented and reported from the public page alone.
- Registration record: the domain is registered through Gransy, s.r.o., a possible route for an abuse report.
- Hosting infrastructure: the site is hosted on FranTech Solutions infrastructure, a possible route for a hosting abuse report.
Written analysis generated 2026-11-16 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
11 findings contributed to this verdict, raised by page content, several checks together, hosting and network, behaviour in a sandbox, and registration and ownership.
01 Page content
- The review of the page content rated it high risk.Page content
rule:PAGE_RISK_HIGH - The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page has very little readable content.Page content
rule:PAGE_CONTENT_THIN - The page presents a sign-in form, and the operator behind it could not be independently verified.Page content
rule:PAGE_TYPE_LOGIN_UNVERIFIED
02 Several checks together
- No external threat source confirms a listing for this site, but its own page content reads as risky.Several checks together
rule:HYB_POSITIVE_EXTERNAL_NEGATIVE_PAGE
03 Hosting and network
- The domain was registered, or a site on a hosting platform was first seen, three to six months before capture.Hosting and network
rule:DNS_YOUNG_6M
04 Behaviour in a sandbox
- The page produced an unusually high number of errors while it ran.Behaviour in a sandbox
rule:BEHAV_CONSOLE_ERRORS_HIGH - The page showed a password field during the sandbox session, and it could not be matched to a recognised brand's sign-in page.Behaviour in a sandbox
rule:BEHAV_PASSWORD_FORM_PRESENT
05 Registration and ownership
- The security certificate only proves control of the domain, not who operates it.Registration and ownership
rule:KF_SSL_DV_ONLY - The registration lookup did not return the domain's registrant and country.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Page quality: 2 findings share one limit, because each is weak evidence on its own. Together they stayed under the limit.
Noted, not counted
Recorded during the assessment, but not counted against the site.
- AbuseIPDB: 1 report on hosting IP 198.251.83.106 (PONYNET), 0% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- org:Oaklogs
- contact:form
- on_site_identity
What TrustSniffer observed
First-party facts recorded during the assessment of oakslog.com.
- The request stayed on oakslog.com. It was not redirected to another domain. Clear
- Registered through Gransy, s.r.o. Noted
- DNS for this domain is served by my-control-panel.com, across 2 name servers. Noted
- The domain is registered until 2027-07-29. Noted
- It is hosted on PONYNET, a network registered in US. Noted
Domain intelligence
| Registrar | Gransy, s.r.o. |
|---|---|
| Hosting | PONYNET - FranTech Solutions |
| Network registered in | US |
| Server IP | 198.251.83.106 |
| Name servers | ns25.my-control-panel.com, ns26.my-control-panel.com |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR1 |
| SSL expiry | 2026-12-27 |
| Domain age | 104 days (registered 2026-07-29) |
| Domain expiry | 2027-07-29 |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 0 malicious, 1 suspicious | AbuseIPDB: 0% confidence, 1 report | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about oakslog.com at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.