Verdict
When the evidence was captured, Cloudflare showed its own warning page in place of this site, and external threat listings named it as malicious. Do not pay or share personal details with this site.
pandupanda.app shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: A registration check came back incomplete: the registration lookup did not return the domain's registrant and country. That is a gap in what could be looked up, not a sign that ownership is hidden, and it does not say who runs the site.
| What the captured page showed | A Cloudflare interstitial reports the requested site as suspected phishing and withholds its content, so the site's purpose, identity, and business model cannot be verified. |
|---|
Evidence status and limitations
Evidence completeness: CompleteThis says whether every check on the site was recorded as finished. All of them were.
- The evidence was captured on 2026-11-10 and re-scored on 2026-11-11. The certificate, the registration age and the page content describe the site as it was on 2026-11-10.
- External threat sources confirmed a listing for this site when the evidence was captured (VirusTotal, a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-26)). It was not re-queried for this version. On its own it would limit the score to at most 24; the score is lower because of the other findings below.
- When captured, this address served Cloudflare's own warning page instead of the site, so the site's own content was not captured; Cloudflare's warning is itself the evidence.
- The real-world operator identity was not independently verified.
How to read these numbers
A trust score of 0 means the risk evidence outweighed every trust signal by more than the 0 to 100 scale can show. It rates the evidence found, not the probability that the site is a scam.
Evidence confidence (75%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | The findings belowThe confirmed external listing ceiling (at most 24) and the threat-listing ceiling (at most 5) also apply, but the findings brought the score lower. | Watch |
|---|---|---|
| Malware engines | 7 marked it malicious, 1 suspiciousVirusTotal; Fortinet, Sophos among the engines that flagged it | Risk |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | 11 months oldRegistered 2025-12-20 | Watch |
| Web archive | Archived since 20261 snapshot; the archive has almost no record of this site, which counted against it | Watch |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- Domain age: less than 1 year at capture (registered 2025-12-20).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain when the evidence was captured.
Full analysis
Security Alert
7 VirusTotal engines, including Fortinet, Sophos, marked this site as malicious; independent sources confirm a listing for this site.
Overview
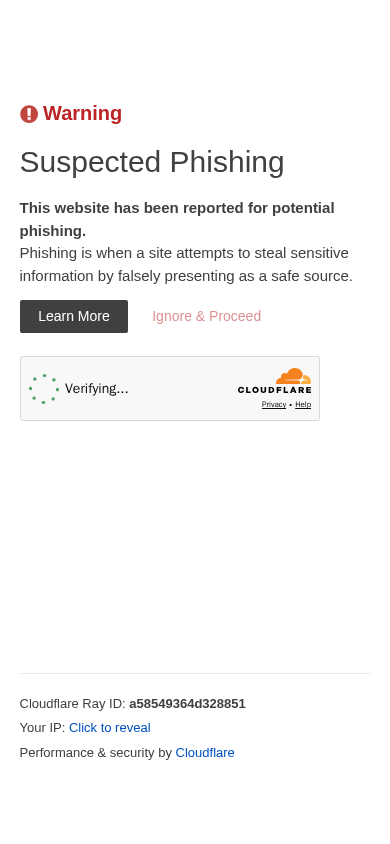
The website at pandupanda.app did not present any content of its own when it was captured. The automated capture returned a Cloudflare security interstitial headed "Suspected Phishing," which states that the site "has been reported for potential phishing" and defines phishing as a site that tries to steal sensitive information by falsely presenting as a safe source. The page is a third-party warning, not the operator's content. Its purpose, product, audience and business model therefore could not be established, and the page showed no offer, form or monetization of any kind.
Scam/Impersonation Risk
This assessment is at critical risk, and it rests on external threat intelligence rather than on anything the site's own pages showed. A threat-intelligence listing classes the domain as a phishing source and assigns it the role of actor, meaning the site itself is listed as the source of the activity. The listing was last seen on 26 October 2026. VirusTotal separately reported that 7 engines rated the domain malicious and 1 suspicious, including Fortinet and Sophos. These two independent sources align, so TrustSniffer treats the listing as a confirmed blacklist entry. Google Safe Browsing did not list the domain, and that check is the only one of its kind that was run. No brand impersonation was detected and no conflicting legal identities were found. The risk therefore comes from the phishing listings and the Cloudflare warning, not from an identity contradiction. The captured page showed no login or payment form.
- Homepage capture (10 November 2026): the page returned was Cloudflare's "Suspected Phishing" interstitial with an "Ignore & Proceed" option, and no site content was visible.
- VirusTotal: 7 engines malicious and 1 suspicious, with Fortinet and Sophos among the engines reporting malicious.
- Threat-intelligence listing: class phishing, role actor, last seen 2026-10-26.
Regulatory Verification Notes
The only page read was the homepage, and it was the Cloudflare warning. On the pages read, no contact channels, no terms or privacy statement, and no company or licence information were present, so the expected disclosures for a site of this type are all missing. No licence or regulatory registration is claimed anywhere in the evidence, and no regulator or third-party broker record links the domain to a supervised entity. The registration record lacks the registrant and country fields. TrustSniffer counts incomplete registration data as a scored finding. The real-world operator has not been independently connected to any person or brand. The domain was registered recently and the web archive holds only a single capture, so there is no long operating history to offset the listings. The valid certificate and clean abuse record at the host do not establish who runs the site.
- Registration record: domain registered 2025-12-20 (325 days old at capture) through NICENIC INTERNATIONAL GROUP CO., LIMITED, expiring 2026-12-20; registrant and country fields are missing.
- Web archive: 1 snapshot, first and last on 2026-02-16, a span of 0 days.
- Transport encryption: the certificate seen at capture was a DV certificate issued by WE1, valid until 2027-01-10. This shows encryption only, not operator identity.
- Homepage capture: no contact channels or terms/privacy content on the page read, which was the Cloudflare warning.
What to Verify Next
The page captured was Cloudflare's phishing warning, not the site itself, and the "Ignore & Proceed" option should not be used to bypass it. Anyone who was sent to this address should confirm the sender's identity through a channel that does not rely on the site, such as an offline or previously known route. Claims of a business, product or licence connected to the domain should be checked directly with the relevant registry and the named organization, because the captured page offered nothing to check against. Any later re-assessment should start from the current status of the phishing listing and the engine detections, not from this capture.
- Homepage capture: the page offered no operator name, licence number or contact route to check.
- Listings: the detections and the phishing listing were seen between 26 October and 10 November 2026.
Summary Verdict
The overall posture is critical risk. The domain is a recently registered, thinly archived and unattributed site that independent sources classify as phishing, and nothing in the evidence offsets those findings. Its apparent legitimacy is not supported by any verified operator identity.
Infrastructure Integrity
The domain resolves to Cloudflare (AS13335), a US-registered network, and all four observed IP addresses are Cloudflare edge addresses, with no origin server visible. This arrangement is neutral and says nothing about whether the site is legitimate. The host address's abuse record was checked and showed no reports, which is a neutral finding that does not offset the phishing listings. The Cloudflare warning page was served from this same infrastructure.
Closing Assessment
The site should be treated as critical risk. It should not be visited, relied on or engaged with, and any message, advertisement or contact that directs someone to it should be handled as potentially fraudulent until the operator's identity is established through an independent route.
Written analysis generated 2026-11-11 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
5 findings contributed to this verdict, raised by page content, external reputation, several checks together, history in the web archive, and registration and ownership.
When captured, this address served Cloudflare's own warning page instead of the site, so the site's own content was not captured; Cloudflare's warning is itself the evidence.
01 Page content
- When the evidence was captured, Cloudflare showed its own warning page in place of this site, telling visitors the site had been reported as harmful.Page content
rule:PAGE_CF_PHISHING_INTERSTITIAL
02 External reputation
- 7 VirusTotal engines, including a leading vendor (Fortinet, Sophos), marked this domain as malicious when the evidence was captured, which TrustSniffer counts as a confirmed external listing.External reputation
rule:EXT_BLACKLIST_CRITICAL
03 Several checks together
- Several independent checks pointed to risk at the same time.Several checks together
rule:HYB_MULTIPLE_MODULES_HIGH_RISK
04 History in the web archive
- The web archive has almost no record of this domain, which fits a site that is new.History in the web archive
rule:ARCH_PEN_YOUNG_AND_SPARSE
05 Registration and ownership
- The registration lookup did not return the domain's registrant and country.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- No contact detail, company registration number or linked social profile was extracted from the page for checking.
What TrustSniffer observed
First-party facts recorded during the assessment of pandupanda.app.
- The request stayed on pandupanda.app. It was not redirected to another domain. Clear
- Registered through NICENIC INTERNATIONAL GROUP CO., LIMITED. Noted
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The domain is registered until 2026-12-20. Noted
- The earliest public archive of this site is from 2026-02-16. Watch
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | NICENIC INTERNATIONAL GROUP CO., LIMITED |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3033::6815:46f (a CDN edge address; the server behind it was not observed) |
| Name servers | becky.ns.cloudflare.com, west.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2027-01-10 |
| Domain age | 325 days (registered 2025-12-20) |
| Domain expiry | 2026-12-20 |
| Archive first seen | 2026-02-16 (267 days before capture) |
| Archive snapshots | 1 |
| Reputation | VirusTotal: 7 malicious, 1 suspicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about pandupanda.app at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.