Verdict
Several risk patterns were present. Do not send money or personal details until you have verified this business another way.
pepememe-vip.web.app is low-trust and potentially risky.
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 3 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 3% confidenceAbuseIPDB, 4 reports; shared hosting inflates reports | Clear |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by WR4 | Noted |
| Hosted by | FASTLYServer in US | Noted |
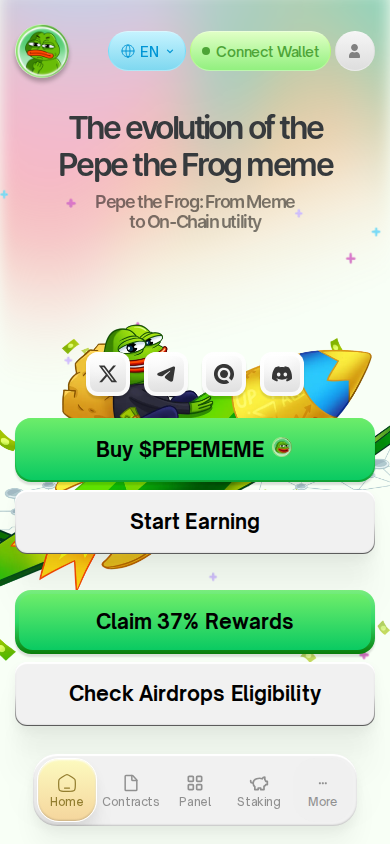
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Overview
This website is a single-page site at a subdomain of a shared web-application hosting namespace, titled "Pepe Meme", with "vip" in its hostname. Its name and branding point to a meme-token or meme-coin themed project, and it presents a short landing page with roughly a few thousand characters of text. The collected evidence does not show a clear product, service, or revenue model, so its apparent purpose is promotional or community-style engagement around a meme theme.
Scam/Impersonation Risk
This is the decisive area of concern. Several independent threat-intelligence sources currently flag the site as malicious or suspicious, and the site is blacklisted by those sources. This is a hard contradiction, and no mitigating factor offsets it. The theme is typical of a meme-token launch, a category that is often used for token-promotion scams and wallet-related lures. The behavioral testing did not observe wallet-connection prompts, clipboard manipulation, hidden forms, external credential posts, or cloaking, so no specific malicious mechanism was demonstrated during the controlled runs. That absence does not outweigh the external detections, because a page can change after the testing window. A secondary signal is a small number of abuse reports against a network address that serves this site. Those reports apply to a shared provider address used by many unrelated sites, so they carry limited weight against this site specifically. No conflicting legal identities and no brand impersonation were observed. The risk therefore stems from the blacklisting, not from identity inconsistency. Evidence:
- Homepage: external threat-intelligence sources list the domain as malicious or suspicious, and it is blacklisted.
- Homepage behavioral runs: three successful sessions showed no external requests, wallet-connect activity, clipboard writes, hidden forms, or cloaking.
- Homepage after interaction: a large burst of page-structure changes (about 1,443 DOM mutations) occurred, so the page is highly dynamic and its content can change materially.
- Network layer: four abuse reports were recorded against a shared provider address, which weakens their attribution to this site.
Regulatory Verification Notes
The evaluated page discloses no operating company, legal entity, registration number, or licensing information. Because the site uses a meme-token theme, the absence of any regulatory standing is notable, since token promotion and any associated financial activity usually fall under securities or virtual-asset rules. This is a disclosure gap in its own right. Ownership and governance are opaque: nothing on the page connects the site to an identifiable person or organization, and the operator's real-world identity could not be established. No third-party broker or regulatory reputation record was matched. The site's valid but basic certificate and clean-looking transport layer say nothing about the legitimacy of the operator. Evidence:
- Homepage: no company name, legal entity, license, or registration detail is shown.
- Hosting: served from AS54113 (Fastly, US) in ARIN-registered address space.
- Transport encryption: TLS certificate issued by WR4 (domain-validated, DV), valid to 2026-12-22, so it confirms only control of the domain, not the operator's identity.
- Third-party broker reputation: no match found, so there is neither a positive nor a negative record.
What to Verify Next
Before any interaction, the operator's identity must be established independently, since the site does not state it. Any token, contract address, or promoter claim should be checked against official project channels reached by a route that does not start from this site. Any claim of registration or licensing should be checked directly in the relevant financial or virtual-asset registry. The threat listings should be rechecked later, as they may be revised if the site is cleaned or if the listing was a false positive. Nothing should be downloaded or installed from the site while the listings remain active. Evidence:
- Homepage: no named operator or registry reference is available to check.
- Threat listings: multiple sources currently flag the domain, so the status should be rechecked before any reassessment.
- Official channels: any social or contract details the page promotes should be matched against independently sourced project information.
Summary Verdict
The overall posture is high risk. External threat detections are decisive, and the lack of a verifiable operator identity gives no counterweight. The clean behavioral runs and the valid certificate lessen concern about a specific exploit but do not support a trusted classification. The site should be treated as unsafe for any sensitive or financial interaction.
Infrastructure Integrity
The site is delivered through a recognized content-delivery and web-application-protection network, and only edge addresses were observable, so the origin server cannot be independently identified. This offers some protection against direct attacks and shows the hosting is professionally operated. It is a mitigating factor only. Edge-only visibility also means that independent hosting verification is not possible and that content can be swapped quickly without any visible infrastructure change.
Closing Assessment
The site should not be used for login, credential entry, wallet connection, or any payment or token purchase. At most, it may be viewed passively in an isolated environment. Anyone who has already interacted with it should treat any connected wallet or entered credentials as potentially exposed and take protective steps accordingly.
Written analysis generated 2026-10-27 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, registration and ownership, behaviour in a sandbox.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Registration and ownership
- The public registration record for this domain is incomplete.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
03 Behaviour in a sandbox
- The structure of the page changed sharply while it was loading.Behaviour in a sandbox
rule:BEHAV_DOM_DENSITY_SPIKE
Signals weighed against the site
- AbuseIPDB: 4 reports on hosting IP 2620:0:890::100 (Google LLC, Content Delivery Network), 3% confidence. The reports are attributed to shared infrastructure, not specifically to this website.
Identity verification
| Status | UNKNOWN |
|---|---|
| Identity score | 50/100 |
| Identity verification confidence | 30% |
- AI page analysis unavailable (page captured; identity not AI-verified)
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of pepememe-vip.web.app.
- The request stayed on pepememe-vip.web.app. It was not redirected to another domain. Clear
- It is hosted on FASTLY, from a server in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | FASTLY - Fastly, Inc., US |
| Country | US |
| Server IP | 2620:0:890::100 |
| Name servers | Not available |
| CDN / edge network | Detected (fastly) |
| Resolved IP addresses | 2 |
| Edge IP addresses | 2 |
| Likely origin IP addresses | 0 |
| SSL issuer | WR4 |
| SSL expiry | 2026-12-22 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 3 flagged | AbuseIPDB: 3% confidence, 4 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about pepememe-vip.web.app at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.