Verdict
An external threat listing named this site as malicious when the evidence was captured. Do not pay or share personal details with this site.
plume.us.org shows critical-risk indicators.
- Sensitive Interaction Risk: This label is given when the overall risk is high. The captured page did not ask for a password, card number or other sensitive details; if it ever does, entering them here could be unsafe.
- Governance Risk: The governance checks raised a concern: a threat-intelligence listing limits the score; the registration lookup returned no registration details for the domain. The findings below give the detail.
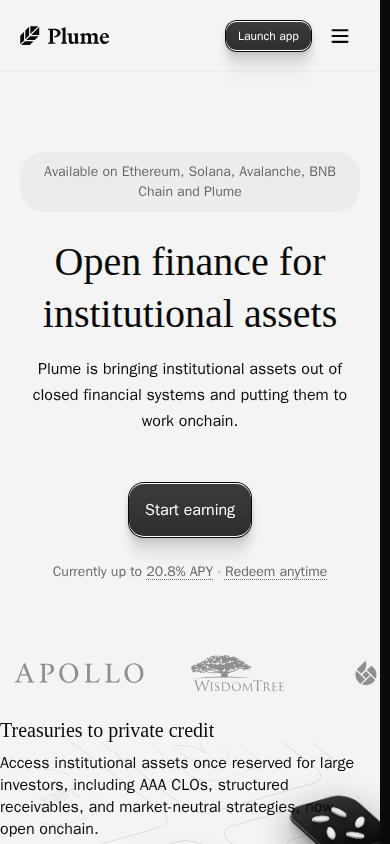
| How the site describes itself | Plume is a DeFi platform that offers stablecoin deposits into tokenized real-world asset vaults advertised at up to 20.8% APY, with leverage, borrowing, and yield-trading options, while claiming Bermuda licensing and institutional partnerships that the page does not independently verify. |
|---|
Evidence status and limitations
Evidence completeness: PartialThis says whether every check on the site was recorded as finished. At least one check failed or returned no result.
- The evidence was captured on 2026-10-22 and re-scored on 2026-11-16. The certificate, the registration age and the page content describe the site as it was on 2026-10-22.
- One external source flagged this site when the evidence was captured (a threat-intelligence listing from a feed TrustSniffer monitors (phishing, the site itself as the source, last seen 2026-10-19)). No second source confirms it. The alert is from the evidence captured on 2026-10-22; it was not re-queried for this version and is treated as unconfirmed. On its own the alert would limit the score to at most 49; the threat-listing ceiling holds it at 5, because the listing names the site itself as the source.
- The real-world operator identity was not independently verified.
- These checks returned no result: domain registration record (WHOIS), name servers (DNS), web archive lookup.
How to read these numbers
The trust score runs from 0 to 100, higher is safer. 5/100 rates the evidence found, not the probability that the site is a scam.
Evidence confidence (55%) measures how much of TrustSniffer's evidence set this site produced: the page reading, the browser sandbox, the web archive, the registration record and the reputation services. It falls when a check returns nothing, as listed above, and it does not change the score.
At a glance
The checks that decide most of this verdict.
| What limits the score | Threat-listing ceilingA threat-intelligence feed TrustSniffer monitors listed this site itself as the source of a threat when the evidence was captured (last seen 2026-10-19), and that listing caps the score. The unconfirmed alert ceiling (at most 49) also applies, but the score is below it. | Risk |
|---|---|---|
| Malware engines | None malicious; 1 marked it suspiciousVirusTotal | Watch |
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the CDN edge address | 0% confidenceAbuseIPDB, 0 reports; this is the record of the CDN edge address, not of the server behind it, which was not observed | Noted |
| Domain age | Not availableNo registration record was returned | Noted |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
| Hosted by | CLOUDFLARENETNetwork registered in US | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk, Governance Risk.
- No security engine marked this domain as malicious; some marked it suspicious, which TrustSniffer does not count as a listing.
- The operator behind the site could not be independently connected to a real-world brand or person.
Full analysis
Overview
The website presents itself as Plume, a decentralised-finance platform marketed under the banner "Open Finance for Institutional Assets". Its homepage invites visitors to deposit stablecoins into vaults described as holding tokenized real-world assets in exchange for a variable yield. It also offers token staking, asset-issuance and distribution services, and a "Launch app" entry point. Its apparent business model is deposit-based yield generation for individual and institutional users, with borrowing and yield-trading products layered on top.
Scam/Impersonation Risk
This address carries critical risk. A threat-intelligence feed recorded it as an actor distributing phishing, last seen on 19 October 2026, three days before the page was captured on 22 October 2026. That listing is what holds the score down, through the threat-listing ceiling. VirusTotal, which is a single source, gave a much weaker result. One engine rated the address suspicious, no engine rated it malicious, and Google Safe Browsing did not list it, so that result is not a detection. The captured homepage contained no forms of any kind and sent no data to other hosts, so TrustSniffer observed no credential-capture mechanism on the page as captured. The listing remains the main finding on this address. The domain name carries the Plume brand name, but TrustSniffer did not independently establish that this address is operated by the project of that name. No conflicting legal identities and no brand-impersonation indicators were observed on the page read.
The offer itself raises further concern. The homepage advertises yields of up to 20.8% APY on stablecoin deposits (USDC, USDT and the platform's own pUSD). It claims the vaults "outperform market rates" and promotes leverage of up to 6.7x through Morpho and Pendle. It also advertises availability across Ethereum, Solana, Avalanche, BNB Chain and Plume's own network. Funds must be deposited before any return is delivered, and the page gives no breakdown of where the yield comes from. A headline return of this size paired with leverage and no stated source of yield leaves a depositor unable to judge the risk of loss.
- Threat-intelligence listing record: address recorded as a phishing actor, last seen 2026-10-19, evidence captured 2026-10-22.
- VirusTotal: 0 engines malicious and 1 engine suspicious; Google Safe Browsing did not list the address.
- Homepage: yield of "up to 20.8% APY", "outperform market rates", leverage "up to 6.7x" and a five-network availability line.
- Homepage behaviour capture: 0 forms and 0 requests sending data to other hosts across 3 runs.
Regulatory Verification Notes
The homepage names Kimber Labs Inc. as the legal entity. That name has not been checked against any company register, and the real-world operator remains unverified. The site also says it holds a licence from the Bermuda Monetary Authority. On the pages read (the homepage only), no licence number, licensing-authority reference or register link accompanies that claim, so it is a statement the site makes and not a verified status. For a platform that takes stablecoin deposits, three expected disclosures were absent on the pages we read: contract addresses, a risk warning, and terms or a privacy policy. The homepage also does not state its fee structure, who operates the assets held in the vaults, or how deposited funds are kept in custody. No broker-reputation record was matched for this address, so there is no third-party reputational signal in either direction.
- Homepage: names Kimber Labs Inc. as the legal entity and asserts a Bermuda Monetary Authority licence, with no licence number.
- Homepage: no contract address, risk warning, or terms or privacy page found on the pages read.
- Hosting record: served from AS13335 (Cloudflare, Inc., US).
- TLS certificate: domain-validated (DV) certificate issued by WE1, valid to 2026-12-02 when seen at capture.
What to Verify Next
Any licence claim should be checked directly in the Bermuda Monetary Authority's public register, searching by entity name and by licence number. A search for Kimber Labs Inc. in a corporate registry would test the named entity. The connection between this address and the Plume project should be established from official channels reached independently of this site, for example through a published project address obtained elsewhere. Contract addresses for the vaults and tokens should be sourced from independent documentation and inspected on a public block explorer before any interaction. The partnership and deposit claims should be confirmed with the named institutions' own channels.
- Homepage: names Apollo, EtherFi and Bybit as partners, cites "$100M into Plume Vaults" for EtherFi, and carries a New York Times feature dated 17 December 2025. None of these claims is independently corroborated.
- Homepage menu: links to regulation and documentation pages, which were not read in this analysis.
- Homepage: social links to X, Telegram and Discord are presented as the community channels.
Summary Verdict
The overall posture is critical risk. The site presents a polished, content-rich institutional-finance front, but that presentation does not offset a phishing-class threat listing. It also does not offset a deposit-first, high-yield model whose legal status, custody and operator remain unconfirmed. The evidence indicates critical risk for this address.
Infrastructure Integrity
The site is served through Cloudflare's content delivery network, and all four observed addresses are edge addresses, so the origin server was not observed and the underlying host cannot be attributed. The presence of a CDN is neutral. It neither raises nor lowers risk and does not bear on the legitimacy of the operator. The host address's abuse record was checked and showed no reports.
Closing Assessment
Stablecoin deposits, wallet connections and token approvals through this address should be avoided entirely, and browsing should stay read-only. Anyone who wants to reach the Plume project should do so through channels obtained independently of this address.
Written analysis generated 2026-11-16 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
6 findings contributed to this verdict, raised by governance, page content, and registration and ownership.
01 Governance
- A threat-intelligence feed TrustSniffer monitors listed this site itself as the source of a threat when the evidence was captured (last seen 2026-10-19), and that listing caps the score.Governance
rule:gov_active_threat_listing
02 Page content
- The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page is about crypto and names several tokens, and it is not a news, education or documentation page.Page content
rule:PAGE_CRYPTO_TOKEN_HEAVY - The page has no description for search engines, which established sites usually provide.Page content
rule:PAGE_SEO_MISSING_META - The page carries none of the structured previews for search and social sharing that established sites usually provide.Page content
rule:PAGE_SEO_NO_STRUCTURED
03 Registration and ownership
- The registration lookup returned no registration details for the domain.Registration and ownership
rule:KF_WHOIS_INCOMPLETE
How related findings were counted
Some findings above describe the same underlying fact, and some are weak on their own. TrustSniffer counts each such group under one shared limit, so one fact is not counted several times and weak signals stay bounded.
- Certificate and search-engine setup: 2 findings share one limit, because none of them is a sign of fraud on its own. Together they stayed under the limit.
Identity verification
| Status | UNVERIFIED |
|---|
The operator behind the site could not be connected to a real-world brand or person. What the page shows, if anything, is listed below; none of it was independently checked.
- Legal entity named on the page: Kimber Labs Inc. (not checked against a register)
What TrustSniffer observed
First-party facts recorded during the assessment of plume.us.org.
- The request stayed on plume.us.org. It was not redirected to another domain. Clear
- It is hosted on CLOUDFLARENET, a network registered in US. Noted
Domain intelligence
| Registrar | Not available |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc. |
| Network registered in | US |
| Server IP | 2606:4700:3031::ac43:b9bc (a CDN edge address; the server behind it was not observed) |
| Name servers | Not available |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 4 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 0 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-02 |
| Domain age | Not available (no registration date was returned) |
| Domain expiry | Not available |
| Archive first seen | Not available |
| Archive snapshots | Not counted (archive lookup incomplete) |
| Reputation | VirusTotal: 0 malicious, 1 suspicious | AbuseIPDB (CDN edge address, not the host): 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about plume.us.org at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A high score means the signals were consistent with a legitimately operated site; a low or critical score means several risk patterns were present. It is a starting point for your own judgement, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.