Verdict
polarclient.net shows high-risk / scam indicators.
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
| What this site appears to be | A site offering a cracked Polar Client mod for Hypixel SkyBlock (Fabric 26.2 and 1.21.11). Describes automation features (mining bots, ESP/XRay, macros) and provides download/install instructions. Claims 'failsafe' anti-detection and free distribution; limited author verification and potential security risk from running cracked binaries. |
|---|
Evidence status and limitations
Evidence completeness: UNKNOWN
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 14 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 6 months oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 202619 snapshots | Clear |
| Certificate | Encrypted connectionIssued by YR1 | Noted |
The page as captured
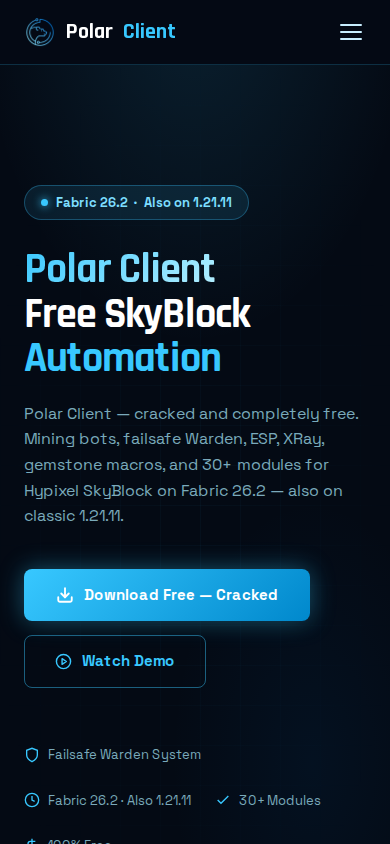
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2026.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Fortinet, Kaspersky, Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
Polarclient.net presents itself as a free-download site for the cracked Polar Client Minecraft Fabric modification, aimed at Hypixel SkyBlock players seeking automation and cheating functionality. Its apparent business model is the distribution of executable `.jar` files, potentially supported indirectly through advertising or donations.
Scam/Impersonation Risk
The site presents a critical sensitive-interaction risk. No conflicting legal identities or direct brand-impersonation claim was observed, but the site is subject to confirmed blacklisting and multiple external malware detections, including 14 malicious and 3 suspicious classifications across evaluated security services. This is materially reinforced by the homepage’s promotion of a cracked client, executable downloads, anti-detection claims, Discord webhook functionality, and instructions to install and run the software. The claims that the client is “failsafe” and able to detect known macro checks are not supported by independently verifiable authorship or safety evidence; running an untrusted binary creates a direct malware and account-security exposure.
- The homepage advertises “Polar Client — cracked and completely free,” with mining bots, “failsafe Warden,” ESP, XRay, gemstone macros, and more than 30 modules.
- The homepage provides download and installation instructions for Fabric 26.2 and Minecraft 1.21.11, including executable client distribution.
- External security assessment recorded 14 malicious and 3 suspicious detections; blacklist status was confirmed by two evaluated sources.
- The domain was registered in 2026 and is approximately 0.47 years old; archival coverage records 19 snapshots spanning 2026–2026, with 1 year tracked.
Regulatory Verification Notes
The available material does not independently verify the real-world operator or establish a responsible publisher for the software. The site’s disclosure position is unclear, and the page-level assessment identifies unverified contact or authorship information, a significant evidence gap for software whose installation requires execution on a user device, and no clear independently verifiable product provenance. These are verification deficiencies rather than separate proof of impersonation, but they leave no reliable basis for treating the publisher as an accountable software provider. No broker or regulated-financial-entity association was identified in the supplied third-party context.
- The homepage identifies the product as a cracked Polar Client but does not provide independently verified author or publisher credentials.
- The homepage contains no visible sensitive form or account-login mechanism; its principal interaction is software download and installation.
- The site is hosted on AS214351 through FEMOIT - FEMO IT SOLUTIONS LIMITED, GB; the resolved infrastructure is registered through AFRINIC and associated with SC.
- The site’s TLS certificate is issued by YR1 at DV validation level and is valid through 2026-12-20.
What to Verify Next
Any prospective deployment should first obtain the publisher’s identity and software provenance through an independent channel, then compare the file’s cryptographic hash with a release record maintained outside the site. The binary should be analyzed in an isolated environment by qualified security personnel before any execution, and any associated Discord, Minecraft, or system credentials should remain segregated from testing. Licensing, distribution rights, and the applicable game-platform rules should also be confirmed independently. If the publisher cannot provide verifiable provenance and accountable support channels, the software should not be introduced into an enterprise or personal production environment.
- The homepage directs users to download and install a cracked `.jar` client rather than presenting a conventional hosted service.
- The homepage claims anti-detection behavior and advertises Discord webhook notifications, creating a need to inspect both the binary and its outbound capabilities.
- The page-level assessment records four concerns: unverified contact or address information, claim-evidence dissonance, a high-stakes evidence gap, and no clear product verification.
Summary Verdict
The site has a critical risk posture and is not suitable for credentialed, financial, or other sensitive interaction. The combination of confirmed blacklist status, malware detections, unverified operator identity, and distribution of cracked executable software outweighs the limited benign indicators observed during technical inspection.
Infrastructure Integrity
The site resolves directly to a single origin rather than a detected CDN or WAF edge, so there is no identified intermediary protection reducing exposure of the hosting endpoint. Transport encryption is present, but a DV certificate confirms encrypted delivery only and does not authenticate the operator or establish software safety.
Closing Assessment
The appropriate action is to suspend downloading or execution, preserve any acquired files for controlled security analysis, and require independent publisher verification before considering any further interaction.
Written analysis generated 2026-10-01 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
3 findings contributed to this verdict, raised by external reputation, page content, hosting and network.
01 External reputation
- An external threat feed lists this domain: either Google Safe Browsing marked it malicious, or a significant number of malware engines flagged it.External reputation
rule:EXT_BLACKLIST_CRITICAL
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The page content shows at least one warning sign that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_SOME - The browser raised a warning while loading the page.Page content
rule:PAGE_BROWSER_FLAGS_SUSPICIOUS
03 Hosting and network
- The domain was registered between three and six months ago.Hosting and network
rule:DNS_YOUNG_6M
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 25% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of polarclient.net.
- The request stayed on polarclient.net. It was not redirected to another domain. Clear
- Registration is published under Internet Domain Service BS Corp.. Clear
- DNS for this domain is served by topdns.com, across 3 name servers. Noted
- The registration is paid up to 2028-04-12. Clear
- The earliest public archive of this site is from 2026-04-16. Clear
- It is hosted on FEMOIT, from a server in SC. Noted
Domain intelligence
| Registrar | Internet Domain Service BS Corp. |
|---|---|
| Hosting | FEMOIT - FEMO IT SOLUTIONS LIMITED, GB |
| Country | SC |
| Server IP | 196.251.107.204 |
| Name servers | NS-CANADA.TOPDNS.COM, NS-UK.TOPDNS.COM, NS-USA.TOPDNS.COM |
| CDN / edge network | Not detected |
| Resolved IP addresses | 1 |
| Edge IP addresses | 0 |
| Likely origin IP addresses | 1 |
| SSL issuer | YR1 |
| SSL expiry | 2026-12-20 |
| Domain age | 0.47 years (continuous registration) |
| Domain expiry | 2028-04-12 |
| Archive first seen | 2026-04-16 |
| Archive snapshots | 19 |
| Reputation | VirusTotal: 14 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about polarclient.net at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.