Verdict
This assessment found strong scam indicators. Do not pay, sign in, or share personal details with this site.
polinex.org shows high-risk / scam indicators.
| What this site appears to be | Polinex is a site offering a free Minecraft Fabric mod that automates Hypixel Skyblock mining and advertises advanced anti-detection and dynamic failsafes. The page focuses on features, downloads, and community testimonials. It lacks verifiable third-party evidence for anti-detection claims and provides limited transparency about safety or provenance. |
|---|
Evidence status and limitations
Evidence completeness: Not recorded
- The real-world operator identity was not independently verified.
- Module-level completeness metadata is unavailable for this legacy report.
At a glance
The checks that decide most of this verdict.
| Malware engines | 4 flagged itVirusTotal | Risk |
|---|---|---|
| Google Safe Browsing | Not listedGoogle | Clear |
| Abuse reports on the host | 0% confidenceAbuseIPDB, 0 reports; shared hosting inflates reports | Clear |
| Domain age | 18 days oldMost scam domains are under a year old | Risk |
| Web archive | Archived since 200474 snapshots | Clear |
| Certificate | Encrypted connectionIssued by WE1 | Noted |
The page as captured
Key findings
- Automated classification: Sensitive Interaction Risk.
- Domain age: less than 1 year (registration continuity).
- Public web-archive history exists since 2004.
- At least one reputation service TrustSniffer consulted had flagged this domain at assessment time.
Full analysis
Security Alert
Sophos flagged this site in external intelligence checks, indicating elevated compromise/scam exposure that requires immediate caution.
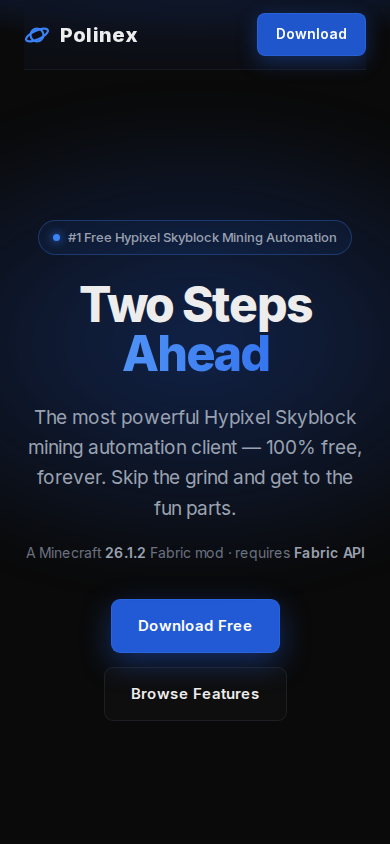
Polinex is a product-and-download website offering a free Minecraft Fabric mod for automating Hypixel Skyblock mining, including commission macros, configurable modules, automatic updates, anti-detection features, and dynamic failsafes; its apparent model is free distribution of game-automation software supported by an unspecified community or support mechanism.
Scam/Impersonation Risk
The site presents a downloadable client that claims to be “undetectable,” to bypass watchdog measures, maintain a “low ban rate,” and provide more than 120 modules, while offering no independently verifiable evidence for those safety and anti-detection claims. The homepage also promotes automatic updates and ready-to-use macros, which increases the importance of establishing the provenance and integrity of the distributed software. External reputation evidence includes multiple malicious detections and confirmed blacklist status; this is the decisive contradiction and makes downloading or executing the client unsuitable for sensitive environments. No confirmed conflicting legal identities or explicit brand impersonation were observed, but the combination of external threat detections, unverifiable claims, and limited provenance information creates a clearly elevated risk posture.
- External reputation assessment recorded 4 malicious detections, including a tier-one threat detection, and confirmed blacklist status.
- The homepage advertises “Advanced anti-detection bypassing all watchdog measures,” “Dynamic Failsafes,” automatic updates, and “120+” modules without cited independent validation.
- Archive records show 74 snapshots spanning 2004-11-12 through 2025-04-09, covering 22 years, with a reconciled domain age of 21.916495550992472 years.
Regulatory Verification Notes
The site is a game-automation download service rather than an identified financial or regulated service. Its pages do not establish a verifiable operating entity, licensing basis, ownership structure, or clear monetization model; the available identity evidence therefore remains unverified. This is a material transparency gap for software distribution, although the absence of a stated license is not by itself proof of fraud. The page-level presentation also provides limited information about software provenance, safety testing, support accountability, or the entity responsible for updates. A valid transport certificate and mainstream hosting infrastructure are technical protections only and do not establish operator legitimacy.
- The homepage identifies the product as a Minecraft 1.21+ Fabric mod requiring Fabric API and provides a “Download Free” path, but does not identify a verifiable operating company or licensing authority.
- The site’s transport certificate is issued by WE1, uses DV validation, and is valid to 2026-12-22T16:20:07+00:00.
- Hosting is served from AS13335, CLOUDFLARENET - Cloudflare, Inc., US.
What to Verify Next
Before any download or execution, an enterprise should independently identify the operator, obtain a verifiable software publisher identity and release history, and inspect the file in an isolated malware-analysis environment. The installer or mod should be checked for a reproducible cryptographic hash, update endpoints, embedded credentials, persistence, and unexpected network activity. Any proposed support or community channel should be confirmed through an independently sourced route rather than relying solely on the website. Account credentials, production gaming accounts, and corporate devices should not be exposed to the software unless these checks produce satisfactory results.
- The homepage contains no login form or sensitive-data form, so apparent absence of credential collection should not be treated as evidence that the downloadable software is safe.
- Behavioral testing recorded 3 successful runs, 0 external XHR requests, 0 non-whitelisted external posts, and no detected clipboard-write activity.
- The page is classified as a product/download service and was observed to provide downloadable executable content while promoting conduct that may violate the relevant game platform’s rules.
Summary Verdict
The overall posture is critical trust risk. The site’s apparent purpose is clear, but its operator identity and software provenance are not independently established, while confirmed external threat detections and blacklist status materially outweigh the site’s otherwise stable presentation and basic technical protections. It is not appropriate for sensitive interaction or trusted software acquisition.
Infrastructure Integrity
Cloudflare CDN/WAF protection provides a mitigating layer against direct exposure of the application infrastructure, but it is shared protective infrastructure and cannot validate the site operator, downloaded content, or stated claims. Observed infrastructure included CDN edge addresses and a potential origin candidate, so the protective layer should be treated as containment support rather than evidence of legitimacy.
- The site is protected by Cloudflare CDN/WAF infrastructure, with four observed CDN edge addresses and one potential origin candidate.
- The hosting organization is CLOUDFLARENET - Cloudflare, Inc., US, as reflected in the observed hosting path.
Closing Assessment
The proportionate action is to avoid downloading or executing the client on production, corporate, or credential-bearing systems until independent publisher verification and isolated software analysis have been completed.
Written analysis generated 2026-10-13 by the TrustSniffer Analysis Engine from the evidence in this report.
What the analysis found
2 findings contributed to this verdict, raised by external reputation, page content.
01 External reputation
- Several malware engines flagged this domain.External reputation
rule:EXT_BLACKLIST_HIGH
02 Page content
- The page shows few of the signs expected from a trustworthy operator.Page content
rule:PAGE_TRUST_QUALITY_LOW - The page content shows three or more warning signs that deceptive sites commonly use.Page content
rule:PAGE_RED_FLAGS_STRONG - The review of the page content rated it moderate risk.Page content
rule:PAGE_RISK_MED - The page appears to present itself as a known brand it is not verified to belong to.Page content
rule:PAGE_BRAND_SUSPECTED
Identity verification
| Status | UNVERIFIED |
|---|---|
| Identity score | 30/100 |
| Identity verification confidence | 50% |
- No on-site identity signals detected
Identity verification measures whether the site can be independently connected to a real-world brand or person. It is separate from the classification confidence.
What TrustSniffer observed
First-party facts recorded during the assessment of polinex.org.
- The request stayed on polinex.org. It was not redirected to another domain. Clear
- Registration is published under Cloudflare, Inc.. Clear
- DNS for this domain is served by cloudflare.com, across 2 name servers. Noted
- The registration is paid up to 2027-09-23. Noted
- The earliest public archive of this site is from 2004-11-12. Clear
- It is hosted on CLOUDFLARENET, from a server in US. Noted
Domain intelligence
| Registrar | Cloudflare, Inc. |
|---|---|
| Hosting | CLOUDFLARENET - Cloudflare, Inc., US |
| Country | US |
| Server IP | 2606:4700:3035::6815:4f58 |
| Name servers | melody.ns.cloudflare.com, scott.ns.cloudflare.com |
| CDN / edge network | Detected (cloudflare) |
| Resolved IP addresses | 5 |
| Edge IP addresses | 4 |
| Likely origin IP addresses | 1 |
| SSL issuer | WE1 |
| SSL expiry | 2026-12-22 |
| Domain age | 0.05 years (continuous registration) |
| Domain expiry | 2027-09-23 |
| Archive first seen | 2004-11-12 |
| Archive snapshots | 74 |
| Reputation | VirusTotal: 4 flagged | AbuseIPDB: 0% confidence, 0 reports | Google Safe Browsing: 0 matches |
About this assessment
A trust score summarises the evidence TrustSniffer could collect about polinex.org at assessment time. It is a starting point for your own judgement, not a guarantee: a high score means the signals were consistent with a legitimately operated site, a low or critical score means several risk patterns were present.
TrustSniffer assesses a website from the evidence it can collect at a point in time: domain registration and age, hosting and certificate, the content the site served, and third-party reputation feeds. A score is a summary of that evidence, not a guarantee and not a legal finding. There is no human rating and no user review in it. A site can change after it is assessed.